
Every organization depends on computers, networks, applications and digital information. From personal email accounts to enterprise databases, these systems need protection against unauthorized access, data theft, disruption and misuse.
This is where cybersecurity comes in.
Cybersecurity is the practice of protecting systems, networks, applications and data from digital threats. But to understand how cybersecurity works, beginners must first learn a few fundamental concepts.
Four particularly important areas are the CIA Triad, threats, vulnerabilities and risk. These concepts form the foundation of security assessments, penetration testing, incident response and defensive security.
Let’s explore each one.
NEW TO ETHICAL HACKING?
Start your ethical hacking journey with our FREE Beginner Ethical Hacker Starter Kit (2026 Edition).
Get beginner-friendly guidance to understand the fundamentals of ethical hacking and take your first steps into cybersecurity.
What Is Cybersecurity?
Cybersecurity refers to the technologies, processes and practices used to protect digital systems and information against cyberattacks and unauthorized activities.
Its purpose is not simply to prevent hackers from accessing computers. It also involves ensuring that information remains accurate, services remain available and only authorized individuals can access sensitive resources.
For example, consider an online banking platform. It must protect customer information, prevent unauthorized transactions and remain accessible when customers need it. To achieve these goals, security professionals rely on several fundamental security principles.
Understanding the CIA Triad
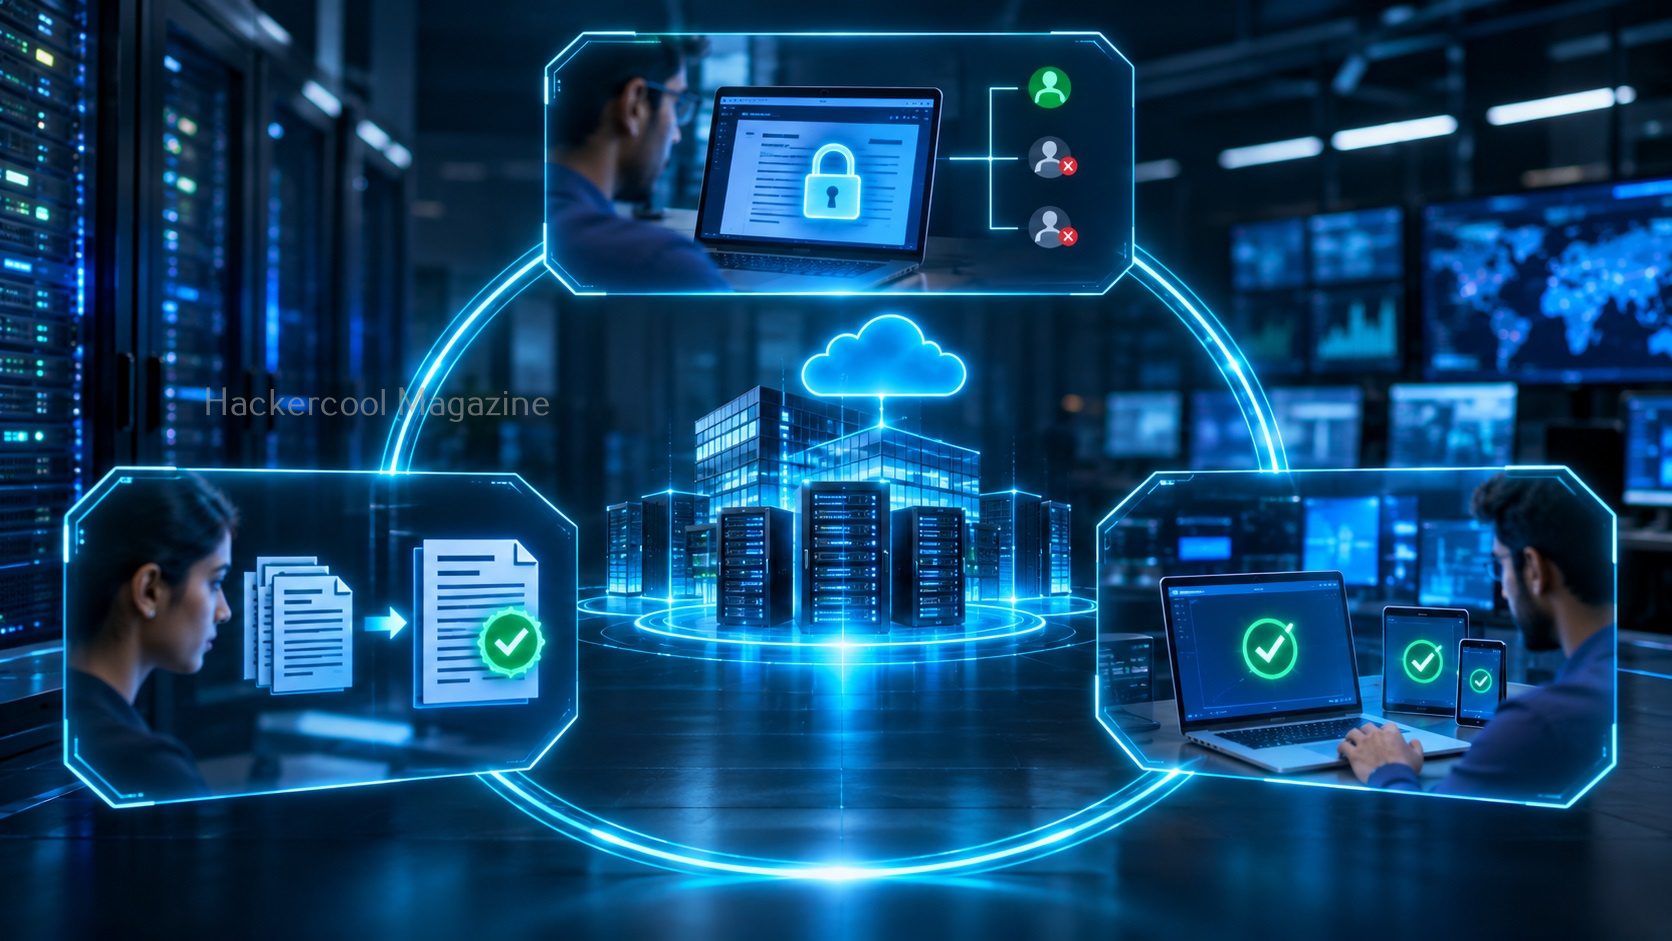
The CIA Triad is one of the most important concepts in cybersecurity. It represents three essential security objectives:
- Confidentiality
- Integrity
- Availability
Together, these principles help organizations design, implement and evaluate security controls.
1. Confidentiality
Confidentiality ensures that information is accessible only to authorized individuals, systems or processes. For example, a customer’s banking information should only be accessible to the customer and authorized banking personnel.
If an attacker steals login credentials and accesses private customer records, confidentiality has been compromised.
Common measures used to protect confidentiality include:
- Access control and permissions
- Strong authentication
- Multifactor authentication (MFA)
- Data encryption
- Secure communication protocols
2. Integrity
Integrity ensures that information remains accurate, complete and protected against unauthorized modification. Imagine an attacker changing the account balance stored in a banking database. Even if the attacker does not steal the data, modifying it without authorization violates integrity.
Organizations use several controls to maintain integrity:
- File integrity monitoring
- Cryptographic hashes
- Digital signatures
- Access permissions
- Database controls
- Audit logs
For example, a cryptographic hash can help detect whether a file has changed. A digital signature can help verify the authenticity and integrity of signed information.
3. Availability
Availability ensures that systems, applications and information remain accessible to authorized users when needed. Consider an online shopping website. If customers cannot access it because its servers have failed or are experiencing a denial-of-service attack, availability has been affected.
Organizations protect availability through:
- Regular backups
- Redundant infrastructure
- Load balancing
- Disaster recovery planning
- System monitoring
- DDoS protection
The CIA Triad provides a useful way to understand the security objectives of almost any digital system.
What Is a Cybersecurity Threat?
A threat is anything that has the potential to cause harm to a system, network, application or information. Threats may come from malicious individuals, organized cybercriminal groups, insiders or accidental events.
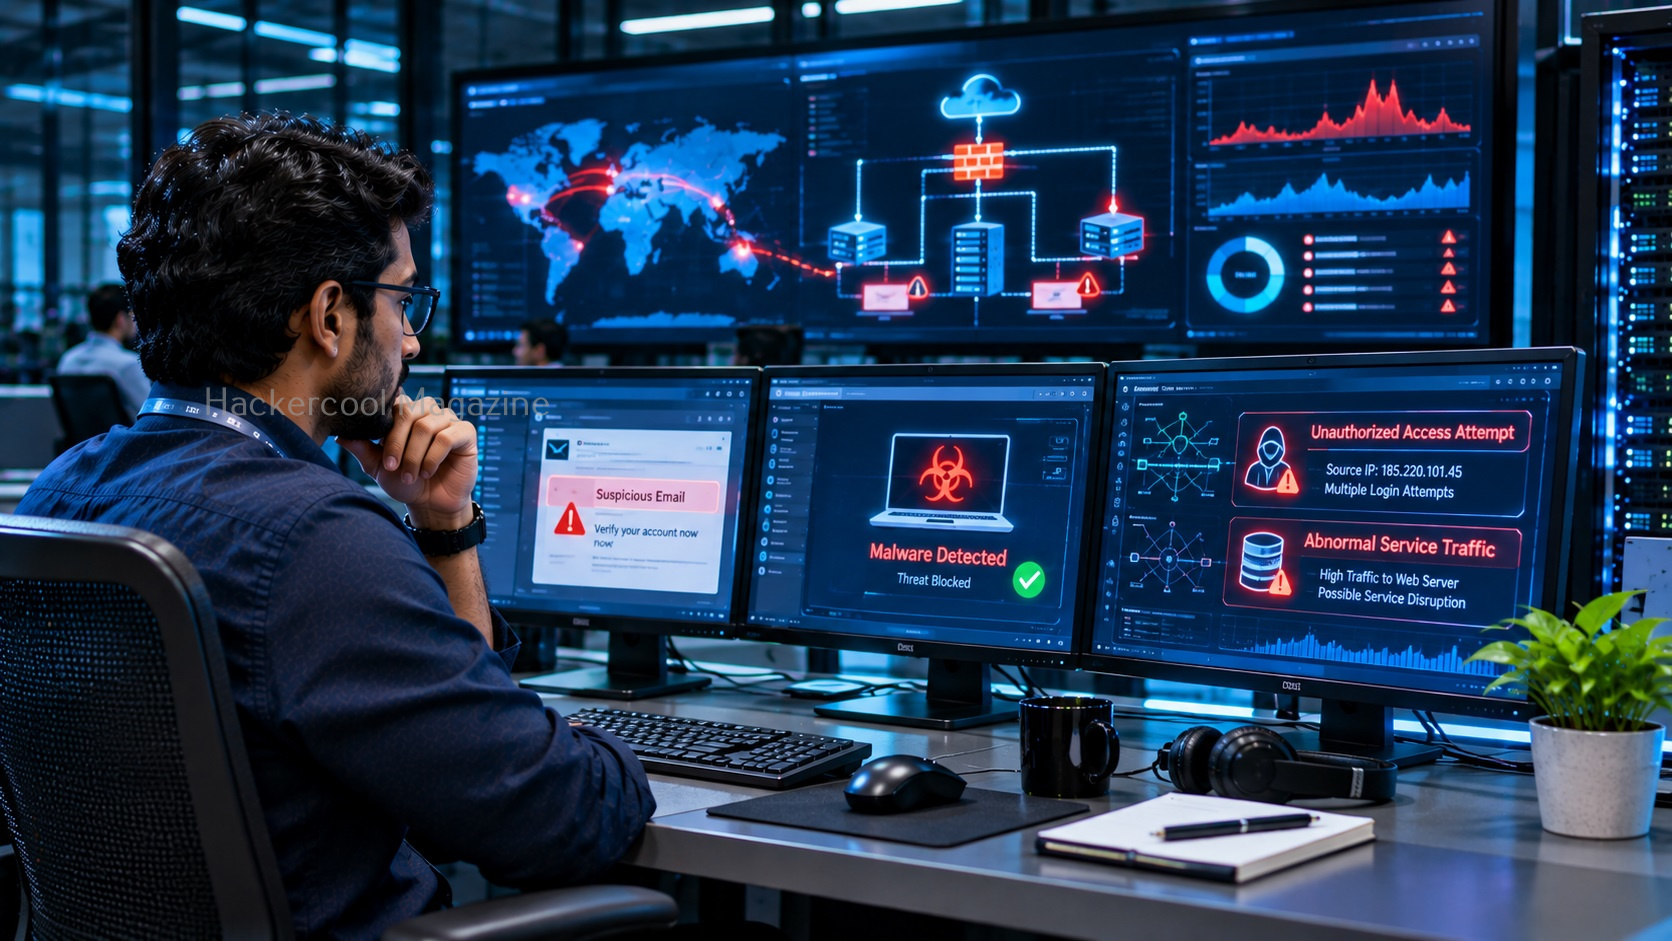
Common cybersecurity threats include:
1. Malware:
Malicious software such as ransomware, spyware, trojans and worms can compromise devices, steal information or disrupt operations.
2. Phishing:
Attackers use deceptive emails, messages or websites to trick individuals into revealing credentials or performing unsafe actions.
3. Password attacks:
Weak, reused or exposed passwords can allow unauthorized access to accounts.
4. Denial-of-Service attacks:
DoS and DDoS attacks attempt to disrupt the availability of services by overwhelming or exhausting resources.
5. Insider threats:
Employees, contractors or other trusted individuals may intentionally or accidentally expose sensitive information or misuse access.
Attackers manipulate people into disclosing information, granting access or performing actions that compromise security.
A threat does not necessarily mean that a system has already been compromised. It represents the possibility of harm.
READY TO BUILD YOUR ETHICAL HACKING FOUNDATIONS?
Go beyond the basics. Develop the essential knowledge every aspiring ethical hacker needs.
Your learning package includes:
Networking Fundamentals
Linux Fundamentals
Windows Fundamentals
Web Fundamentals
Command Line Essentials
Virtual Labs
$1 INTRODUCTORY TRIAL
6 Foundation Resources + Full Magazine Access
Trial terms apply. Post-trial subscription billing is manual.
What Is a Vulnerability?
A vulnerability is a weakness in a system, application, network, configuration or security process that could be exploited by a threat. For example, an outdated web application may contain a security flaw that allows unauthorized access. Similarly, a server with weak access permissions may expose sensitive files.
Common vulnerabilities include:
- Outdated operating systems and applications
- Weak passwords
- Misconfigured firewalls
- Unnecessary open network services
- Insecure access permissions
- Unpatched software flaws
- Poorly secured web applications
- Missing or ineffective security controls
Vulnerabilities may result from software coding errors, configuration mistakes, weak security practices or failure to apply updates. Security professionals identify vulnerabilities through activities such as vulnerability scanning, configuration reviews, code analysis and authorized penetration testing.
However, identifying a vulnerability does not automatically mean that an attacker can exploit it. Its exploitability depends on factors such as system configuration, network exposure, existing controls and attacker capabilities.
Understanding Cybersecurity Risk
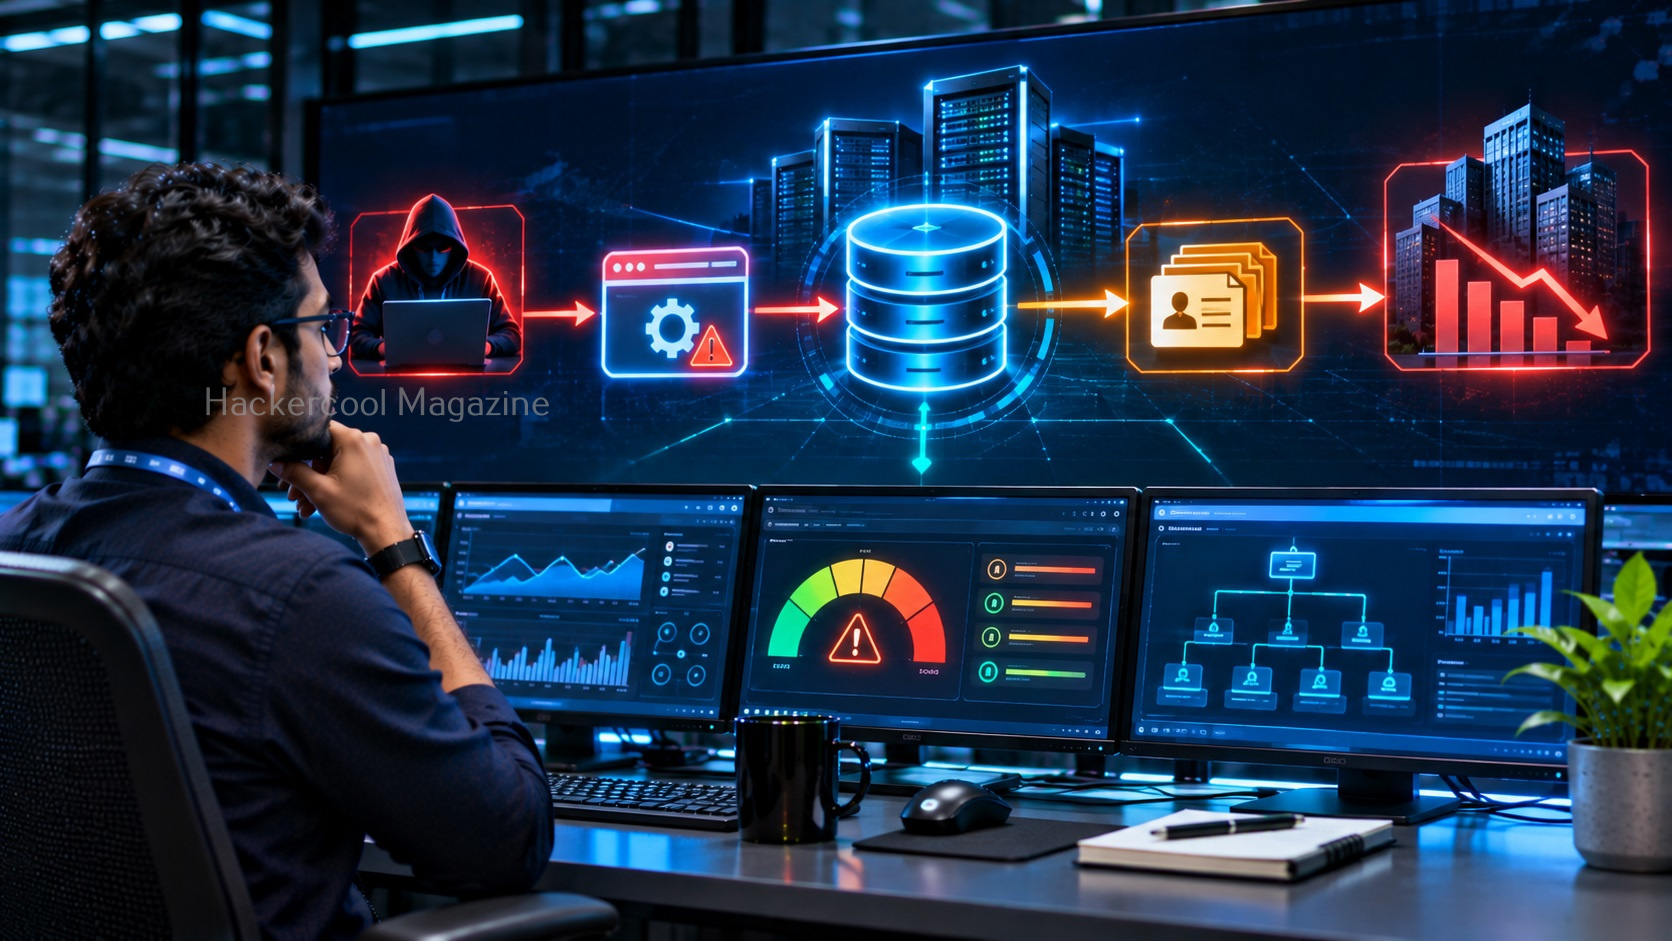
Risk refers to the potential for loss or harm when a threat exploits a vulnerability and affects an asset. In simple terms, risk helps organizations understand how likely a security incident is and how serious its consequences could be.
For example, consider a company operating an internet-facing web application with an unpatched security vulnerability.
- Asset: The company’s web application and customer database.
- Threat: A malicious attacker.
- Vulnerability: An exploitable software flaw.
- Impact: Unauthorized access to customer information.
- Risk: Potential data exposure, financial loss, and reputational damage.
A commonly used simplified risk model is:
Risk = Likelihood × Impact
This is a conceptual model rather than a universal measurement formula. Organizations may use qualitative ratings, numerical scoring or more detailed risk assessment methods. For example, a vulnerability with a high likelihood of exploitation and severe business consequences may require immediate attention.
Another vulnerability may have a lower likelihood or limited impact and therefore receive a lower priority. Risk assessment helps security teams decide which issues should be addressed first.
How Threats, Vulnerabilities and Risk Are Connected
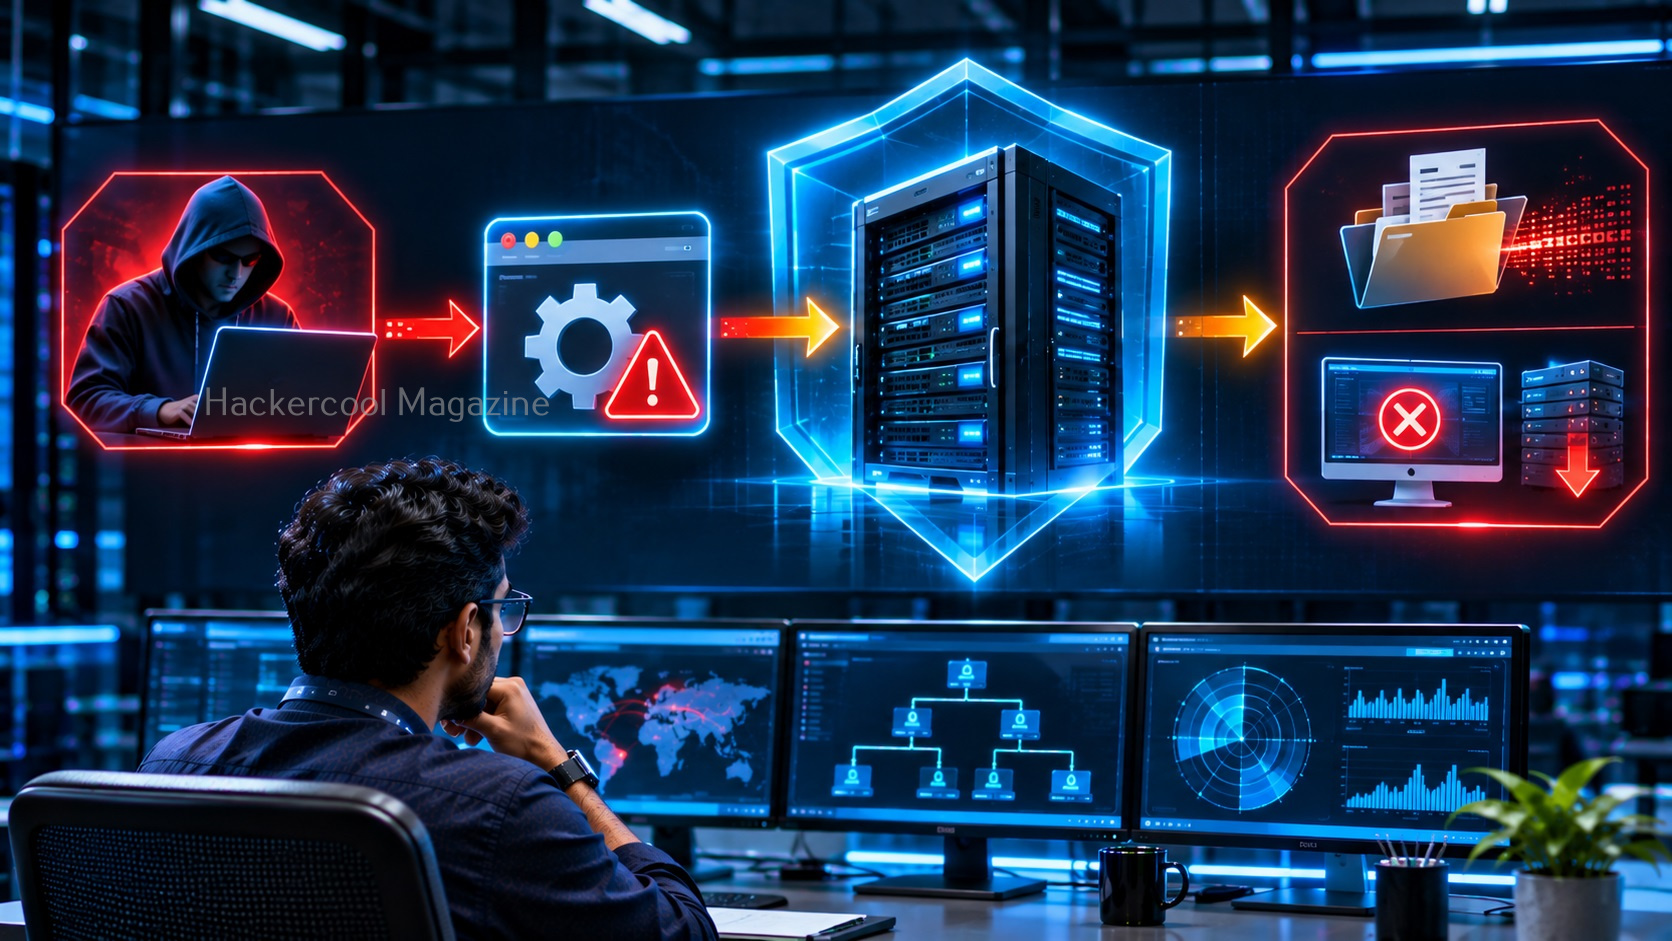
Threats, vulnerabilities and risk are related but they do not mean the same thing. Consider an organization running an outdated web server.
- The outdated server contains a vulnerability.
- A cybercriminal capable of exploiting it represents a threat.
- If the vulnerability is exploited, the organization may experience data theft or service disruption.
- The likelihood and potential consequences of that incident contribute to the organization’s risk.
This relationship explains why organizations need to identify both their weaknesses and the threats that could affect them.
A vulnerability may exist without being exploited. A threat may exist without successfully reaching a vulnerable system. Risk depends on the possibility and consequences of a harmful event.
How Do Cybersecurity Professionals Manage These Risks?
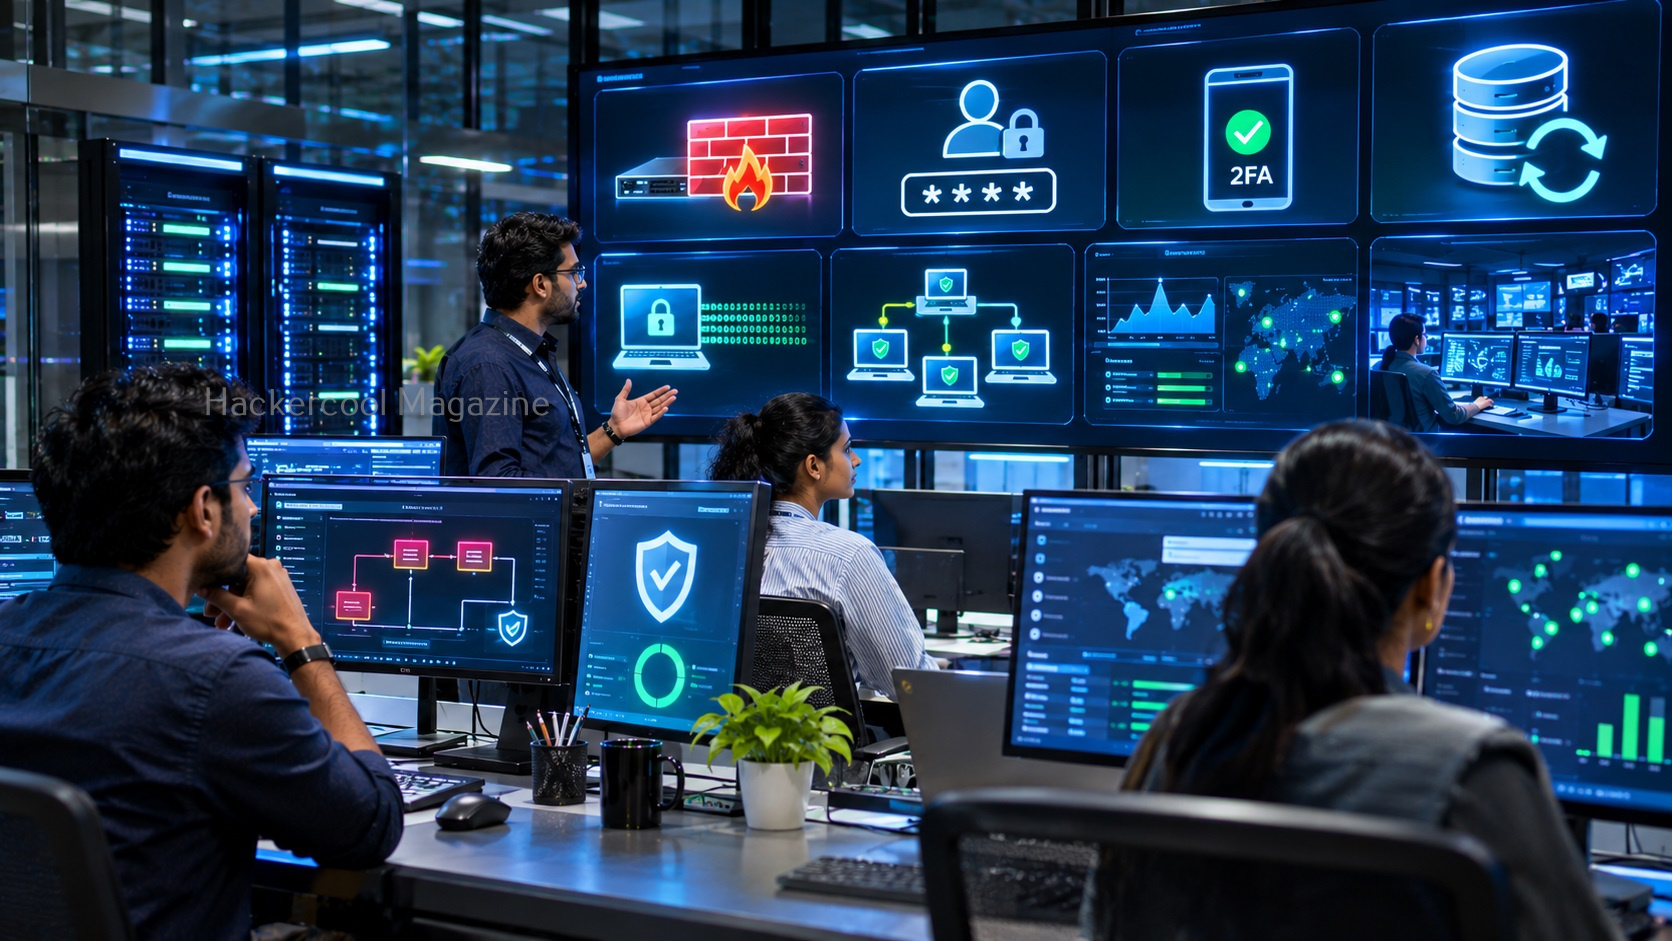
Organizations use a combination of technical, administrative and operational controls to reduce cybersecurity risk.
Common security practices include:
- Asset identification: Identify important systems, applications, devices and data.
- Threat assessment: Understand the threats that could affect those assets.
- Vulnerability assessment: Identify weaknesses in systems and configurations.
- Risk prioritization: Evaluate likelihood and impact to determine which issues need attention.
- Security controls: Implement appropriate safeguards, such as encryption, access control, patching and monitoring.
- Continuous monitoring: Review systems, logs, alerts and security configurations.
- Incident response: Prepare procedures for detecting, containing, investigating and recovering from security incidents.
Security is not a one-time activity. New vulnerabilities, threats and business changes continually affect an organization’s security posture.
Why Are These Fundamentals Important for Ethical Hackers?
Understanding cybersecurity fundamentals is essential for anyone interested in ethical hacking or penetration testing. An ethical hacker must understand what needs protection, which security weaknesses may exist, how attackers might exploit them and what impact a successful attack could have.
For example, during an authorized security assessment, a penetration tester may discover that a web application exposes sensitive information because of an access control weakness.
The tester should understand:
- Which security objective is affected?
- What vulnerability caused the weakness?
- What threat could exploit it?
- What could happen if the weakness were abused?
- How should the organization prioritize and fix it?
These questions connect practical penetration testing with the broader principles of cybersecurity risk management. Beginners should build this knowledge through networking, Linux and Windows fundamentals, web security, virtual labs and authorized security exercises.
Conclusion
Cybersecurity is built on fundamental principles that help organizations protect digital systems and information.
The CIA Triad defines three essential security objectives: confidentiality, integrity and availability. Threats represent potential sources of harm, vulnerabilities are weaknesses that may be exploited and risk describes the potential consequences of harmful events.
Understanding how these concepts connect provides a strong foundation for learning network security, ethical hacking, vulnerability assessment and defensive cybersecurity.
Before learning advanced security tools, make sure you understand these fundamentals. They will help you think like a security professional rather than simply learn how to operate security software.
YOUR ETHICAL HACKING JOURNEY STARTS HERE!
Not sure where to begin? Download our FREE 18-page Beginner Ethical Hacker Starter Kit (2026 Edition).
Take your first step towards building practical cybersecurity knowledge.


