
Imagine visiting your favorite website, only to find that it is extremely slow or completely unavailable. The internet connection may be working perfectly but the website itself cannot respond to your request.
One possible reason for this s a Denial-of-Service (DoS) attack.
DoS attacks are designed to make a website, server, application or network service unavailable to legitimate users. They achieve this by exhausting resources, disrupting communication or exploiting weaknesses in the targeted system.
Understanding DoS attacks is an important part of cybersecurity because availability is one of the three fundamental principles of information security. In this beginner’s guide, we will explore what DoS attacks are, how they work, their common types, their impact and how organizations can defend against them.
NEW TO ETHICAL HACKING?
Start your ethical hacking journey with our FREE Beginner Ethical Hacker Starter Kit (2026 Edition).
Get beginner-friendly guidance to understand the fundamentals of ethical hacking and take your first steps into cybersecurity.
What Is a DoS Attack?
A Denial-of-Service attack is a cyberattack that attempts to prevent legitimate users from accessing a computer system, network, website or online service. The attacker overwhelms or disrupts the target so that it cannot respond normally to genuine requests.
For example, imagine a website server that can comfortably handle a certain number of simultaneous requests. If an excessive number of requests arrive, the server may run out of available resources. Legitimate visitors may experience slow responses, connection failures or complete service disruption.
DoS attacks primarily target the availability component of the CIA triad:
- Confidentiality: Protecting information from unauthorized access.
- Integrity: Preventing unauthorized modification of information.
- Availability: Ensuring systems and services remain accessible when needed.
Unlike attacks that aim to steal information like Phishing, a DoS attack primarily attempts to disrupt access.
How Does a DoS Attack Work?
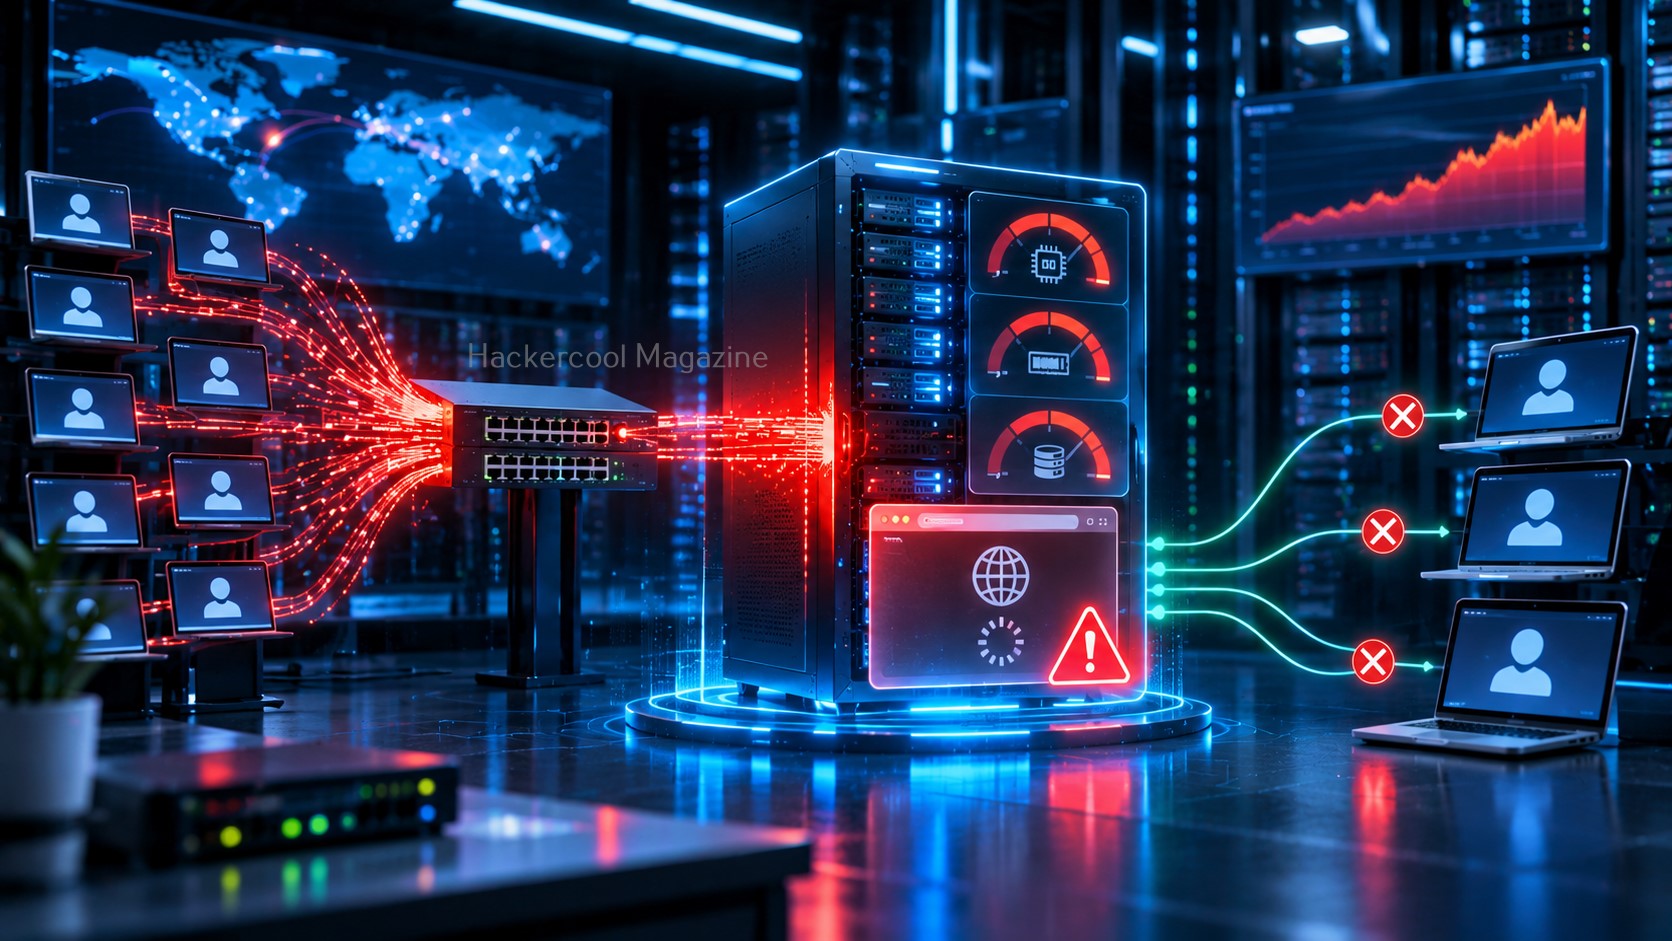
A typical DoS attack involves overwhelming a target or interfering with its ability to provide services. Consider a web server that receives requests from visitors. Each request consumes some combination of network bandwidth, memory, CPU processing or application resources.
When traffic exceeds the server’s capacity, its ability to handle legitimate requests decreases.
The general process can be understood in four stages:
- Target selection: An attacker chooses a website, server, application or network service.
- Resource exhaustion or disruption: The target experiences excessive traffic or another form of interference.
- Service degradation: Response times increase, errors appear or connections fail.
- Denial of service: Legitimate users can no longer access the service reliably.
The exact behavior depends on the attack technique and the target’s infrastructure.
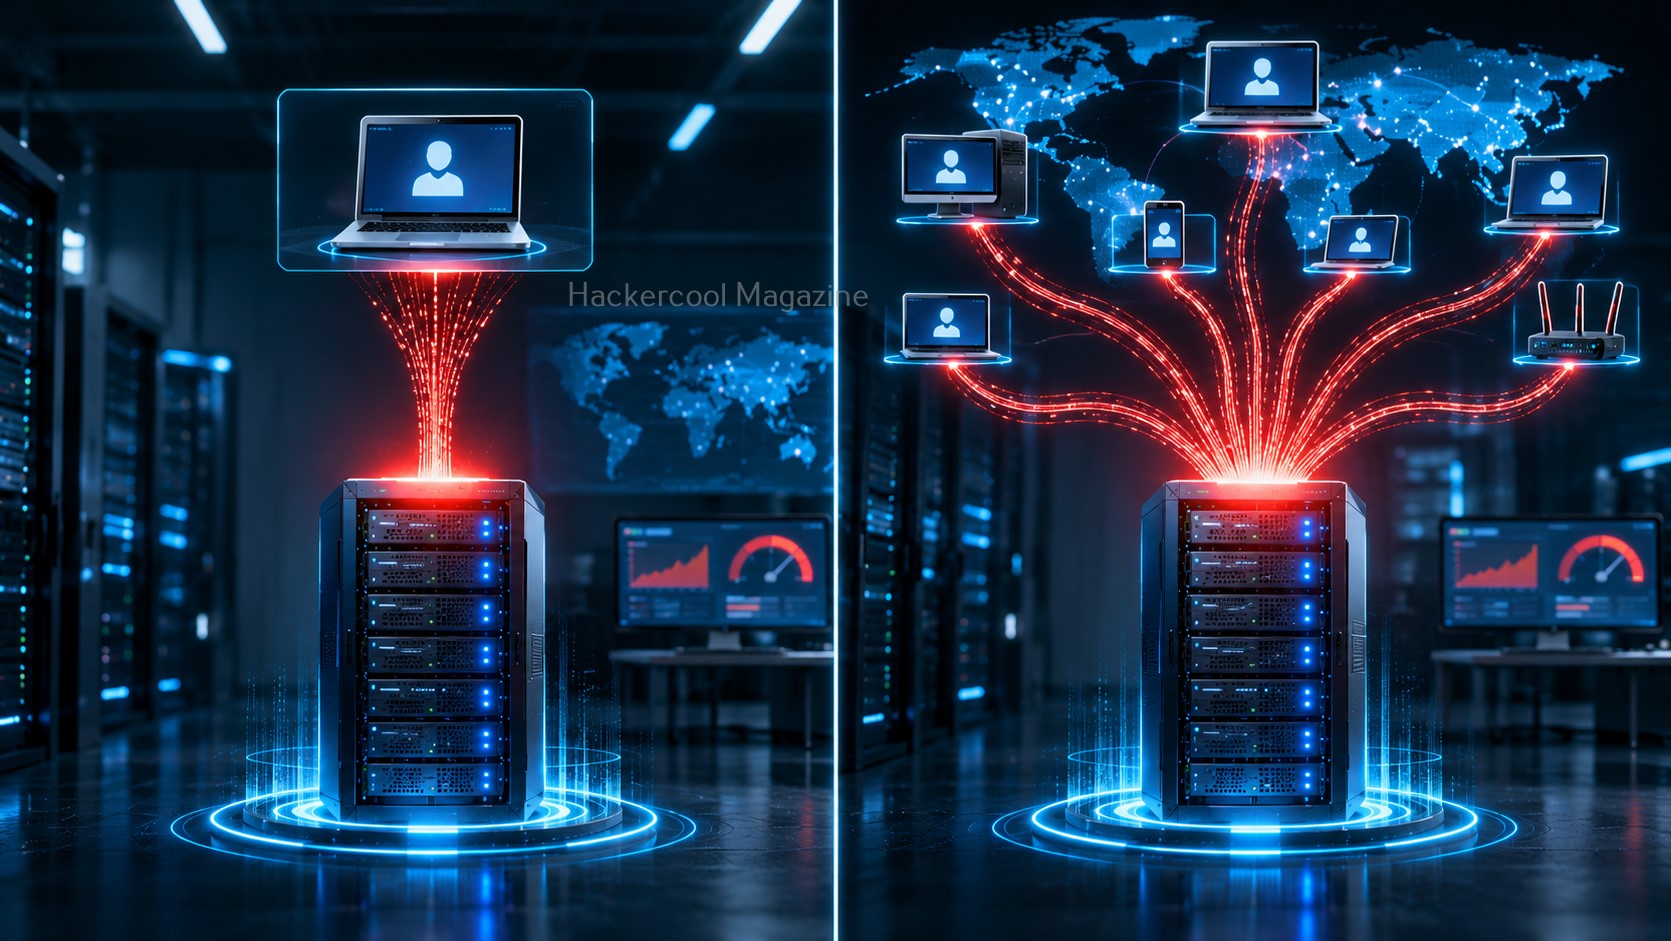
What Is the Difference Between DoS and DDoS?
DoS and Distributed Denial-of-Service (DDoS) attacks share the same broad objective: making a service unavailable.
The main difference is where the attack traffic originates.
DoS (Denial-of-Service): Typically involves an attack originating from a single source or a limited number of sources.
DDoS (Distributed Denial-of-Service): Involves traffic or activity originating from multiple distributed systems, often compromised devices controlled as part of a botnet.
A DDoS attack can be particularly difficult to manage because traffic arrives from many different sources and may resemble legitimate activity.
| Feature | DoS | DDoS |
|---|---|---|
| Source | Usually one source | Multiple distributed sources |
| Scale | Often more limited | Can be much larger |
| Traffic management | May be easier to isolate | More complex |
| Infrastructure | Single or limited sources | Often distributed devices |
| Defense | Filtering and resource protection | Distributed traffic mitigation and filtering |
Common Types of DoS Attacks
DoS attacks can target different layers of network communication and application infrastructure.
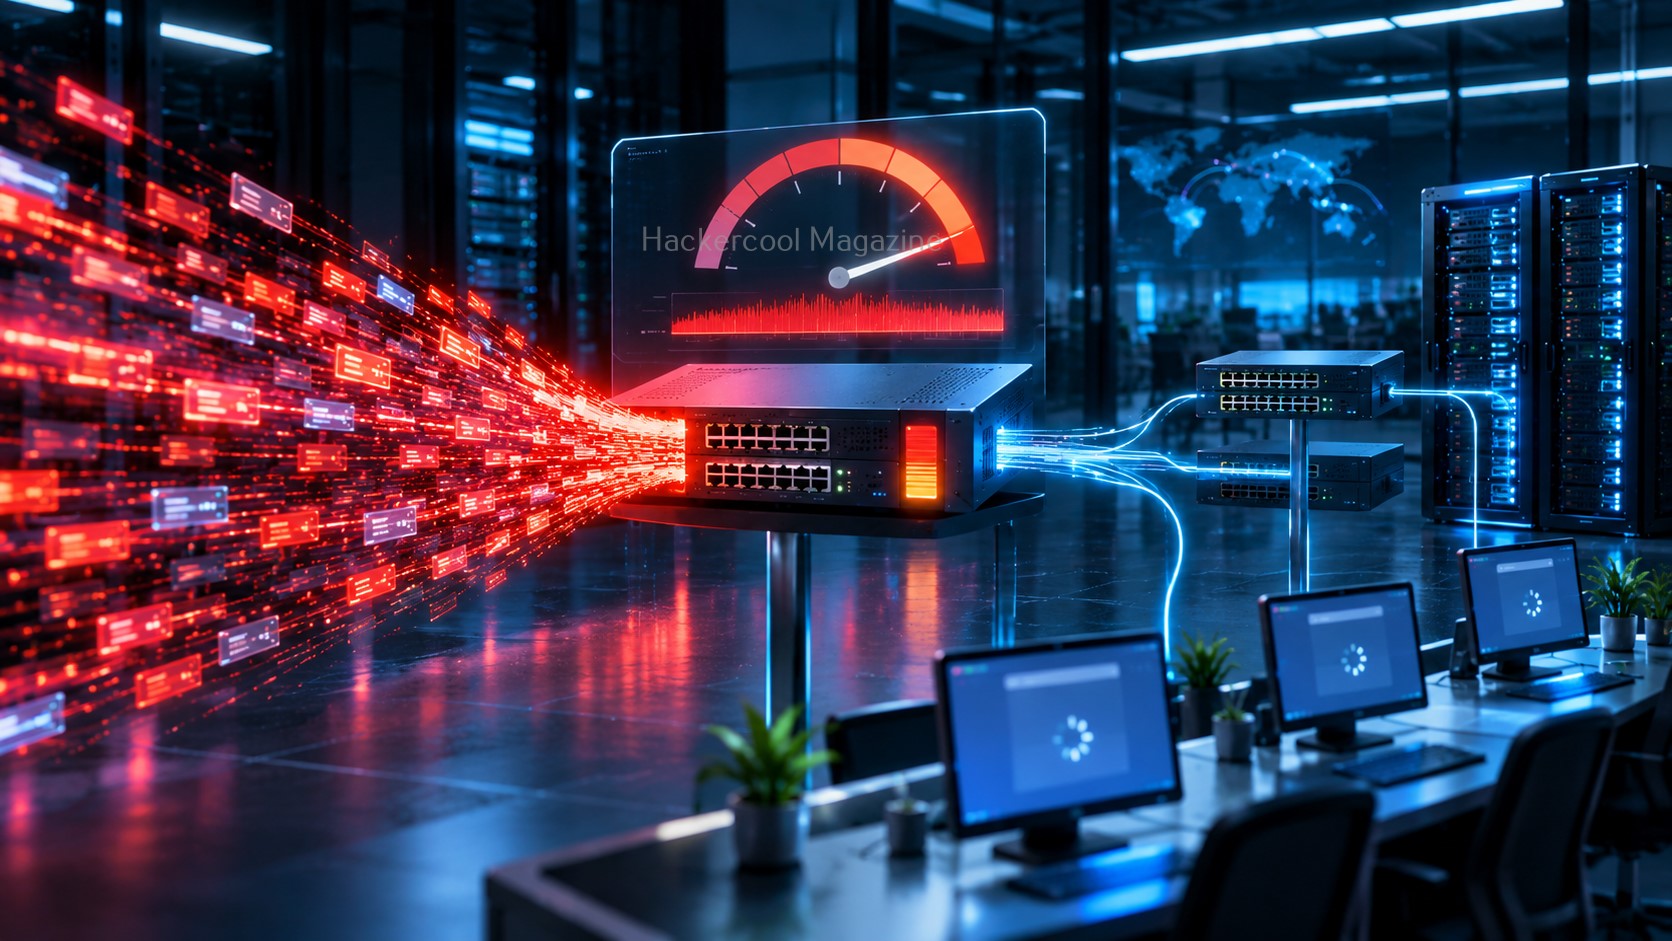
Volumetric attacks
These attacks attempt to consume the available network bandwidth by generating excessive traffic. When incoming traffic exceeds the network’s capacity, legitimate users may experience severe delays or lose connectivity. Given below are some examples of volumetric attacks.
1. Ping Of Death attack:
According to RFC791 IP, the maximum size of the packet should not exceed 65,535 bytes. In the Ping of Death attack, an attacker sends an oversized packet of size more than the prescribed limit with a ping request. (For example, a packet of size 65,550 bytes). The target system may crash while trying to reassemble this packet.

2. UDP Flood attack:
In this type of attack, an attacker sends a number of spoofed UDP packets to random ports of the target system. Target server tries to check for these applications (some of which are nonexistent) repeatedly. This causes exhaustion of the bandwidth in use thus replying to legitimate connections with a ICMP destination unreachable message.
3. ICMP Flood attack:
In the ICMP flood attack, the attacker sends a large volume of ICMP request (ping) messages to the target server either from a single IP or multiple IP addresses. The target server is bound to reply to these packets with a ICMP echo reply message thus exhausting the bandwidth.

4. Smurf attack:
In a smurf attack, the attacker sends ICMP echo request message to the broadcast network address spoofing the IP address of the target server. This makes all the devices in the network to reply to this echo request message with a echo reply message. Since the address of the target server is used in the echo request message, all the devices reply with this IP thus, making the target server inaccessible to the legitimate users. Before this, it is better to understand how a network works in our beginners guide for Networking Fundamentals.
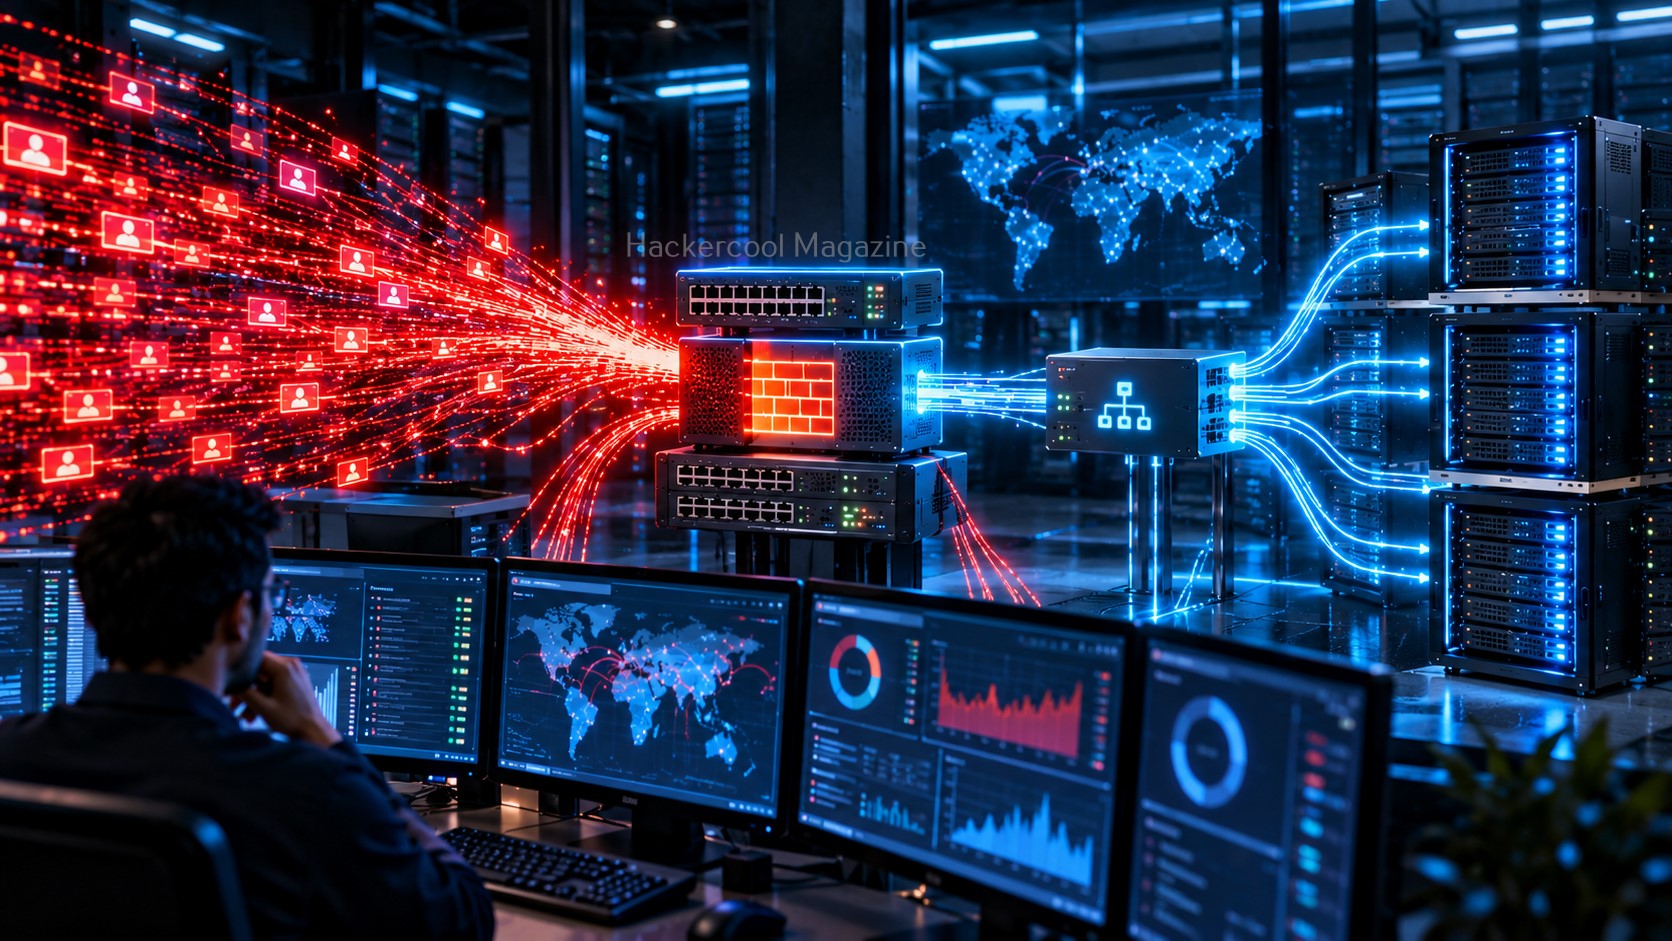
Protocol attacks
Protocol attacks target weaknesses or resource limitations in network protocols and the systems implementing them. They may exhaust resources such as connection tables, session-handling capacity or other network-device processing capabilities. Exanples of Protocol attacks are,
1. SYN Flood attack:
In our blogpost on port scanning techniques, you learnt about the 3-way handshake.

In this attack, attackers exploit this 3-way handshake. How? The attacker sends multiple TCP SYN requests to the target server. When the target server responds to these SYN requests with a SYN/ACK packet, the attacker never sends a ACK message in response. This creates a partially open connection. By default, the target server or machines should track a partially opened connection for 75 seconds.

This is known as SYN flood. In these 75 seconds, the attacker can send large volume of SYN requests thus overloading the target system which eventually makes it inaccessible to the legitimate users.
2. Fragmentation attack:
Network or IP layer allows packet fragmentation in order to overcome the problem of any higher-level protocol creating a packet larger than the size any particular local network supports. If you are new to networking, Learn about different layers and their funsctions during network communication in our OSI Model for beginners blogpost.
READY TO BUILD YOUR ETHICAL HACKING FOUNDATIONS?
Go beyond the basics. Develop the essential knowledge every aspiring ethical hacker needs.
Your learning package includes:
Networking Fundamentals
Linux Fundamentals
Windows Fundamentals
Web Fundamentals
Command Line Essentials
Virtual Labs
$1 INTRODUCTORY TRIAL
6 Foundation Resources + Full Magazine Access
Trial terms apply. Post-trial subscription billing is manual.
Attackers exploit this feature to send a large number (1500+bytes) of fragmented packets to the target server. The size of each fragment is usually reduced and small packet rate is used. This forces the target server to utilize a large number of resources to reassemble these fragmented packets thus causing DoS attack.
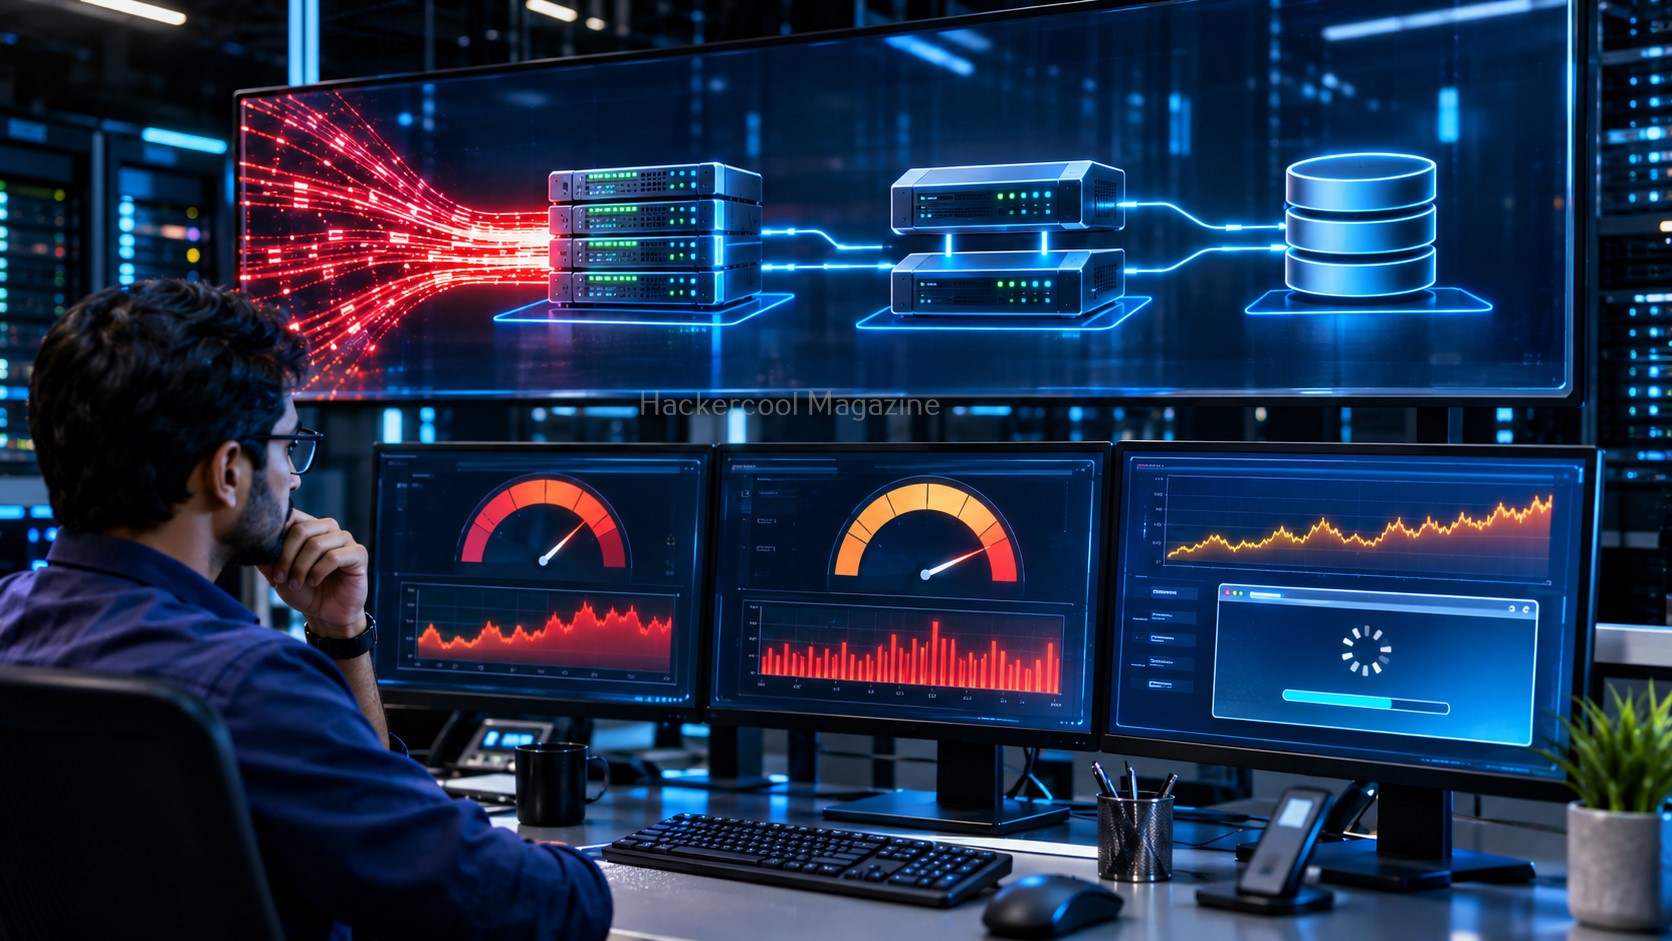
Application-layer attacks:
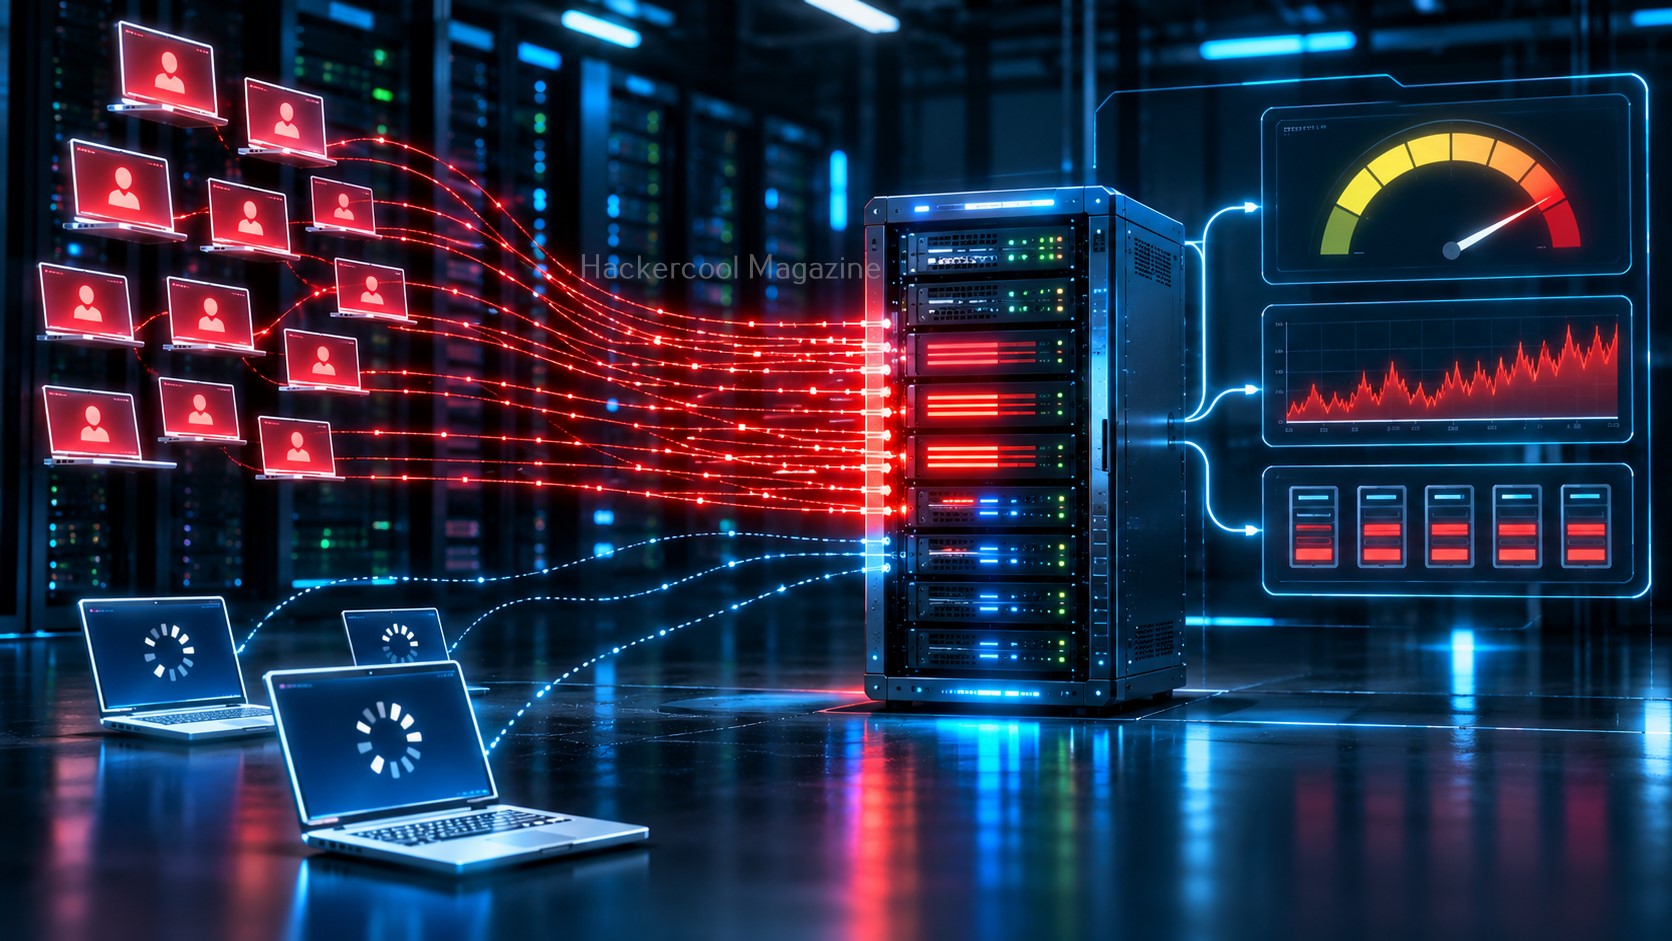
Application-layer attacks target services such as websites, APIs and web applications. Instead of simply generating enormous volumes of traffic, these attacks may cause resource-intensive application operations to consume excessive processing capacity.
For example, an application may struggle when it receives an unusually large number of expensive database operations.
1. HTTP GET/POST attack:
Browsers connect to the web server using HTTP requests. These requests can be either HTTP GET or HTTP POST. In this type of attack, attackers exploit these requests to perform DoS attacks.
In a HTTP GET DoS attack, attackers use time delayed HTTP headers to exhaust resources of webserver whereas in HTTP POST DoS attack the attacker sends HTTP requests with complete headers and without a message body or an incomplete message body.
Slow-rate attacks:
Some DoS techniques attempt to keep connections or application resources occupied for extended periods rather than generating enormous traffic volumes.
These attacks can be difficult to recognize because their traffic levels may be relatively low compared with large volumetric attacks.
What Is a Botnet in DDoS Attacks?
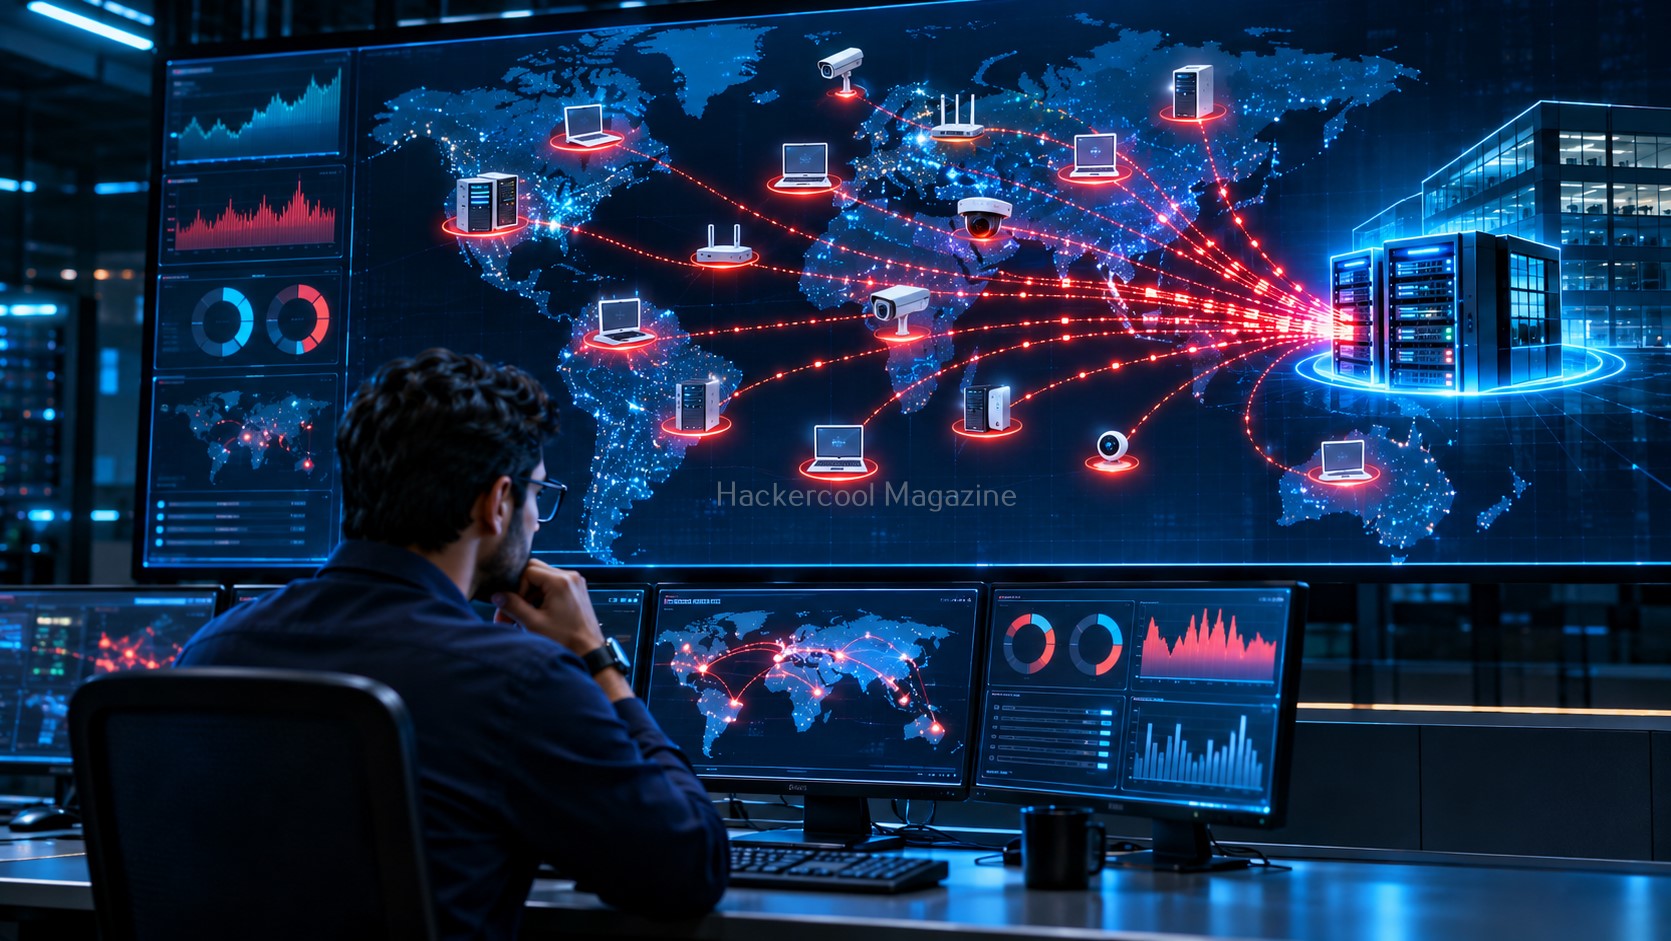
A botnet is a collection of compromised internet-connected devices that can be controlled remotely by an attacker. These devices may include computers, servers, routers and Internet of Things (IoT) devices.
When a botnet is used in a DDoS attack, many compromised devices can send traffic toward a common target. The target may receive requests from numerous locations, making it difficult to distinguish malicious activity from legitimate visitors. Botnets are one reason DDoS attacks can reach considerable scale.
What Happens During a DoS Attack?
The impact depends on the target, its available resources and the attack technique.
Common symptoms include:
- Websites becoming unusually slow.
- Applications returning errors.
- Network connections timing out.
- Servers experiencing unusually high resource consumption.
- Legitimate users being unable to log in or complete transactions.
- Online services becoming temporarily unavailable.
For businesses, these disruptions can lead to lost revenue, customer dissatisfaction, operational delays and reputational damage. For organizations that depend on online services, even a relatively short outage can have significant consequences.
How Can Organizations Detect DoS Attacks?
Early detection helps security teams investigate unusual activity before it causes prolonged disruption.
Organizations commonly monitor:
Network traffic:
Sudden changes in incoming traffic volume, connection patterns or source distribution.
Server resources:
Unusual CPU, memory, connection or bandwidth consumption.
Application performance:
Increased response times, repeated errors and unexpected request patterns.
Security logs:
Repeated connection attempts, unusual access behavior and abnormal service activity.
Monitoring tools, network analysis platforms, intrusion detection systems and application performance monitoring can help identify suspicious patterns. However, high traffic alone does not prove an attack. A legitimate product launch, popular event or sudden increase in visitors can also create heavy demand.
Security teams must examine traffic behavior and business context before deciding how to respond.
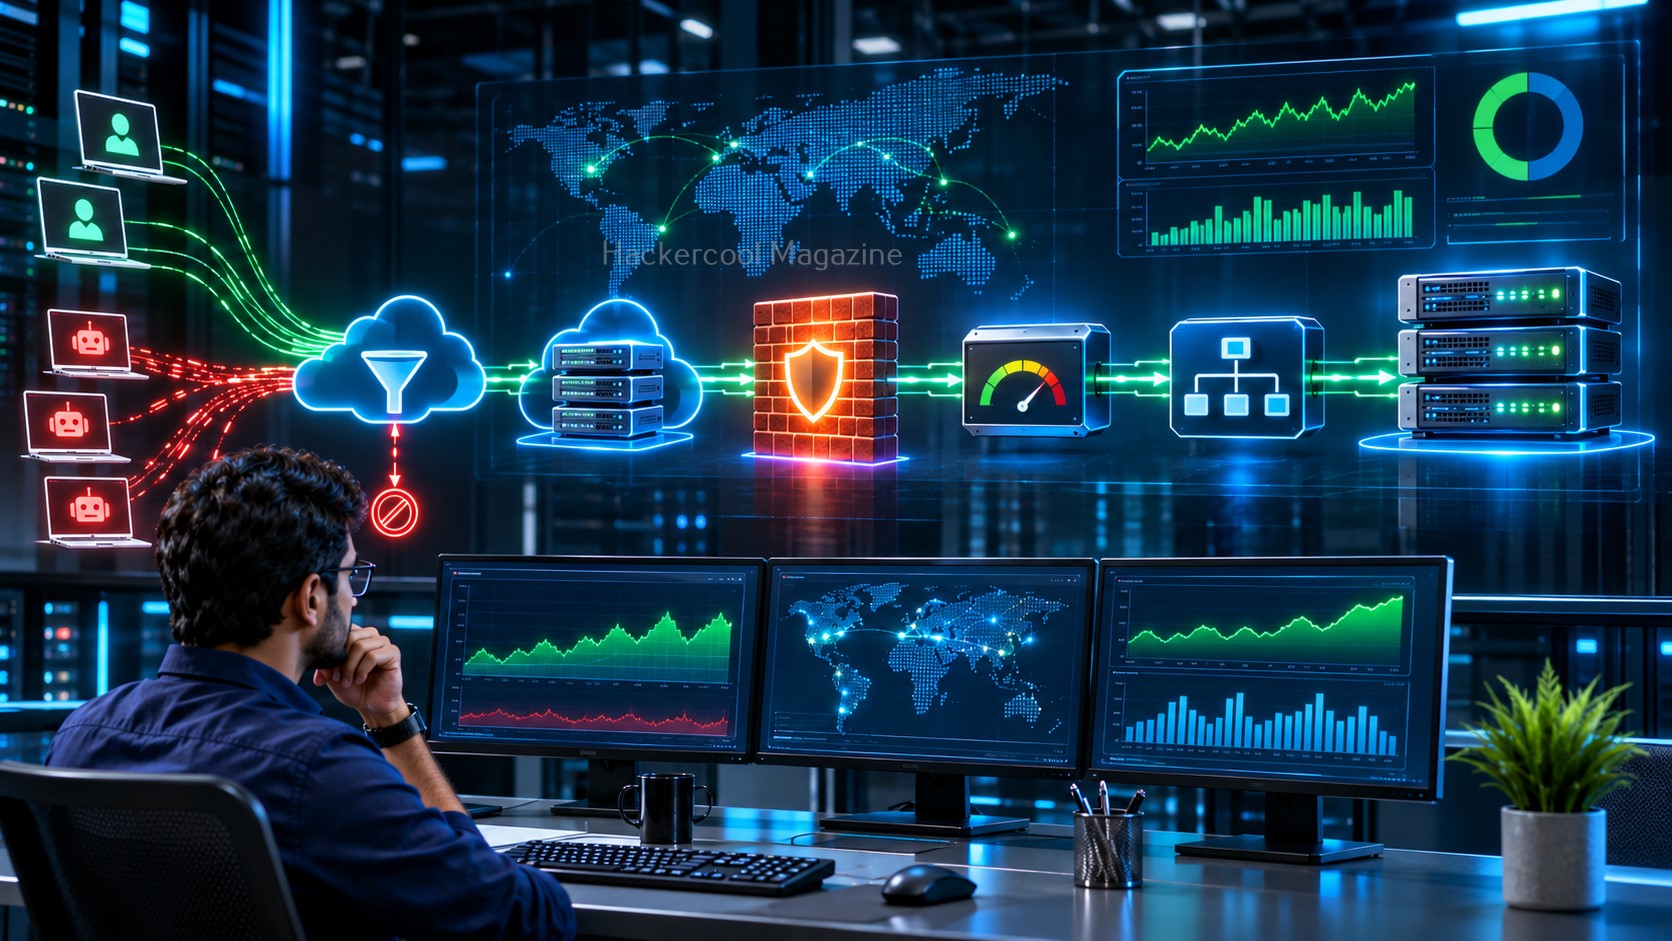
How to Prevent and Mitigate DoS Attacks
No single security measure can prevent every DoS or DDoS attack. Organizations should use multiple defensive layers.
Use DDoS protection services:
Specialized providers can identify and filter malicious traffic before it reaches the protected infrastructure.
Deploy firewalls and traffic filtering:
Properly configured network and application controls can help block unwanted traffic.
Use a Content Delivery Network (CDN):
A CDN distributes content across multiple locations and can help absorb traffic spikes when combined with appropriate protection.
Apply rate limiting:
Limit the frequency of requests from clients or identities where appropriate, while considering legitimate shared networks and application requirements.
Monitor network and application performance:
Continuous monitoring helps identify unusual traffic patterns and service degradation.
Build resilient infrastructure:
Load balancing, redundancy, capacity planning and failover arrangements can improve service availability.
Prepare an incident response plan:
Define responsibilities, escalation procedures, communication methods and recovery steps before an attack occurs.
How Can Beginners Learn About DoS Attacks Safely?
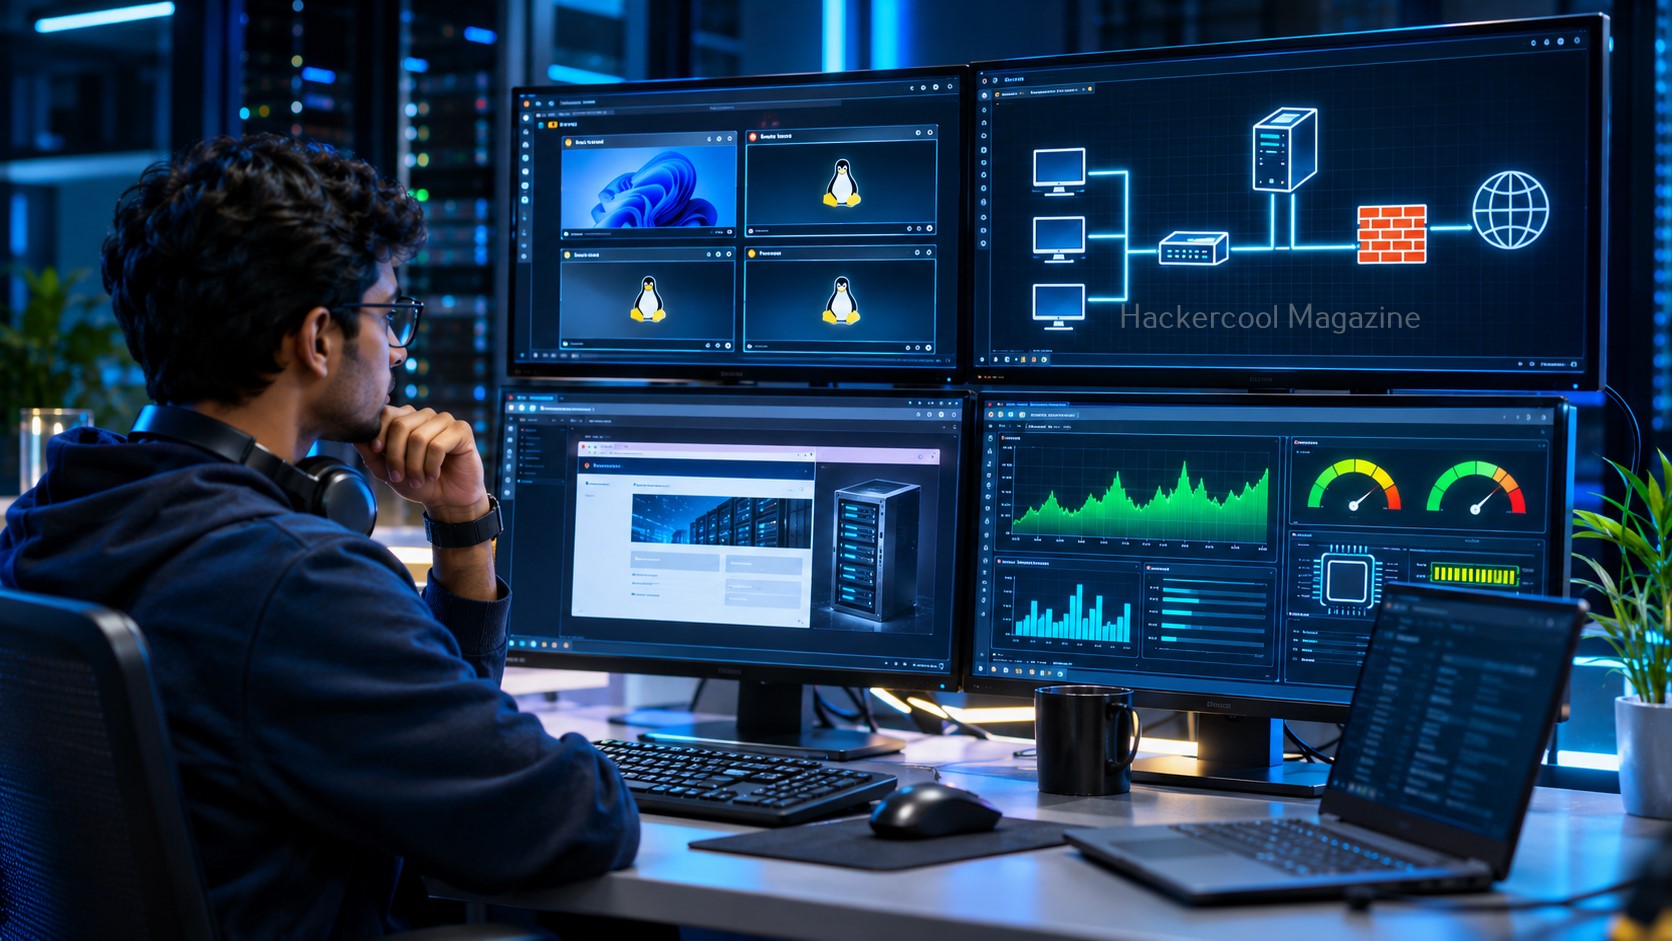
If you are learning ethical hacking or network security, understanding DoS attacks is useful for recognizing availability risks and evaluating defensive controls. Start by studying networking fundamentals, TCP/IP, HTTP, DNS, server resources and basic traffic analysis.
You can then explore:
- How web servers handle legitimate requests.
- How bandwidth, CPU, memory and connection limits affect performance.
- How to analyze sample network traffic using Wireshark.
- How monitoring dashboards identify abnormal traffic.
- How rate limiting and load balancing improve availability.
- How organizations plan for service disruptions.
Use isolated training environments, synthetic traffic and authorized demonstrations. Never test DoS techniques against public websites, third-party servers or networks without explicit written authorization and an agreed testing scope.
The objective is to understand the security risk and learn how to protect systems, not to disrupt services.
Conclusion
Denial-of-Service attacks demonstrate how important availability is to modern digital services. Whether an attack targets network bandwidth, protocol resources or application processing capacity, the result can be the same: legitimate users lose access to the service.
Understanding DoS and DDoS attacks helps cybersecurity beginners develop a broader understanding of network security, infrastructure resilience, monitoring, and incident response.
Start by learning how networks and servers operate, study the different attack categories and explore defensive technologies in authorized environments. In cybersecurity, protecting a system also means ensuring that legitimate users can continue to access it when they need it.
YOUR ETHICAL HACKING JOURNEY STARTS HERE!
Not sure where to begin? Download our FREE 18-page Beginner Ethical Hacker Starter Kit (2026 Edition).
Take your first step towards building practical cybersecurity knowledge.


