
Imagine logging in to your email account, online banking service or social media platform. You enter your username and password, complete authentication and begin using the service. You do not need to enter your credentials every time you open a new page because the website remembers that you are authenticated.
Understanding session hijacking requires a basic knowledge of cybersecurity fundamentals, including confidentiality, authentication, access control and common security threats.
But how does a website recognize you after login?
It generally uses a mechanism called a session. HTTP & HTTPS are itself stateless and hence sessions are used by almost all the webservers to keep the user logged in and track him. A session is assigned as soon as user logs in and it is kept active for a particular period of time or until the user decides to log out. These active sessions are tracked using piece of text called a Session ID. Usually Session ID is included as part of a cookie.

Sessions help websites maintain your authenticated state while you navigate between pages. If an attacker manages to take control of a valid session, they may be able to access an account without knowing the user’s password. This is known as session hijacking.
In this beginner-friendly guide, we will explore what session hijacking is, how it works, common techniques and how users and organizations can defend against it.
NEW TO ETHICAL HACKING?
Start your ethical hacking journey with our FREE Beginner Ethical Hacker Starter Kit (2026 Edition).
Get beginner-friendly guidance to understand the fundamentals of ethical hacking and take your first steps into cybersecurity.
What is Session Hijacking?
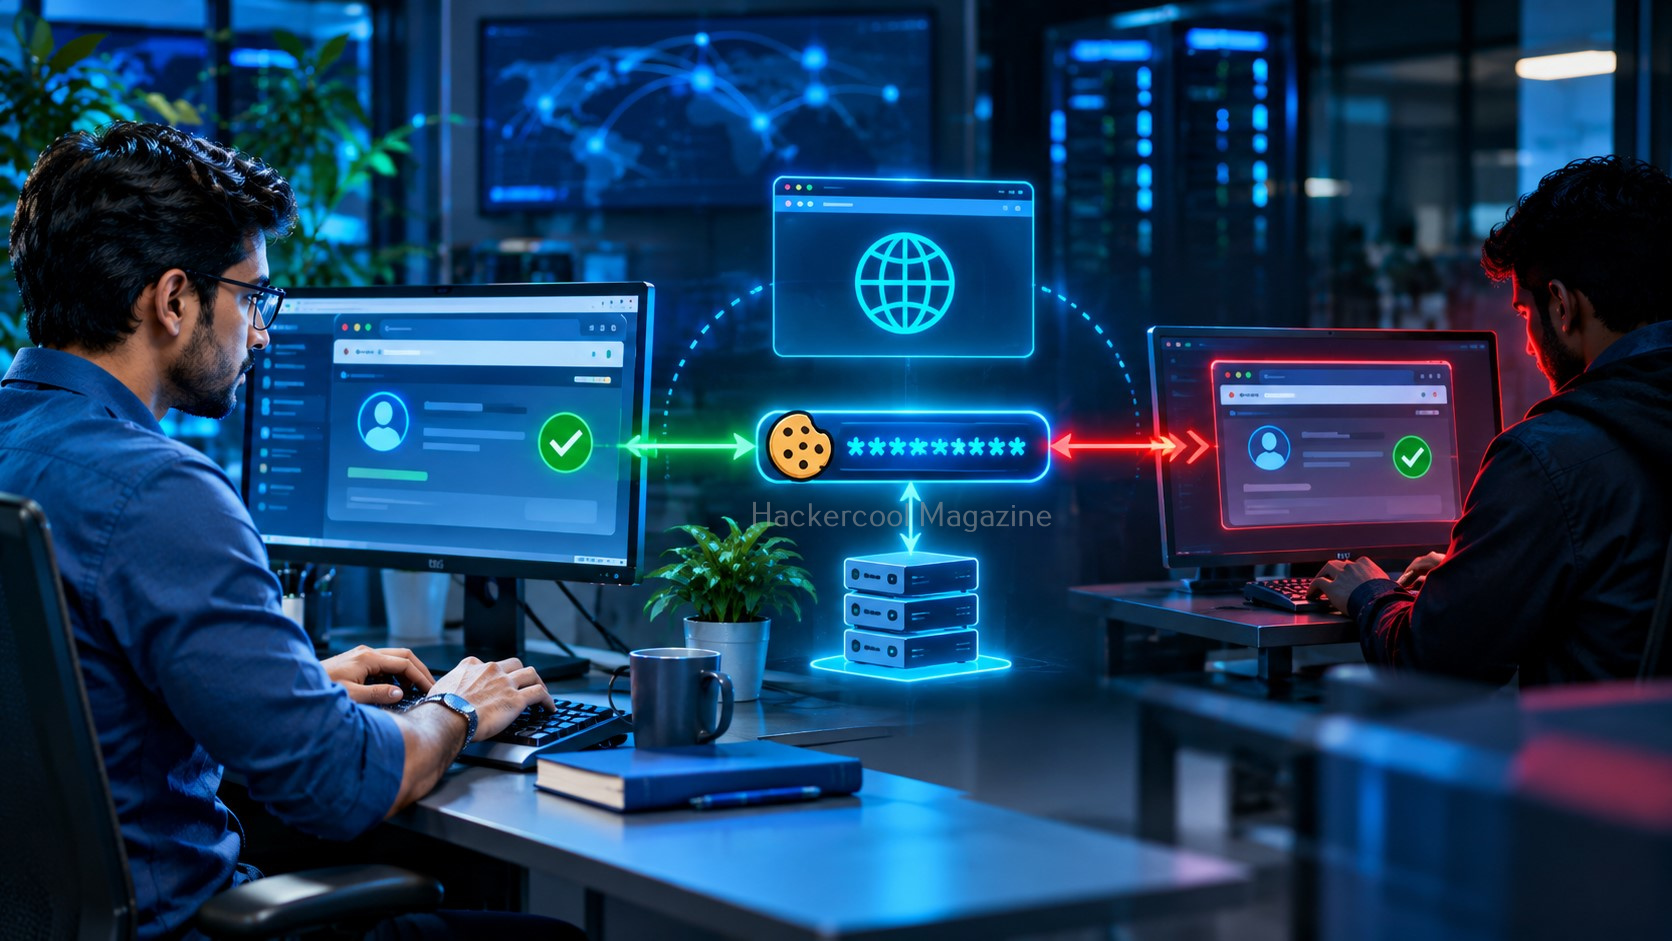
Session hijacking is a type of attack in which an attacker obtains or takes control of a user’s active session to impersonate that user.
When you successfully log in to a website, the server typically creates a session and associates it with your authenticated account. The website may issue a session identifier, often stored in a browser cookie. Your browser sends this identifier with subsequent requests so the server can recognize your session.
If an attacker obtains a valid session identifier and the application does not have adequate protections, the attacker may be able to impersonate the authenticated user.
In simple terms, session hijacking means taking over an existing authenticated session rather than logging in with the victim’s credentials.
This is why session security is an important part of web application security.
How Do Web Sessions Work?
Before understanding session hijacking, it helps to understand how a normal web session works.
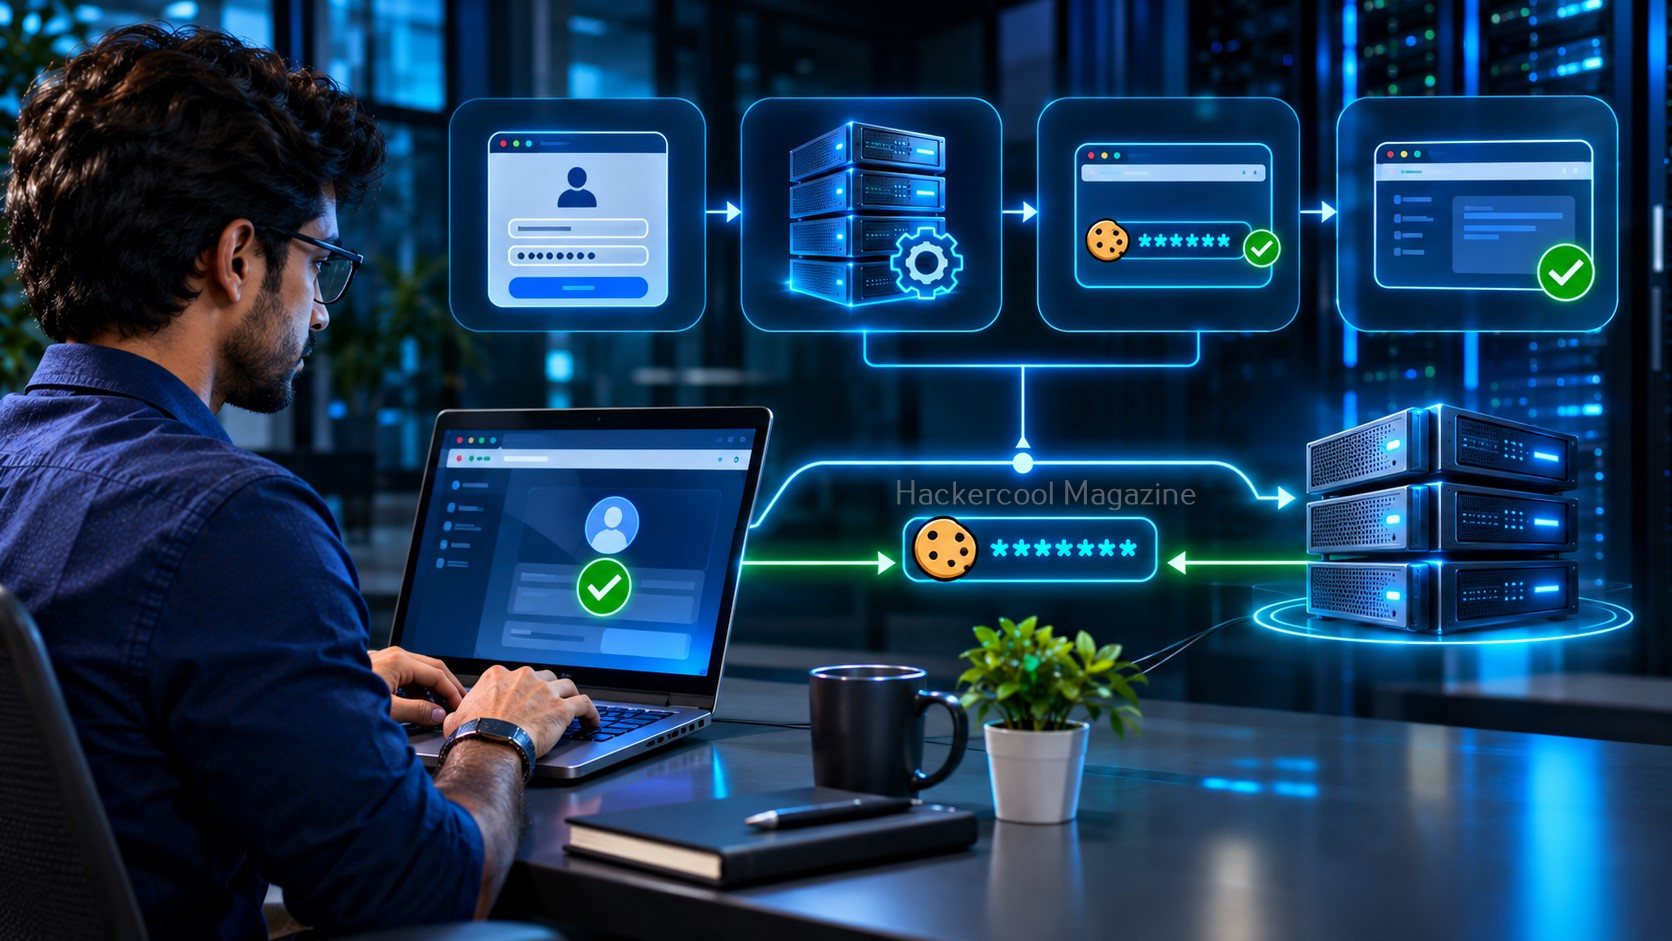
Consider a user logging in to an online service:
- The user visits the website and enters their login credentials.
- The website verifies the credentials.
- The server creates an authenticated session.
- The server sends a session identifier to the browser, commonly through a cookie.
- The browser stores the cookie and sends it with relevant requests.
- The server uses the session identifier to recognize the authenticated user.
The session identifier acts like a temporary proof that the user has already authenticated. It is important to understand that the identifier is not necessarily the user’s password. However, if it is stolen and remains valid, it may provide access to the account.
How Does Session Hijacking Work?
Session hijacking generally involves an attacker obtaining a valid session identifier or otherwise taking control of an authenticated session.
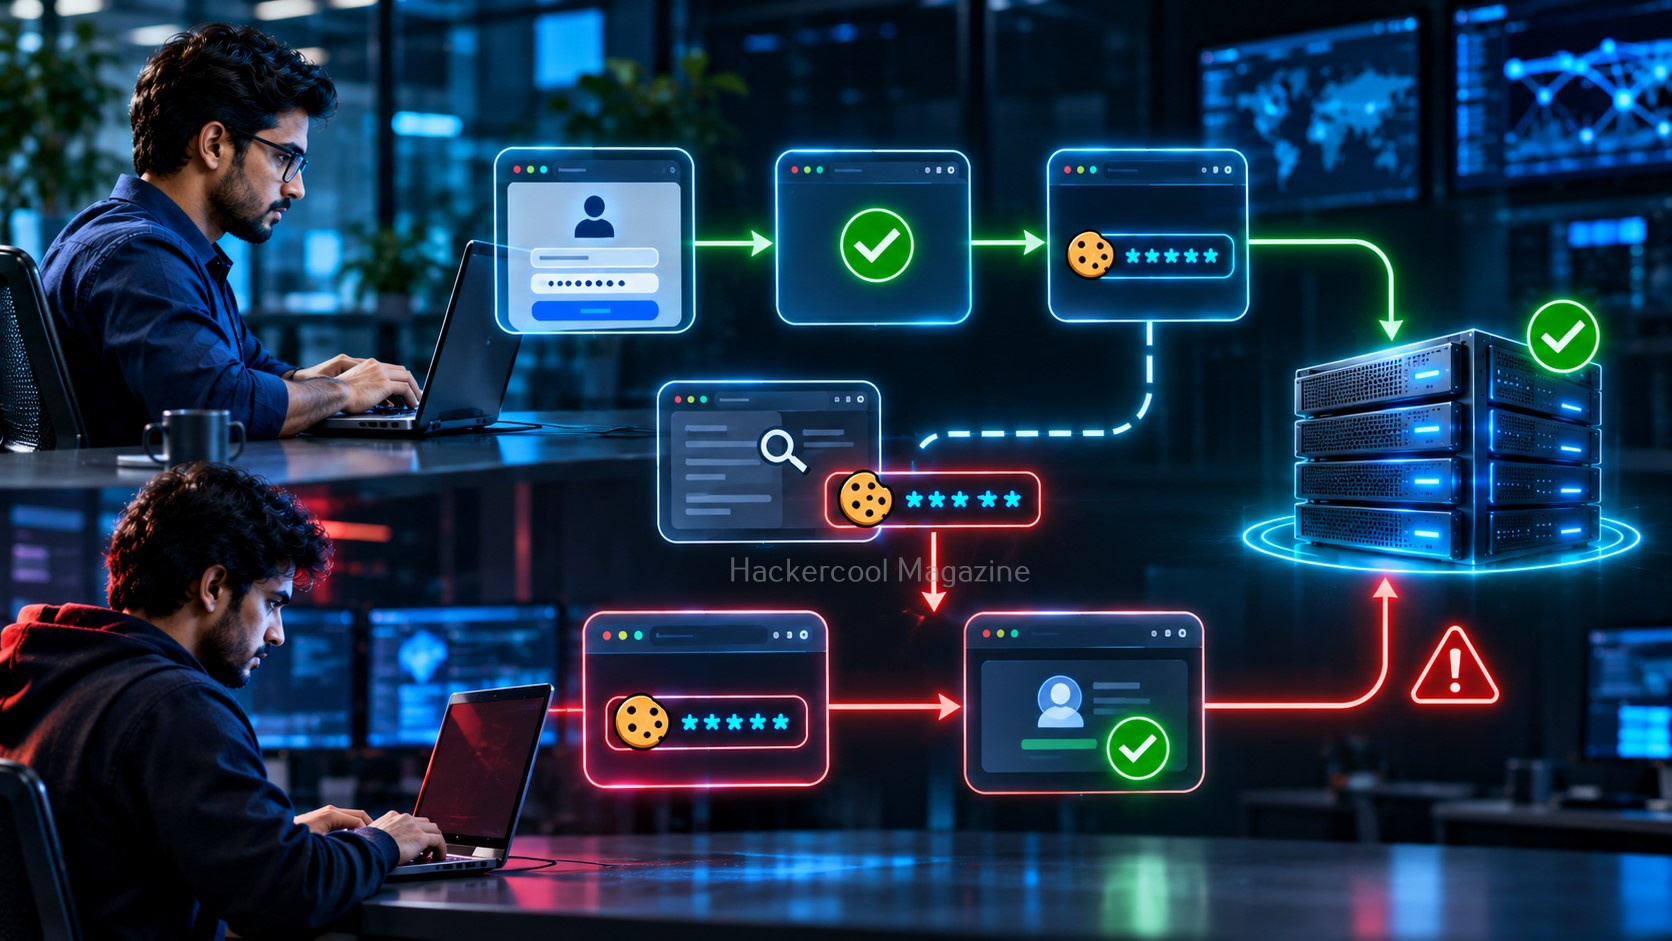
A simplified attack scenario looks like this:
Step 1: A user authenticates
The victim logs in to a website and the application creates an authenticated session.
Step 2: A session identifier is issued
The website sends a session cookie to the user’s browser.
Step 3: The session is exposed
An attacker obtains the session identifier through a security weakness, compromised device, malicious software or another attack technique.
Step 4: The attacker attempts to reuse the session
If the application accepts the stolen identifier and does not detect the suspicious activity, the attacker may be able to impersonate the user.
Step 5: Unauthorized access occurs
Depending on the application’s permissions and security controls, the attacker may view information or perform actions available to the authenticated account.
The attack does not always succeed. Session expiration, device checks, reauthentication requirements and other protections can prevent or limit misuse.
Common Types of Session Hijacking
Session hijacking can happen through several different techniques. Understanding them helps developers and security professionals identify weaknesses.
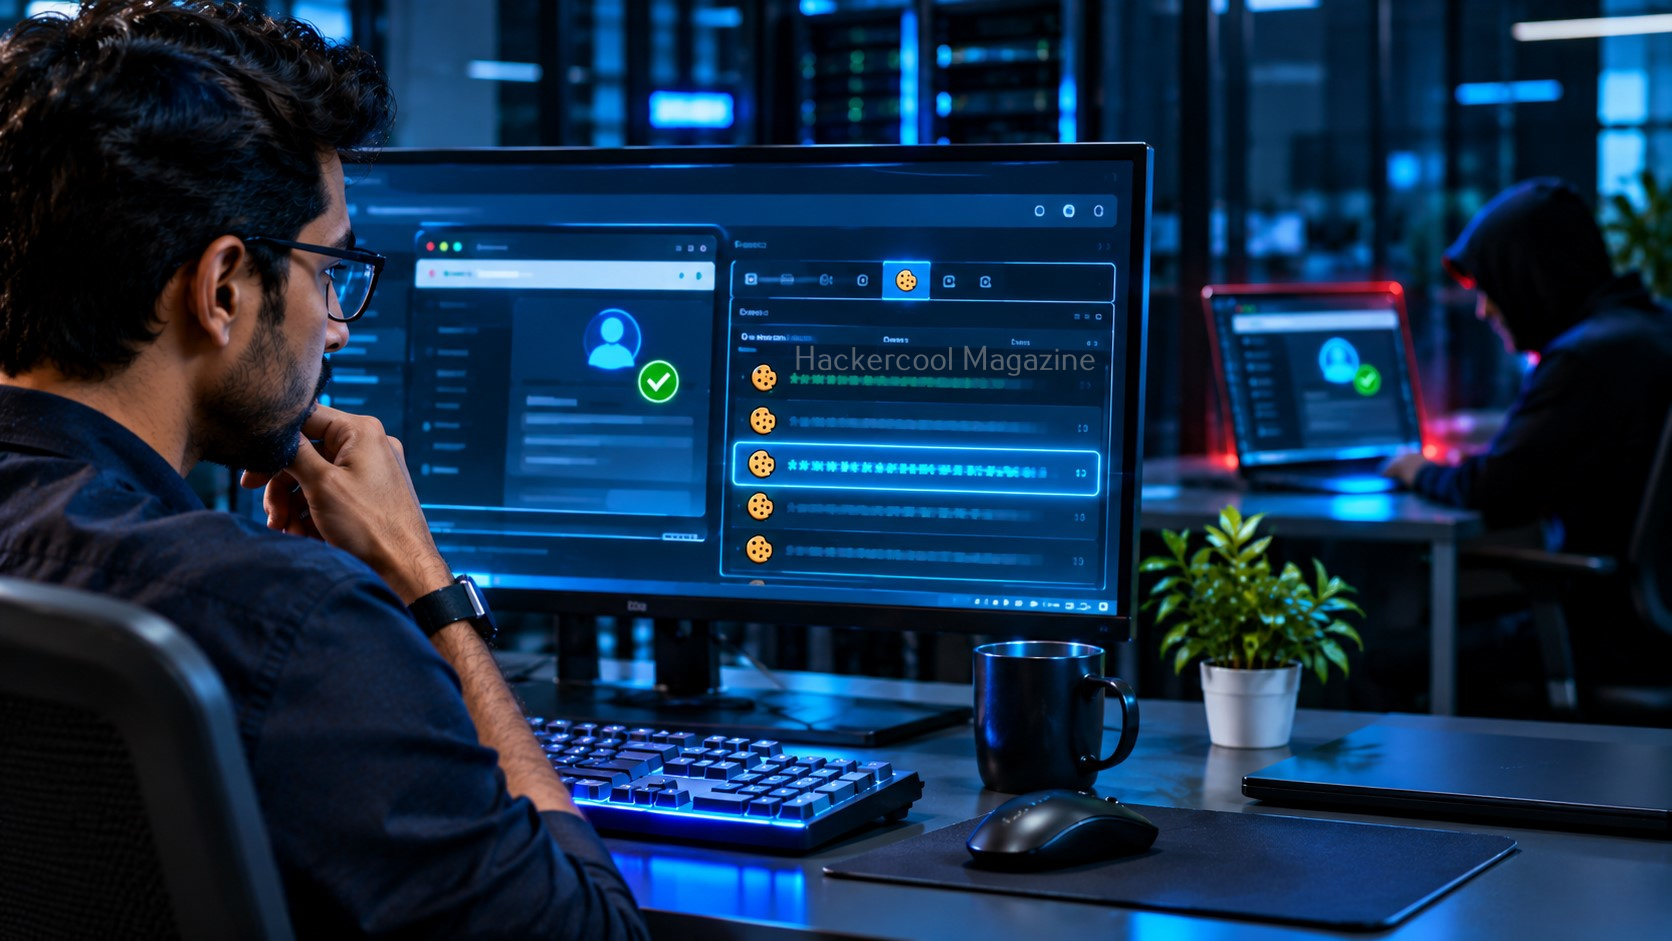
1. Session Cookie Theft:
Session cookies often contain or reference the information used to identify an authenticated session. If an attacker gains access to a valid session cookie through malware, browser compromise, insecure storage or another vulnerability, the attacker may attempt to reuse it.
This is one reason session cookies must be protected like authentication credentials.
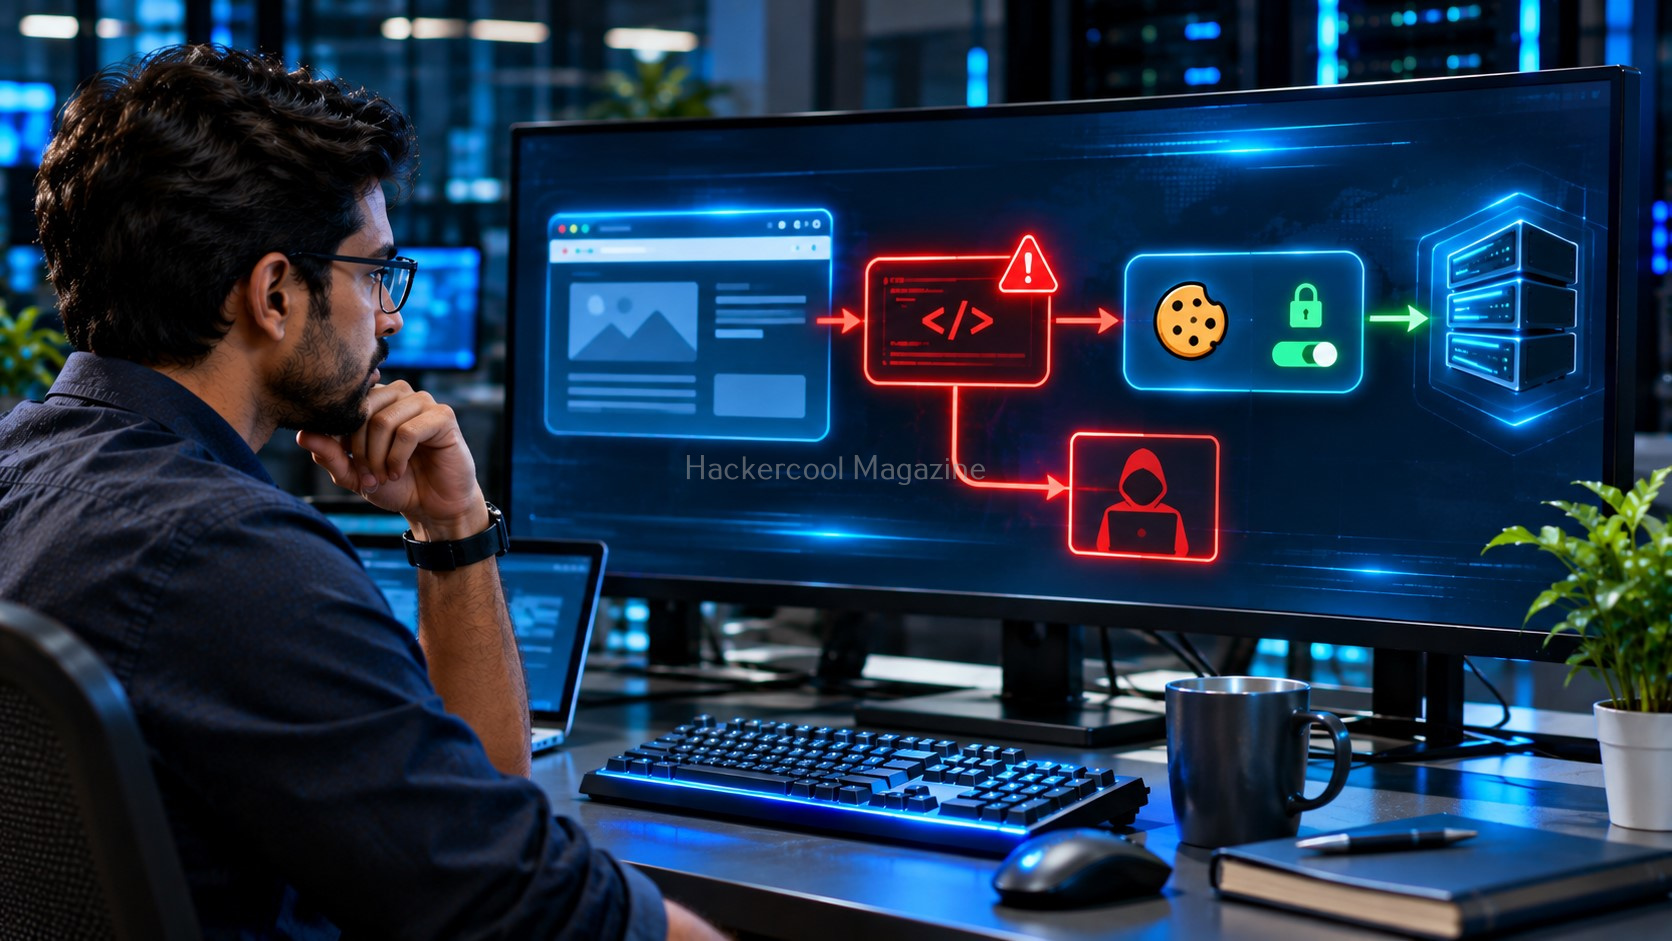
2. Cross-Site Scripting (XSS):
Cross-Site Scripting (XSS) can also allow attackers to execute malicious scripts in a victim’s browser and compromise session security.
Cross-Site Scripting is a web application vulnerability that allows attacker-controlled scripts to execute in a user’s browser. Depending on the vulnerability and browser protections, malicious scripts may be able to access sensitive information or perform actions in the context of the affected website.
Cookies marked with the HttpOnly attribute cannot be read directly through ordinary JavaScript. However, this does not eliminate every risk associated with XSS because malicious scripts may still perform actions through the victim’s browser.
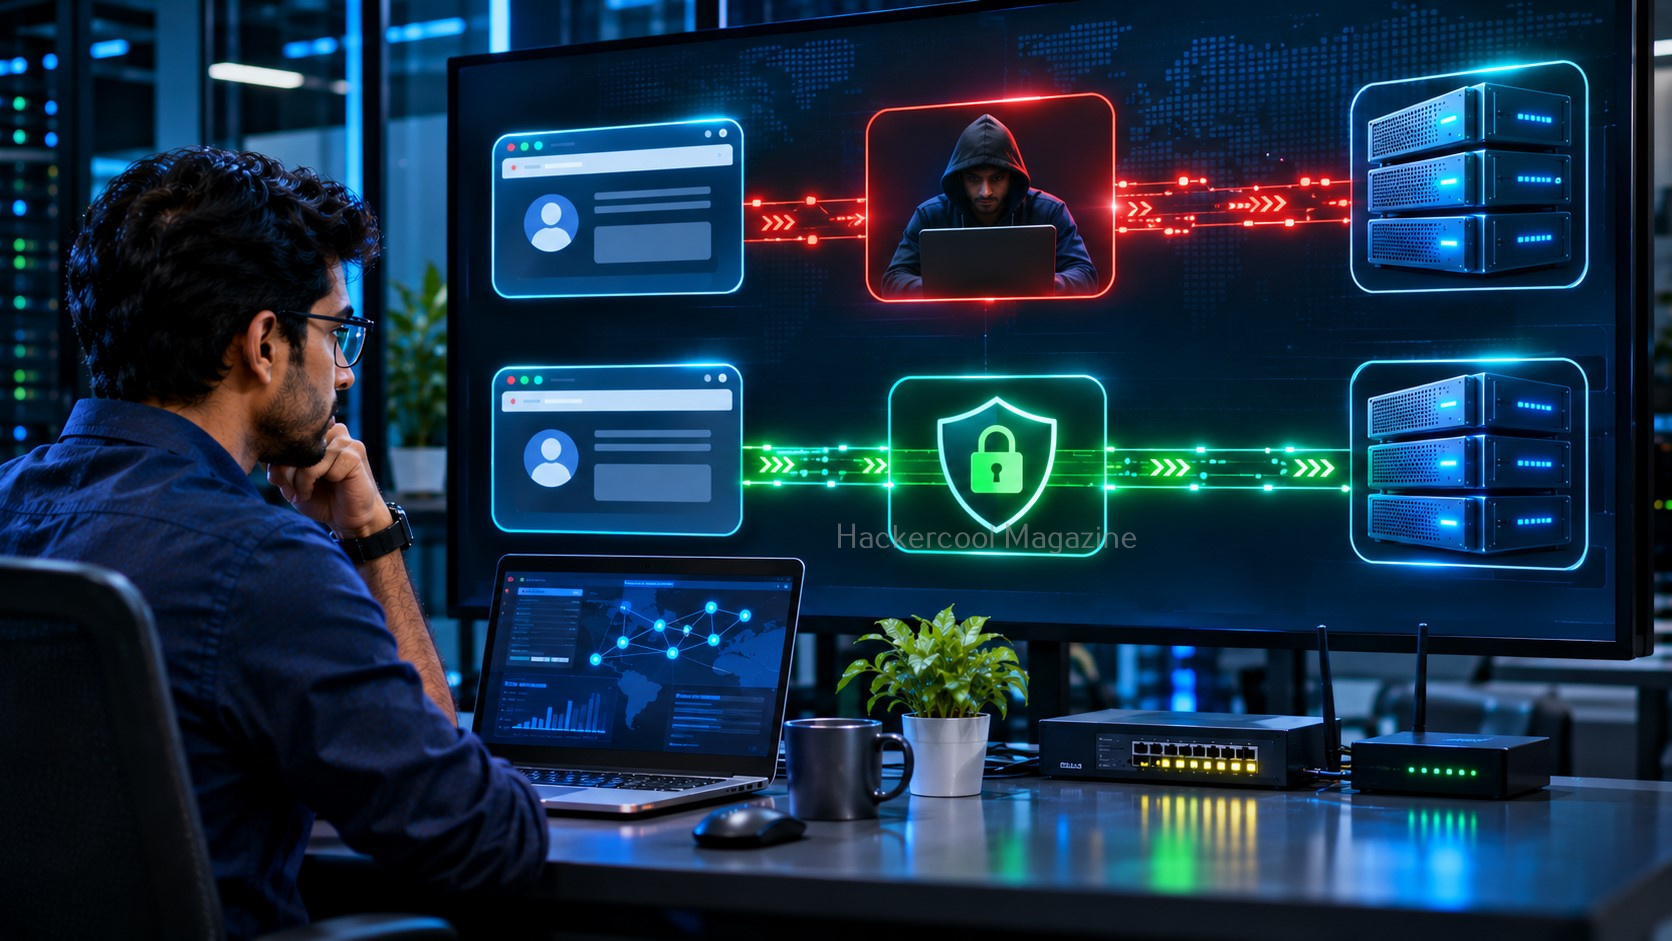
3. Man-in-the-Middle Attacks:
A Man-in-the-Middle (MITM) attack occurs when an attacker positions themselves between two communicating parties and attempts to observe or manipulate their communication. If a web session is transmitted without adequate encryption, session information may be exposed to interception.
Modern websites should use HTTPS to protect communication between browsers and servers. HTTPS helps prevent passive observers from reading session cookies in transit.
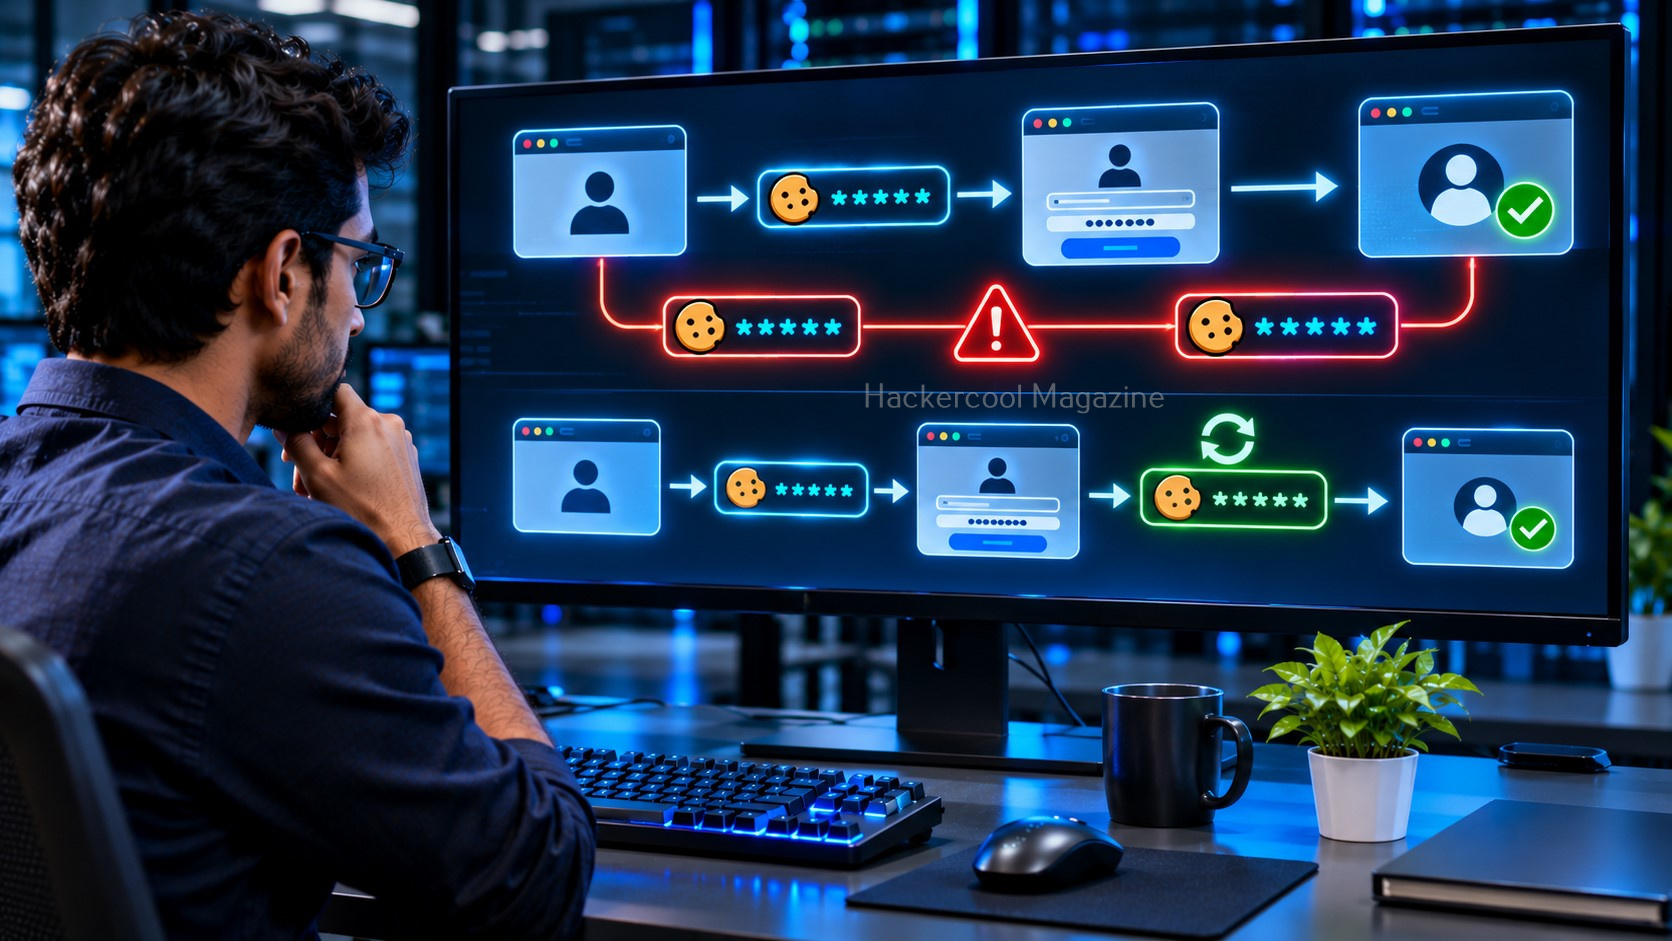
4. Session Fixation:
Session fixation is a related session-management attack in which an attacker attempts to make a victim use a session identifier already known to the attacker. If an application fails to issue a new session identifier after successful authentication, the attacker may be able to misuse the known identifier.
Regenerating session identifiers after login and privilege changes is an important defense.
5. Malware and Browser Compromise:
Malware running on a victim’s device may be able to access sensitive browser information or interfere with an active session.
For example, malicious software may compromise the browser environment or steal data stored by applications. Keeping operating systems, browsers and security software updated helps reduce this risk.
READY TO BUILD YOUR ETHICAL HACKING FOUNDATIONS?
Go beyond the basics. Develop the essential knowledge every aspiring ethical hacker needs.
Your learning package includes:
Networking Fundamentals
Linux Fundamentals
Windows Fundamentals
Web Fundamentals
Command Line Essentials
Virtual Labs
$1 INTRODUCTORY TRIAL
6 Foundation Resources + Full Magazine Access
Trial terms apply. Post-trial subscription billing is manual.
Attackers do not always rely on technical vulnerabilities to compromise user sessions. They may also use social engineering attacks to trick victims into revealing sensitive information or visiting malicious websites.
What Can an Attacker Do After Hijacking a Session?
The consequences depend on the account, the application and the permissions associated with the compromised session.
Possible consequences include:
- Accessing private account information.
- Reading messages or viewing personal data.
- Changing account settings.
- Performing actions as the authenticated user.
- Accessing business information or internal applications.
- Misusing privileges available to the compromised account.
For organizations, session hijacking can result in data exposure, unauthorized transactions, operational disruption and reputational damage.
How to Prevent Session Hijacking?
Preventing session hijacking requires a combination of secure application development, browser protections and good user security practices.
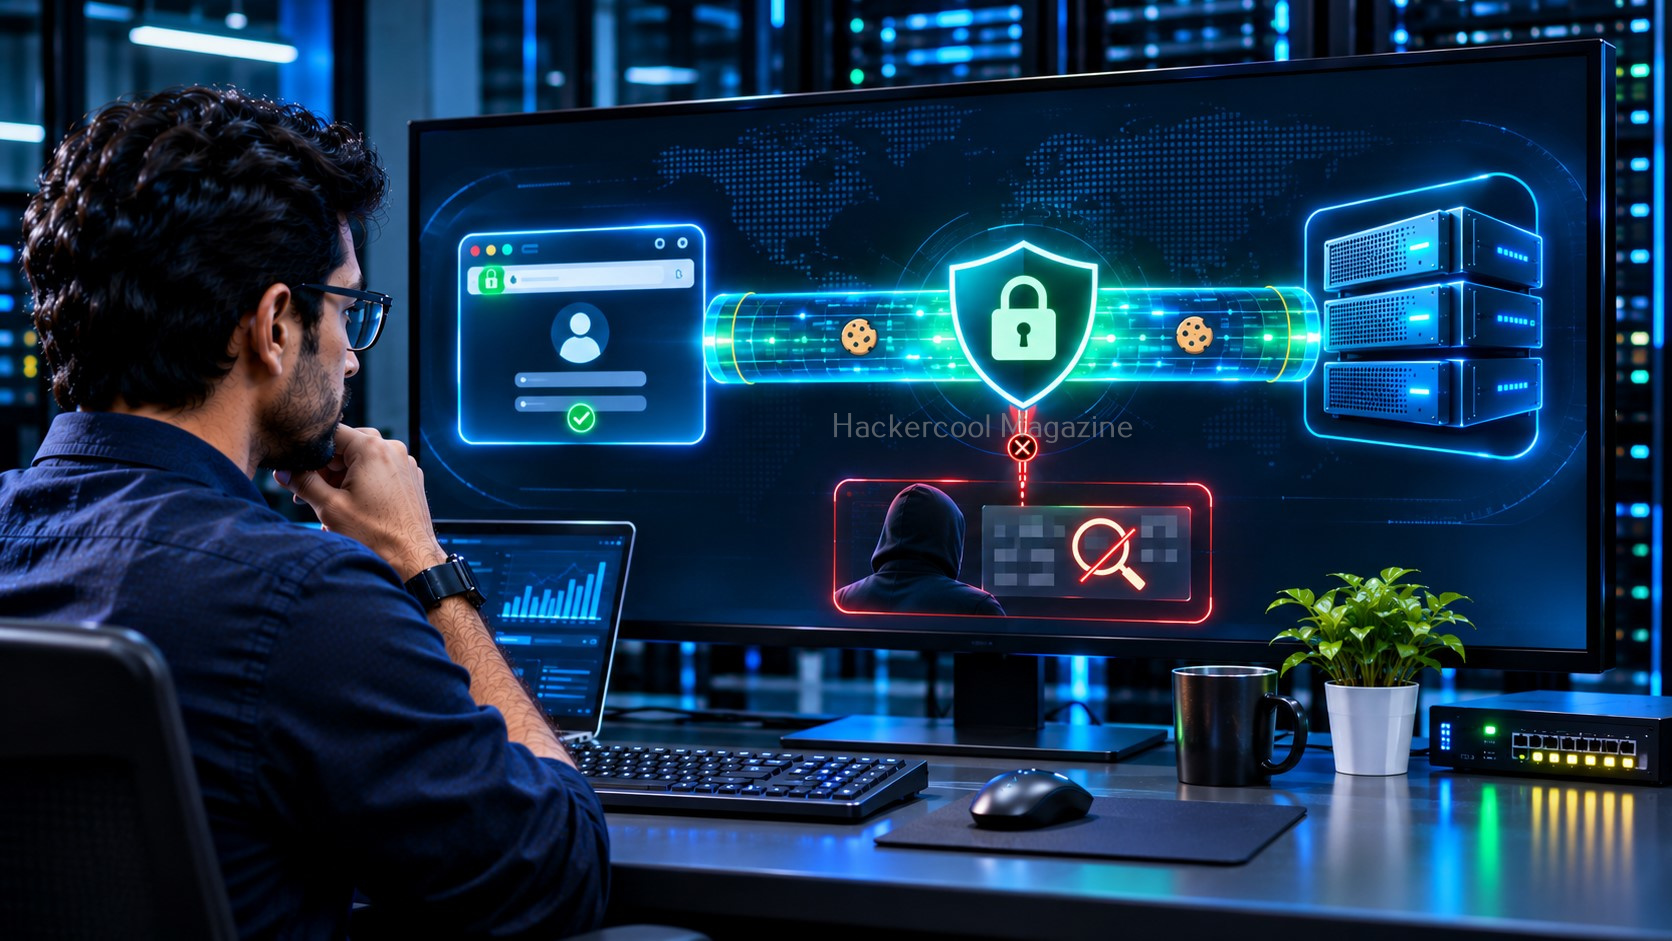
1. Always Use HTTPS
Websites should enforce HTTPS across the entire application, not just the login page. HTTPS encrypts communication between the browser and server, helping protect session information from interception in transit.
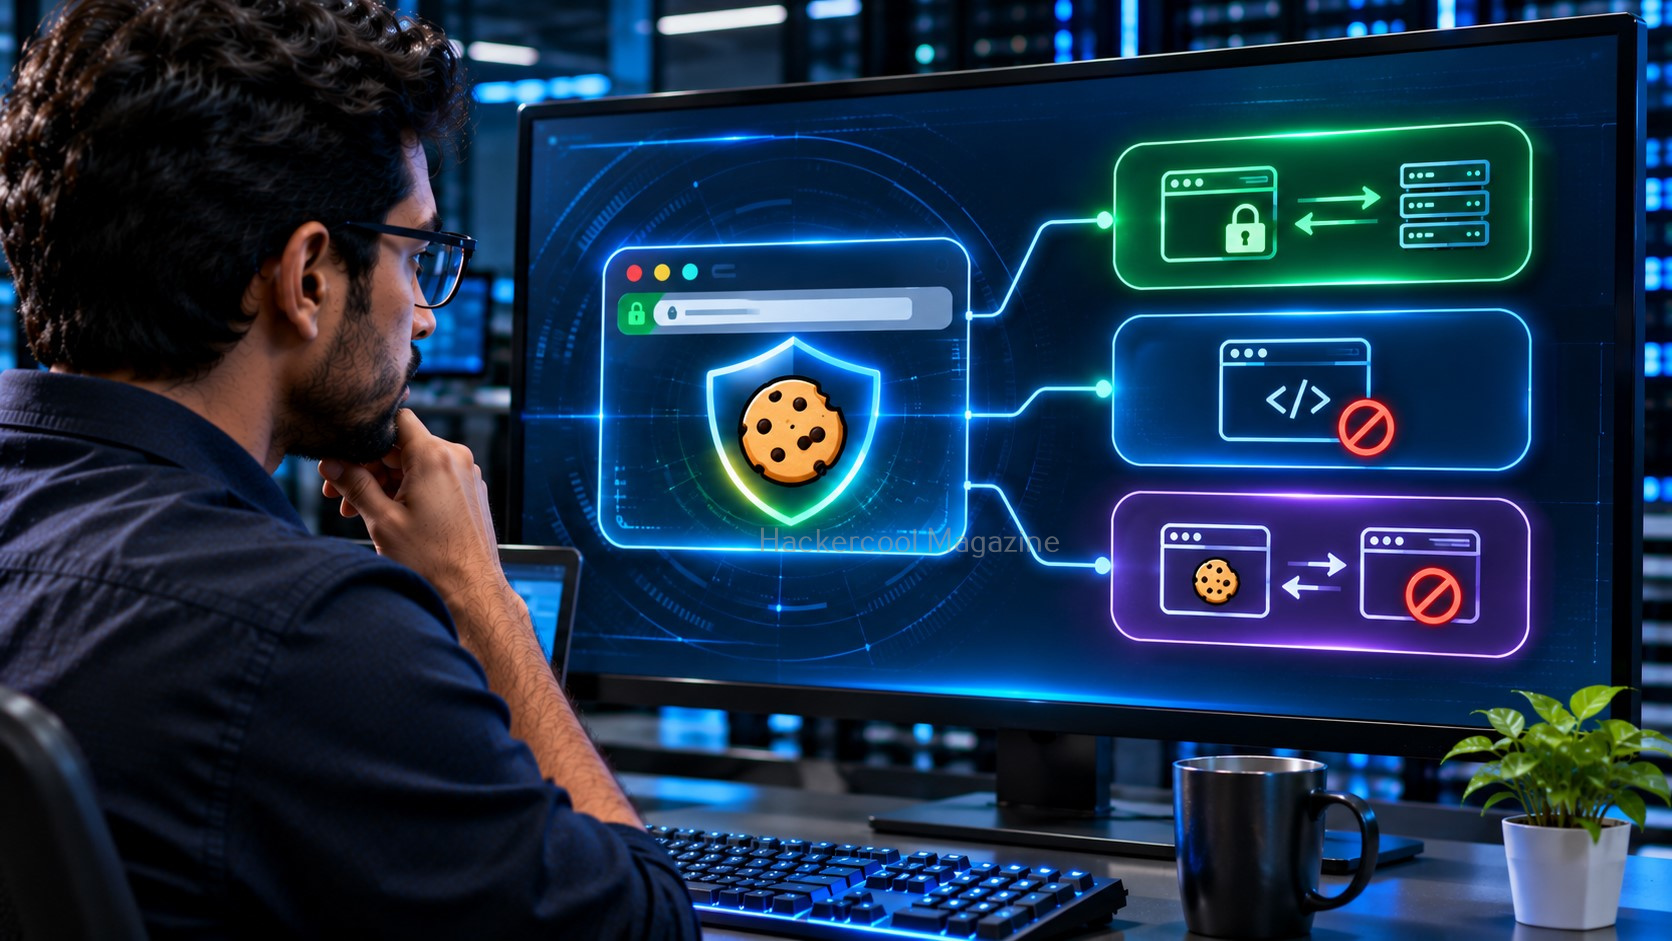
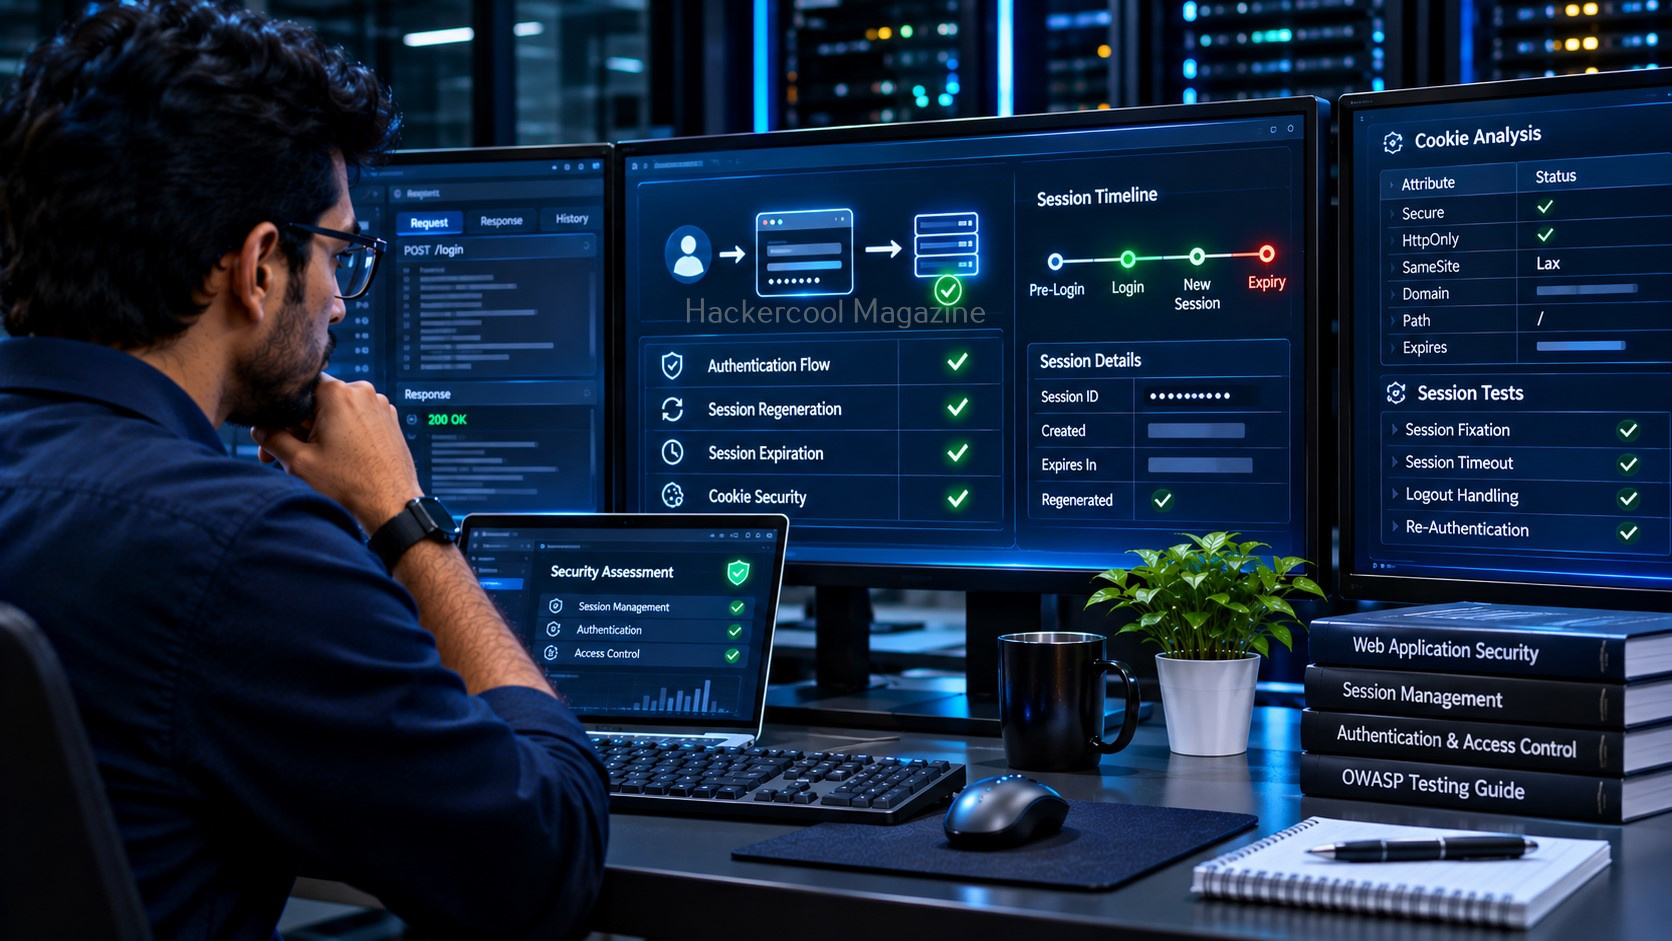
2. Set Secure Cookie Attributes
Developers should configure session cookies with appropriate security attributes:
- Secure: Sends the cookie only over HTTPS connections.
- HttpOnly: Prevents ordinary JavaScript access to the cookie.
- SameSite: Helps control when browsers send cookies with cross-site requests.
These attributes reduce exposure but should be combined with other security controls.
3. Generate Strong Session Identifiers
Session identifiers should be unpredictable and generated using a cryptographically secure random number generator. They should not contain usernames, email addresses, timestamps or other predictable information.
4. Regenerate Session IDs After Authentication
Applications should issue a new session identifier after successful login and important privilege changes. This helps defend against session fixation.
5. Set Session Expiration
Sessions should expire after an appropriate period of inactivity and have a reasonable maximum lifetime. Sensitive applications may require users to authenticate again before performing high-risk actions.
6. Monitor Suspicious Session Activity
Organizations should monitor unusual session behavior, such as unexpected changes in device or location, abnormal access patterns and repeated authentication anomalies.
Risk-based detection should be carefully designed to avoid treating every network or location change as proof of an attack.
7. Protect User Devices
Users should keep their operating systems and browsers updated, avoid untrusted software, use reputable security tools and protect their devices with strong authentication. They should also avoid logging in through suspicious links or untrusted devices.
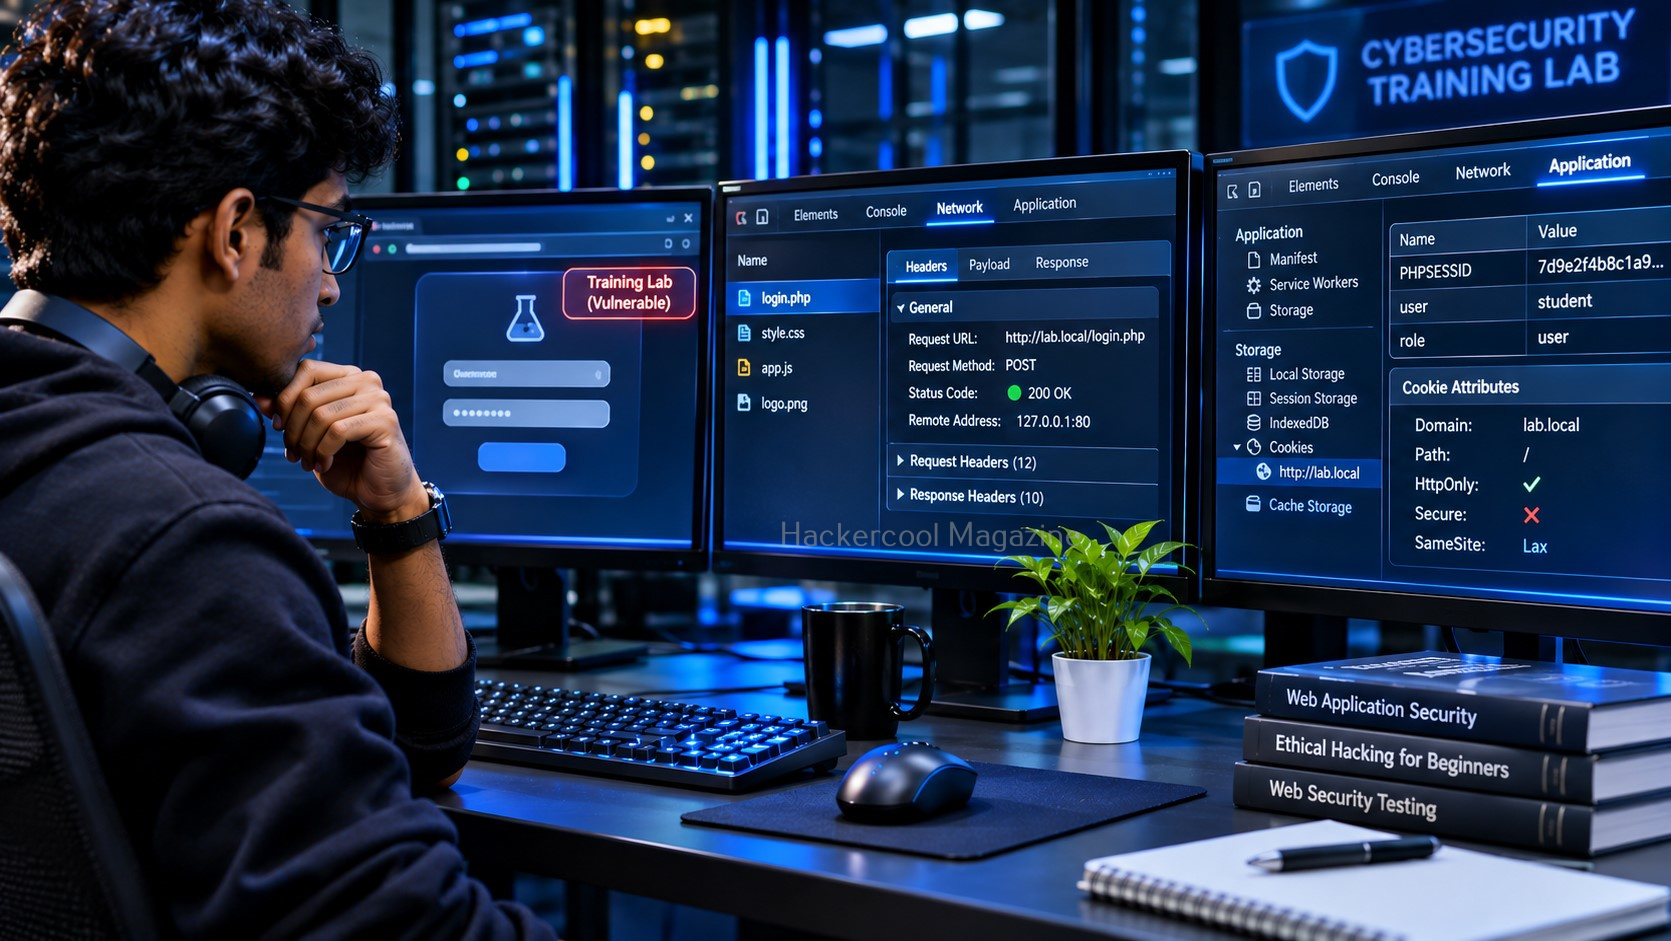
How Can Beginners Learn About Session Hijacking Safely?
Session hijacking is an important subject for anyone learning ethical hacking or web application security. Beginners can build a strong understanding without targeting real accounts or websites.
Start by learning:
- How HTTP requests and responses work.
- How browser cookies are created and stored.
- How authentication and session management operate.
- How HTTPS protects data in transit.
- How common web vulnerabilities affect session security.
You can then study session-management weaknesses in intentionally vulnerable applications and authorized training labs. Use only systems you own or have explicit permission to test. Never attempt to obtain or reuse another person’s session cookie or access an account without authorization.
Conclusion
Session hijacking is a serious web security threat because it can allow an attacker to impersonate an authenticated user without knowing their password.
Understanding how sessions and cookies work is the first step toward understanding this attack. Techniques such as session cookie theft, XSS, session fixation and interception can expose active sessions when applications or devices are not adequately protected.
For developers, secure cookie attributes, HTTPS, unpredictable session identifiers, session regeneration and sensible expiration policies are essential defenses. For users, keeping devices secure and avoiding suspicious links and software can reduce exposure.
For aspiring ethical hackers, session management is an important area of web application security to understand and assess only within authorized environments.
YOUR ETHICAL HACKING JOURNEY STARTS HERE!
Not sure where to begin? Download our FREE 18-page Beginner Ethical Hacker Starter Kit (2026 Edition).
Take your first step towards building practical cybersecurity knowledge.


