Hello, aspiring Ethical Hackers. In our previous blogpost, you learnt what is enumeration, why it is important in pen testing and what are the various types of enumeration. One important service commonly found in enterprise environments is LDAP (Lightweight Directory Access Protocol).
LDAP is widely used by organizations to manage users, computers, groups and other network resources. As it contains valuable directory information, understanding LDAP is an important step for anyone learning cybersecurity.
In this beginner-friendly guide, you’ll learn:
- What LDAP is
- How LDAP works
- What LDAP enumeration means
- Why LDAP is important
- Information that may be discovered
- Common beginner mistakes
- Safe ways to practice
New to Ethical Hacking?
Start your journey with The Beginner Ethical Hacker Starter Kit (2026 Edition).
Inside the free guide, you’ll learn:.
- Ethical hacking fundamentals
- Beginner cybersecurity roadmap
- Essential hacking tools
- Common vulnerabilities explained

What is LDAP?
LDAP stands for Lightweight Directory Access Protocol. It is a protocol used to access and manage directory services. A directory service acts like a central database that stores information about users, computers, printers, groups and other resources within an organization.
Instead of storing this information separately on every computer, organizations keep it in one centralized location. LDAP provides a standard way for applications and systems to search and retrieve that information.

Why is LDAP Important?
Imagine a company with thousands of employees. Without a centralized directory, every server and application would need its own list of users and passwords. Managing access would become extremely difficult.
LDAP simplifies this by allowing organizations to store and manage identity information in one place. Many enterprise services rely on LDAP for:
- User authentication
- Resource management
- Group management
- Device information
- Organizational structure

How Does LDAP Work?
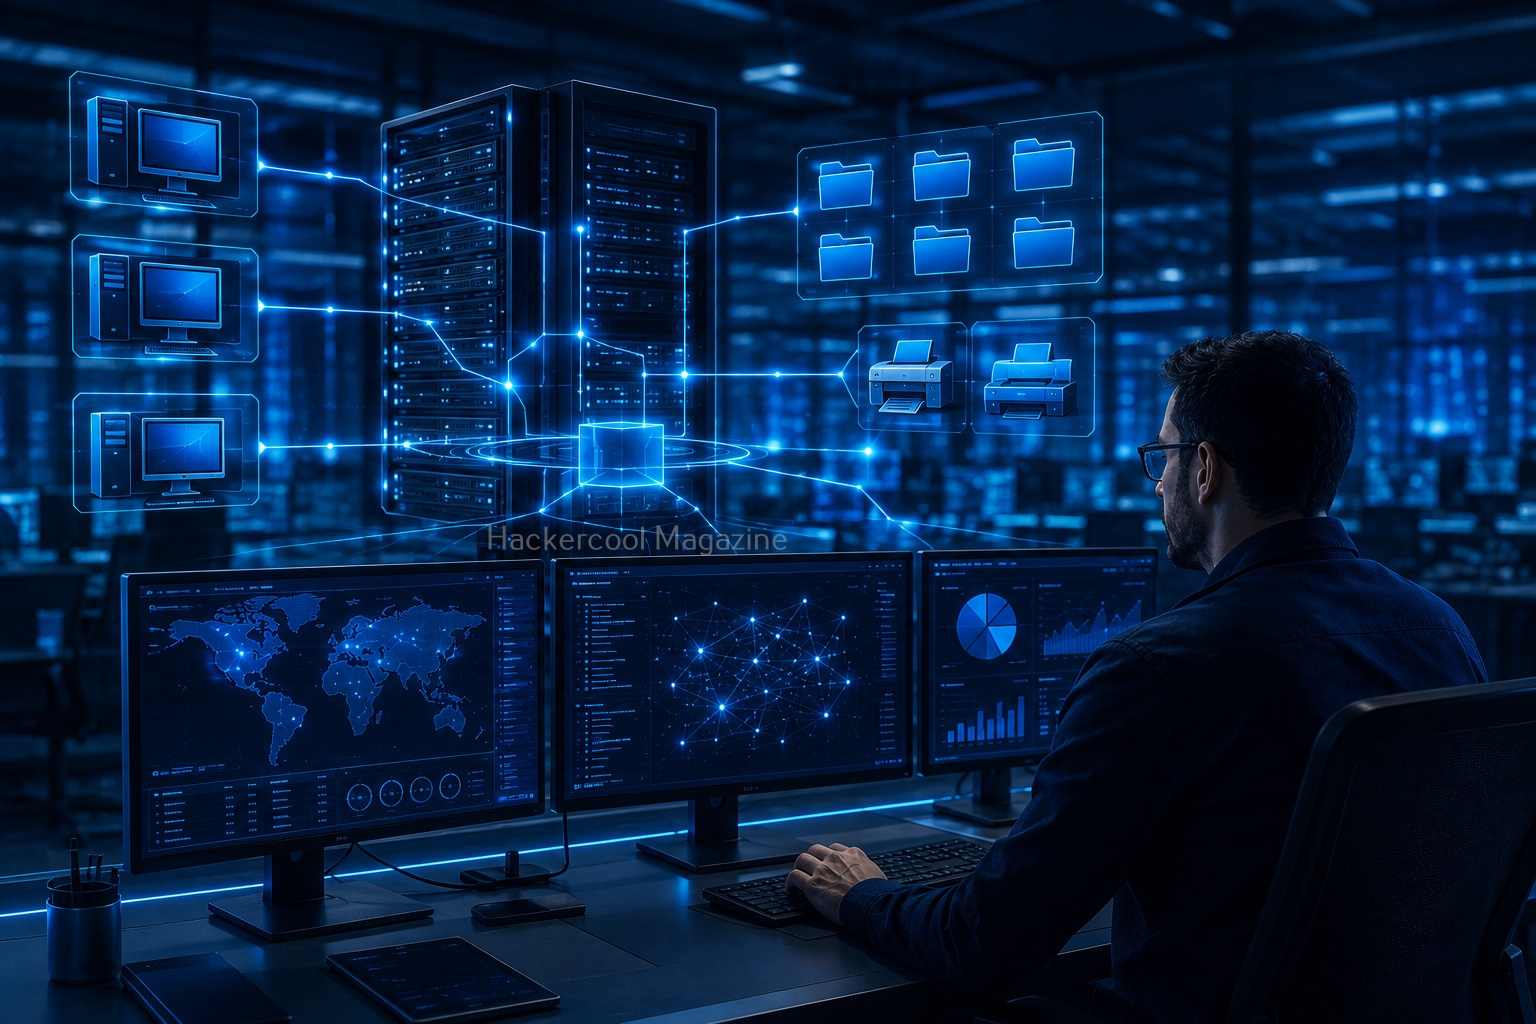
LDAP follows a client-server model. There are three main components in its working. They are,
LDAP Client:
The client is an application that sends requests to the directory service. For example, when an employee logs into an application, the application may query the LDAP server to verify the user’s identity.
LDAP Server:
The LDAP server stores directory information. It receives requests from clients and returns the requested information if the client has permission.
Directory Database:
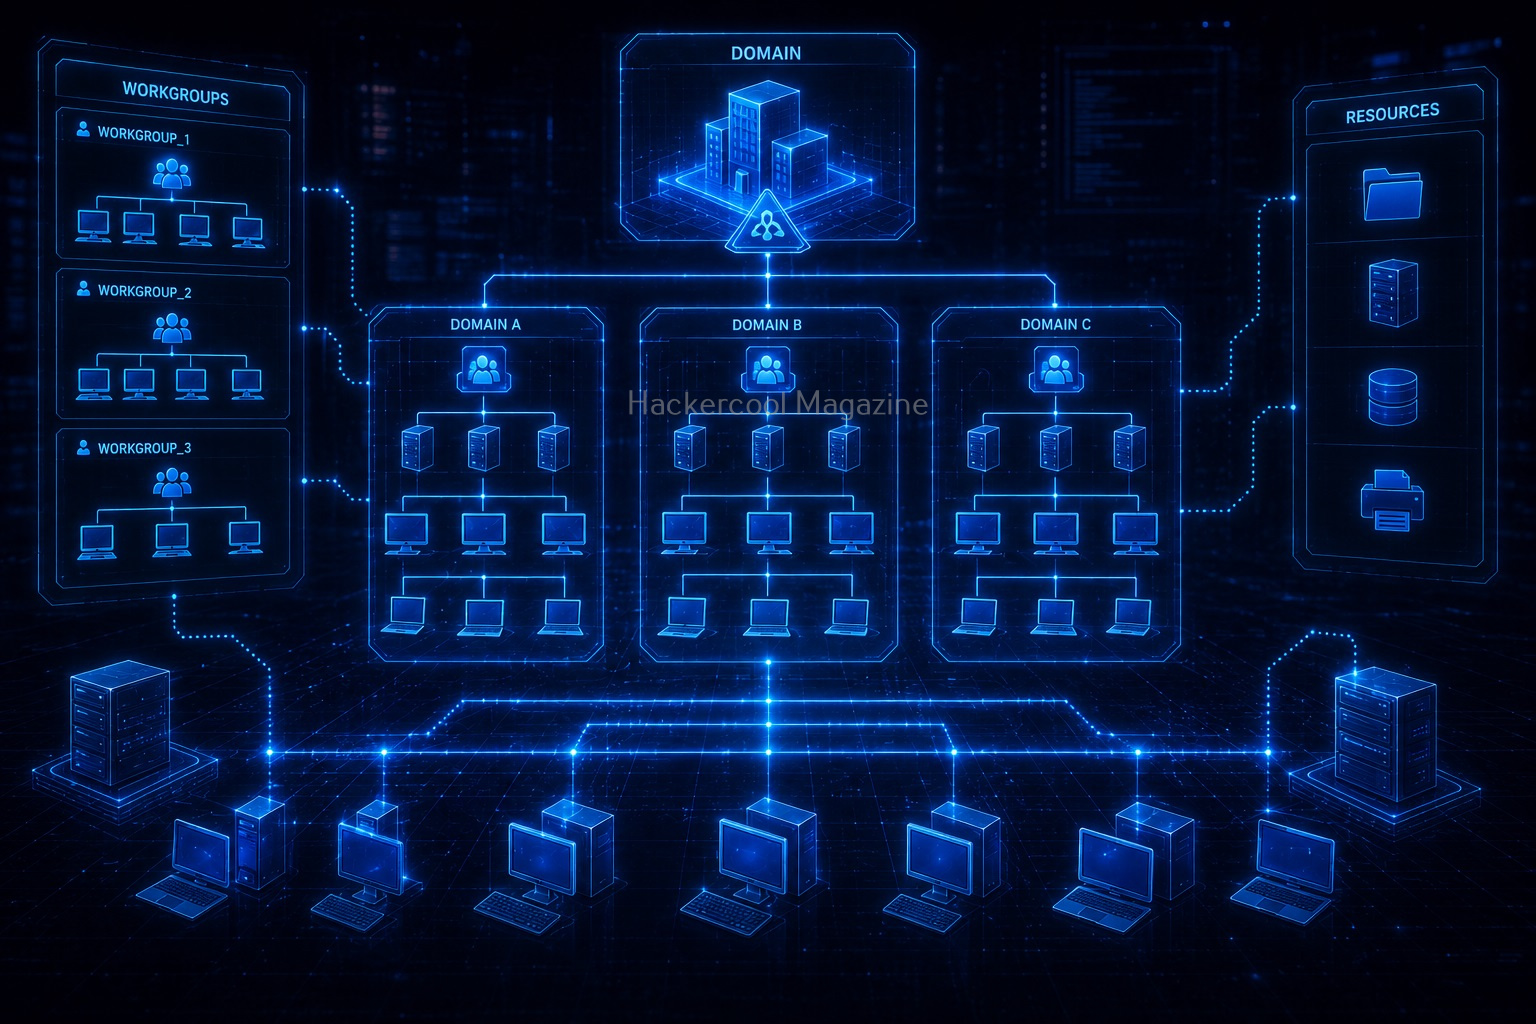
The directory contains structured information such as:
- User accounts
- Groups
- Departments
- Computers
- Printers
- Organizational Units (OUs)
This structure makes it easy to search for resources.

What is LDAP Enumeration?
LDAP enumeration is the process of gathering information from an LDAP directory during an authorized security assessment. The objective is to understand what information is available and how the directory is organized. This helps security professionals better understand an organization’s infrastructure.
Why Learn LDAP Enumeration?
Many enterprise environments rely on directory services.
Understanding LDAP helps beginners learn:
- Enterprise networking
- Identity management
- Authentication systems
- Directory structures
- Information gathering techniques
It also introduces important concepts used in Windows Active Directory and other directory services.
Information That LDAP Enumeration May Reveal
Depending on the directory configuration and access permissions, LDAP may contain useful information such as,

1. User Accounts:
Directory services often contain information about users. Some examples are,
- Usernames
- Display names
- Email addresses
- Departments
This helps administrators manage employee accounts efficiently.
2. Groups:
Organizations commonly organize users into groups. Examples are,
- IT Team
- Human Resources
- Finance
- Sales
Groups simplify permission management.

3. Organizational Units (OUs):
Large organizations divide resources into Organizational Units. These may represent:
- Departments
- Offices
- Geographic locations
- Business units
OUs help organize directory information logically.

4. Computer Objects:
LDAP directories often include computers joined to the organization’s network. Information may include:
- Computer names
- Operating systems
- Device descriptions
This helps administrators manage enterprise assets.
5. Network Resources:
Directories may also include information about,
- Printers
- Shared folders
- Applications
- Network services
These entries help users locate shared resources.

LDAP and Active Directory
Many Windows enterprise environments use Active Directory, which relies heavily on LDAP for directory queries. Although Active Directory provides many additional features, LDAP is one of the primary protocols used to communicate with the directory. Understanding LDAP helps beginners build a stronger foundation for learning enterprise Windows environments.
Why LDAP Matters in Cybersecurity?
Directory services contain valuable information. During authorized security assessments, understanding directory structures helps professionals:
- Identify users
- Understand organizational structure
- Discover systems
- Build an inventory of network resources
This information contributes to a better understanding of the environment before further security analysis.

LDAP Security Best Practices
Organizations should secure LDAP carefully. Some recommended practices include:
1. Restrict Directory Access:
Only authorized users and applications should be allowed to access sensitive directory information.
2. Use Secure Connections:
Many organizations use encrypted communication when accessing directory services to help protect sensitive information.
3. Apply Least Privilege:
Users should only have access to the information required for their job.
4. Monitor Directory Activity:
Unexpected access requests should be investigated. Monitoring helps identify unusual activity.
5. Review Directory Entries:
Regular reviews help remove outdated accounts and maintain an accurate directory.
Want to Learn Ethical Hacking Step-by-Step?
If you’re serious about learning cybersecurity, a structured roadmap makes the journey much easier.
Download The Beginner Ethical Hacker Starter Kit (2026 Edition) and discover:
✔ The ethical hacking learning path
✔ Beginner-friendly security concepts
✔ Essential tools ethical hackers use
✔ The most common vulnerabilities explained
Common Beginner Mistakes
Avoid these common mistakes while learning LDAP.
1. Confusing LDAP with Active Directory:
LDAP is a protocol. Active Directory is a directory service that uses LDAP. They are related but not identical.
2. Memorizing Commands:
Understanding the purpose of directory services is much more valuable than memorizing tool syntax. Focus on concepts first.
3. Ignoring Enterprise Networking:
LDAP makes more sense when you understand:
- User authentication
- Networks
- Domains
- Identity management
Study these topics together.
4. Poor Documentation:
Always document:
- Directory structure
- User groups
- Organizational Units
- Observations
Good documentation is an essential cybersecurity skill.
5. Practicing Without Authorization:
Only perform enumeration in:
- Home labs
- Virtual machines
- Authorized enterprise labs
- Cybersecurity training environments
Always obtain permission before performing security testing.

Safe Ways to Practice
You don’t need access to a corporate network to learn LDAP concepts. Safe practice options include,
Home Lab:
Build a virtual network using Windows or Linux virtual machines.
Directory Service Labs:
Many cybersecurity learning platforms provide simulated enterprise environments.
Study Active Directory Concepts:
Learning how organizations manage users and devices makes LDAP much easier to understand.
Practice Documentation:
Create diagrams showing directory structures, users and organizational units. This builds reporting skills.

A Simple Example
There are many tools that can be used to enumerate LDAP. For this article, let’s see how to perform it using a Nmap script. The nmap script we use is “ldap and not brute”.


Skills Developed Through LDAP Enumeration
Learning LDAP helps beginners develop several important cybersecurity skills.
Enterprise Infrastructure Analysis:
Understand how organizations manage identities and resources.
Information Gathering:
Learn structured methods for collecting technical information.

Identity and Access Management:
Develop an understanding of authentication and authorization concepts.
Investigation Skills:
Analyze how users, devices and resources are connected.

Documentation:
Record technical findings in a clear and organized manner.

Conclusion
LDAP is one of the most important technologies used in enterprise networks. Understanding how directory services work provides valuable insight into user management, authentication and organizational structure.
For beginners, learning LDAP enumeration is about much more than understanding a single protocol. It teaches how organizations manage digital identities and why directory services play such a critical role in cybersecurity.
Remember:
- Learn networking before advanced enumeration.
- Understand directory concepts before learning tools.
- Focus on how information is organized.
- Document your findings carefully.
- Practice only in authorized environments.
Mastering LDAP enumeration will strengthen your understanding of enterprise networks and prepare you for more advanced topics such as Active Directory security, identity management and penetration testing.
Start Your Ethical Hacking Journey Today
Learning cybersecurity can feel overwhelming at first. The best way to start is with a clear roadmap and the right resources.
Download The Beginner Ethical Hacker Starter Kit (2026 Edition) and get instant access to:
Ethical Hacking Fundamentals
A beginner cybersecurity learning roadmap
Essential hacking tools every beginner should know
Common vulnerabilities explained simply