Posted on

Beginners guide to DoS attack

Hello, aspiring ethical hackers. In this blogpost you will learn about DoS attack. In April 2007, the government services, financial institutions and various media outlets of Estonia, a nation in eastern Europe were hit with a massive Denial of service attacks. The attack that almost crippled Estonia (almost all services of Estonia are based only online) coincided with the relocation of “Bronze soldier of Tallinn” a world war II monument which Russia objected to. 

What is DoS attack?

DoS or Denial-of-Service attack is an attack that makes a website, service, network or software inaccessible to legitimate users. For example, imagine you are a user of Gmail. When you are trying to access Gmail to check an important mail sent from your office, you are unable to reach the servers of Gmail as there is a DoS attack on Gmail servers.

Types of DoS attacks

DoS attacks can be classified into three types. They are Volumetric attacks, Protocol attacks and Application layer attacks.

Volumetric attacks

In volumetric attacks, the bandwidth of the target network or service is exhausted, thus denying any legitimate users access to bandwidth. The magnitude of the attack is measured in bits-per-second (bps). Examples of these types of attacks are Ping of Death attack, UDP Flood attack, ICMP flood attack and Smurf attack.

1. Ping Of Death attack:

According to RFC791 IP, the maximum size of the packet should not exceed 65,535 bytes. In the Ping of Death attack, an attacker sends an oversized packet of size more than the prescribed limit with a ping request. (For example, a packet of size 65,550 bytes). The target system may crash while trying to reassemble this packet.

2. UDP Flood attack:

In this type of attack, an attacker sends a number of spoofed UDP packets to random ports of the target system. Target server tries to check for these applications (some of which are nonexistent) repeatedly. This causes exhaustion of the bandwidth in use thus replying to legitimate connections with a ICMP destination unreachable message.

3. ICMP Flood attack:

In the ICMP flood attack, the attacker sends a large volume of ICMP request (ping) messages to the target server either from a single IP or multiple IP addresses. The target server is bound to reply to these packets with a ICMP echo reply message thus exhausting the bandwidth.

4. Smurf attack:

In a smurf attack, the attacker sends ICMP echo request message to the broadcast network address spoofing the IP address of the target server. This makes all the devices in the network to reply to this echo request message with a echo reply message. Since the address of the target server is used in the echo request message, all the devices reply with this IP thus, making the target server inaccessible to the legitimate users.

Protocol attacks

In this type of DoS attacks, instead of exhausting the bandwidth, attackers try to exhaust resources available on the target network or website thus making it inaccessible to the legitimate users. Examples of these DoS attacks are SYN Flood attack, ACK Flood attack, TCP connection flood attack, Fragmentation attack and RST attack. This DoS attack is measured in Packets-per-second (pps).

1. SYN Flood attack:

In our blogpost on port scanning techniques, you learnt about the 3-way handshake.

In this attack, attackers exploit this 3-way handshake. How? The attacker sends multiple TCP SYN requests to the target server. When the target server responds to these SYN requests with a SYN/ACK packet, the attacker never sends a ACK message in response. This creates a partially open connection. By default, the target server or machines should track a partially opened connection for 75 seconds.

This is known as SYN flood. In these 75 seconds, the attacker can send large volume of SYN requests thus overloading the target system which eventually makes it inaccessible to the legitimate users.

2. Fragmentation attack:

Network or IP layer of OSI model allows packet fragmentation in order to overcome the problem of any higher-level protocol creating a packet larger than the size any particular local network supports. Attackers exploit this feature to send a large number (1500+bytes) of fragmented packets to the target server. The size of each fragment is usually reduced and small packet rate is used. This forces the target server to utilize a large number of resources to reassemble these fragmented packets thus causing DoS attack.

Application Layer attacks

In this type of DoS attacks, attackers exploit any vulnerabilities in the target server to prevent its access to the legitimate users. These vulnerabilities include cross site scripting, CSRF, File upload but most probably a Buffer overflow vulnerability. The magnitude of this attack is measured in requests-per-second (rps). Examples of this attacks include HTTP flood attacks and Slowloris attack.

1. HTTP GET/POST attack:

Browsers connect to the web server using HTTP requests. These requests can be either HTTP GET or HTTP POST. In this type of attack, attackers exploit these requests to perform DoS attacks.

In a HTTP GET DoS attack, attackers use time delayed HTTP headers to exhaust resources of webserver whereas in HTTP POST DoS attack the attacker sends HTTP requests with complete headers and without a message body or an incomplete message body.

Posted on

Beginners guide to Social Engineering

Hello, aspiring ethical hackers. In this blogpost you will learn about Social Engineering. Social Engineering is one of the most important techniques in Black Hat Hacking. It is used by APTs and Threat Actors even now.

What is Social Engineering?

Social Engineering is the art in which a human is convinced to perform actions which he is not intended to or shouldn’t be performing under normal circumstances. Hackers use social engineering to grab credentials, gather any required information about the organization or to gain initial access etc. It exploits human emotions like intention to trust, curiosity and other emotions.

Types of Social Engineering

Social Engineering can be classified into three types. They are: Human based, Computer based and Mobile based.

social_engineering

Human based Social Engineering

In human based social engineering, hacker interacts with a human personally to perform the attack. There are many types of social engineering attacks. Some of them are,

1. Dumpster diving:

Dumpster diving is a technique in which a hacker searches the dump or dustbin to gather any information about the organization.

2. Impersonation:

In this attack, attacker impersonates as another user to gather important information about any organization or performing hacking attacks. Any information obtained in dumpster diving can be useful in this stage. Obviously, an attacker will impersonate as a legitimate user of the organization or a person of authority or anyone else who has a chance to enter a company physically or virtually.

In June 2023, hacking group tracked as “Pink Drainer” impersonated journalists in phishing attacks to gain access to 1932 Discord and Twitter accounts. They stole approximately $29,97,707 worth of cryptocurrency.

3. Piggybacking:

Piggybacking is used to gain access to the premises of a company or organization. In piggybacking, a genuine employee of an organization allows access to the attacker because he/she thinks that the attacker has genuine reason to be on the organization’s premises. It usually happens when the hacker impersonates as anyone who is allowed into company’s premises. For example, delivery boy, technician etc.

4. Tailgating:

In tailgating, which is another social engineering techniques to gain illegal access to the company’s premises, a hacker tries to gain access to the company’s premises by quickly following behind a legitimate or genuine user immediately after he/she gains access into company’s premises.

5. Eavesdropping:

Eaves dropping is secretly listening to the conversation of employees of the organization etc. This can happen anywhere but mostly happens at recreational spots.

6. Shoulder surfing:

Shoulder surfing is the technique in which an attacker spies on the legitimate users of the organization by staying behind them. Shoulder surfing is normally used to see the legitimate user is entering his credentials but it can also be used to gather any valuable information.

7. Vishing:

In vishing, also known as voice phishing, a hacker uses voice over a phone or a VOIP call to perform social engineering.
In July 2020, hackers used vishing to trick Twitter employees into revealing account credentials of 130 Twitter account including that of Barack Obama, Joe Biden and Kanye West. The share value of Twitter plummeted by 7% after this incident.

8. Pretexting:

In pretexting, attacker creates specific scenarios or events by which the user he is targeting reveals information he/she makes.

Computer based Social Engineering

When a computer is used in an engineering attack, it is known as computer based social engineering attack. There are two types of computer based social engineering attacks. They are,

1. Phishing:

In phishing, attackers create a fake website (impersonating a genuine website) and divert the target users to this fake website to grab their credentials or make them download malware. There are multiple examples of hackers creating a fake phishing website to steal credentials, credit card information or other sensitive information. In August 2023, Supreme Court (the highest court of India) warned users about a fake website impersonating website of the Supreme Court trying to solicit personal details and confidential information from users. See how to perform phishing attacks with Weeman HTTP server and GoPhish.

2. Spear Phishing:

In spear phishing, a hacker selects specific users as targets and sends them an email with malware attached to the email and luring them to download and execute the attached payloads or take some other action. In February 2022, Russian hacking group known as Gamaredon, targeted Ukrainian government agencies and NGO’s with a spear phishing email campaign with malware laden emails.

Mobile based SE

If an engineering attack uses mobile it is known as mobile based social engineering. SMishing is a type of mobile based social engineering attack.

1. SMishing:

SMishing or SMS phishing is a phishing attack which is performed by sending a SMS to the target user’s mobile phone with a link to the fake website attacker created. In 2020, cyber criminals sent SMS messages to various user’s mobile phones asking them to click on a link to view important information about an upcoming delivery from United States Post Office (USPS). When users clicked on the links in these SMS, it took them to a malicious website that was designed to steal user’s Google account credentials.

Learn about Social Engineering Toolkit (SET), an open-source framework to perform a variety of social engineering attacks.

Posted on

Password sniffing tutorial for beginners

Hello, aspiring Ethical hackers. In this article, you will learn about password sniffing. You should have observed that almost all the websites you have visited recently have a padlock sign and begin with HTTPS now. Google started giving minor ranking boost to websites with HTTPS enabled since year 2014. As you will learn by the end of the blogpost, there is a good security reason behind this.

What is Password sniffing?

Password sniffing or Credential sniffing is sniffing or capturing of credentials (or any other data) while they are in transit from one machine to another machine (usually from client to server). Password sniffing is only possible when plain text protocols are in use. Plain text protocols are those protocols in which confidential information like usernames and passwords are passed to the server in complete plain text and without any encryption.

This allows anyone in middle to sniff on these usernames and passwords. Examples of plain text or clear text protocols are FTP, Telnet, SMTP, HTTP, IMAP, POP3, TFTP etc. Let’s see password sniffing practically. In this article, we will demonstrate the basic level of password sniffing on plaintext protocols. For this, we will be using three virtual machines which are on the same network.

They are  Metasploitable 2 which acts as server, Ubuntu which acts as client and of course Kali as our Attacker system.  As you can see, the IP addresses of the three machines are

     Metasploitable2 – 192.168.64.128 (Server)

     Ubuntu – 192.168.64.132 (Client)

     Kali – 192.168.64.132 (Attacker system)

Let’s start Wireshark on the attacker machine (on interface eth0). It starts capturing packets on the network.

The reason why we are using Metasploitable 2 as our target is that it already has many services that we need for this tutorial preinstalled.  The first service we will be using is Telnet. It is a protocol that is used for remote access on another system. On most Linux systems, Telnet clients are installed by default.

So we open a terminal and log into the Metasploitable 2 Telnet server with the credentials shown below.

The login is successful. Now on the Attacker system, we can observe the traffic being captured by the Wireshark sniffer. You can see data related to Telnet being transferred.

We can Right Click on that Telnet data stream and click on “Follow” as shown below.

In the sub menu that opens when we click on the only option “TCP stream” a new window opens that will show only the TCP stream.

In this window, you can see the credentials we just used to login into the target system. Telnet is a plain text protocol which transfers credentials and other sensitive data in plain text. This allows sniffing of data. That’s the reason it has been mostly replaced by Secure Shell (SSH) nowadays.   

Let’s see another protocol. File Transfer Protocol (FTP) is a protocol that is used to share files. It is another protocol that transfers data in plain text. From our client, we login into the FTP server with credentials “anonymous:anonymous”.

Anonymous account in FTP is used to share files to anyone without the need for them to know credentials.

On the Wireshark interface, you can see FTP data being transferred.

We can view the TCP stream

This once again shows credentials.

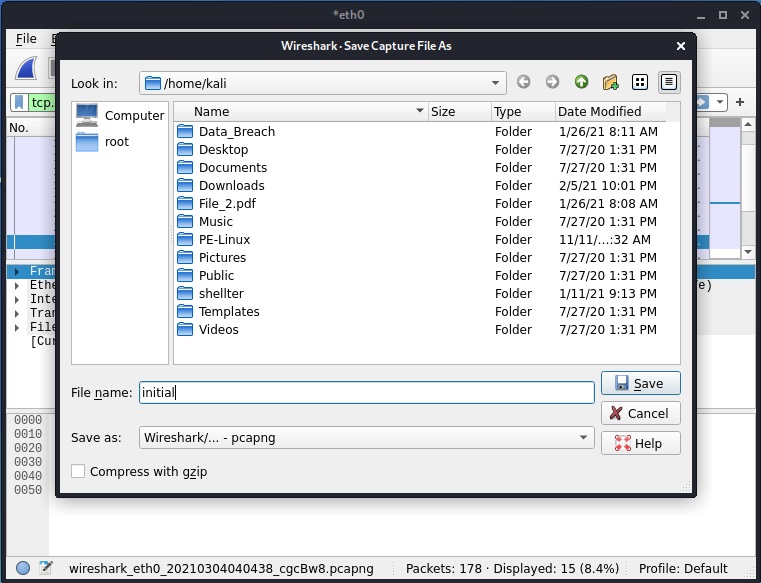
Instead of observing LIVE data transfer and following TCP stream from there, we can also just save the packet capture file and open the file later for analysis.

After opening the file, we can search for specific terms as shown below. 

packet sniffing

Then following the TCP stream gives us the credentials.

Seeing the vulnerability due to sniffing, many protocols have been replaced with secure protocols which transfer data in encrypted form instead of plain text form. These are given below.

Posted on

Beginners guide to Steganography

Hello aspiring Ethical Hackers. In this blogpost, you will learn about steganography. Before you learn what is it, you need to learn why are we learning about it. In Feb 2023, Red Eyes Hacking Group (APT37) used a jpg image as attachment in one of their spear phishing email. When victims clicked on this image, it triggered an exploit that ran shellcode on the victim’s computer to download and execute a malicious payload that is stored within the jpg file mentioned above. But how was the malicious payload was hidden inside the jpg image?

What is Steganography?

It is an art or technique of hiding secret or any precious information inside something that looks common & ordinary. This information is hidden in such a manner that its presence is not evident to the human inspection. The word stegano graphy came from Greek word steganographic, that is combination of words steganos (meaning hidden or concealed) and graphia (writing).

In ancient and medieval times, kings used steganography to forward messages secretly. Greeks were the fist to use it. Coming to modern times, hackers are using it to hide malicious code in images, text, files, audio, video film and any other medium that looks benign.

Types of Steganography

There are five types of stegano graphy. They are,

  1. Text stegano graphy
  2. Image stegano graphy
  3. Video stegano graphy
  4. Audio stegano graphy
  5. Network Stegano graphy
steganography

1. Text Steganography::

In text steganography, the secret information is hidden in a piece of text. For example, let’s say a text contains “Indians love Unity”. This may look like an ordinary or normal text. But just take the first letter of these three words. That becomes “ILU” a shortcut for I Love You message used by youngsters.

2. Image Stegano graphy:

As you might have already expected, when the secret information is hidden in an image (digital image) it is known as Image steganography.

3. Audio Steganography:

If the information we want to hide is hidden in an audio, it is known as audio steganography. Humans can hear sound that only contains certain frequencies. So, by altering the properties of audio like frequency, amplitude etc. secret messages can be hidden. However, to be able to receive and understand this secret information, the receiver needs to have smart listening devices to decipher the hidden information.

4. Video Steganography:

If the secret information is hidden in a video, it is called video steganography. A video is simply a representation of a sequence of consecutive images. So, we can say that this is an advanced version of Image steganography.
5. Network Steganography:

Considered to be more advanced and practically useful to Black Hat Hackers, in Network steganography information is hidden in network traffic. For example, it can be hidden in the TCP/IP headers etc.

Examples of Steganography attacks in hacking

  1. In September 2022, researchers at ESET discovered a previously unknown Threat actor they named Worok hiding malicious payload in PNG files.
  2. In 2019, researchers at Symantec observed a Russian cybersecurity group waterbug (also known as just the malicious) delivering a publicly known backdoor by hiding it in a WAV file.
  3. In the same year, security researchers at Cylance observed a hacking campaign that was delivering XMRIG Monero CPU miner by hiding them in WAV files.
  4. PLATINUM hacker group, that usually targets Governments of South Asia and South East Asia, embedded their malware commands in the HTML code of a website. They achieved this by encoding malware commands in a specific sequence of “TAB” and “SPACE” bar.

In future steganography is going to increase in cyber security.

Posted on

Privilege Escalation Guide for Beginners

Privilege escalation is one of the most important concepts beginners encounter when learning ethical hacking and penetration testing.

Getting initial access to a system is often only one part of a security assessment. An account or process may have limited permissions while sensitive files, administrative settings, security controls and critical systems require higher privileges. Understanding how permissions are assigned and how misconfigurations can allow those permissions to be abused—is therefore an essential cybersecurity skill.

This guide explains privilege escalation from a beginner’s perspective, including the difference between horizontal and vertical privilege escalation, common Linux and Windows weaknesses, a typical assessment methodology and safe ways to practice.

Important: Privilege-escalation techniques should only be tested on systems you own or have explicit authorization to assess. Use intentionally vulnerable labs, virtual machines and training platforms.

What Is Privilege Escalation?

Privilege escalation occurs when a user, process or application gains access to resources or capabilities beyond what it was originally authorized to use.

Imagine a system with three users:

  • A standard user
  • A department administrator
  • A system administrator

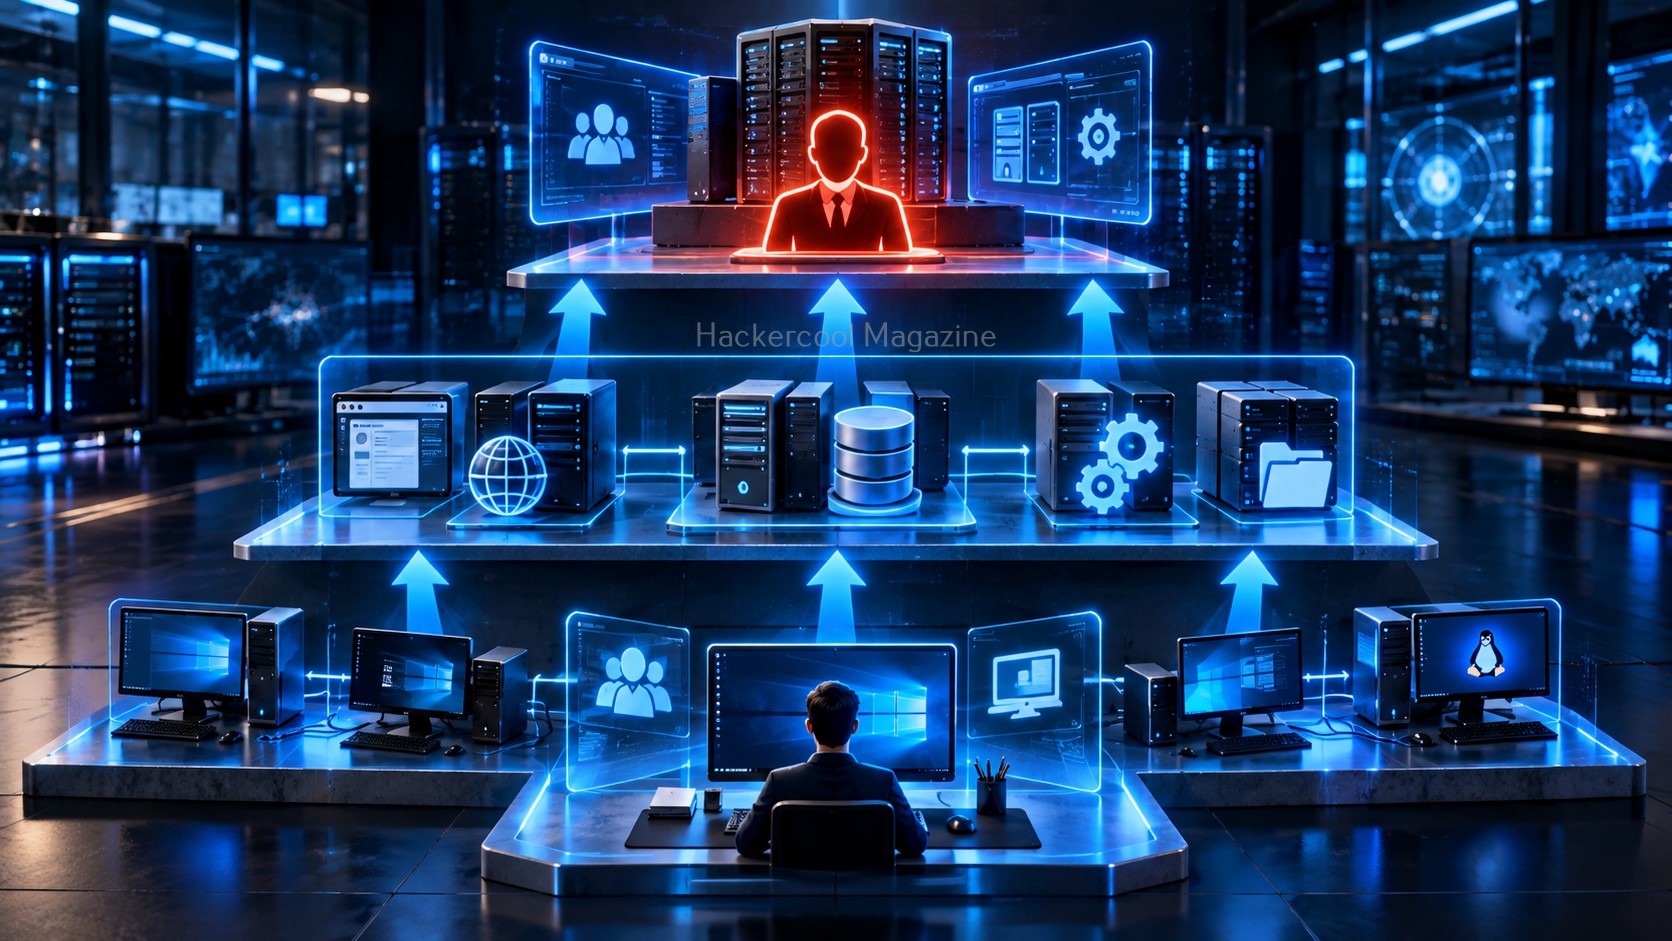
If the standard user discovers a legitimate path to administrator-level permissions because of a security weakness, that situation represents privilege escalation. The same concept applies to servers, workstations, cloud environments, applications and enterprise identity systems.

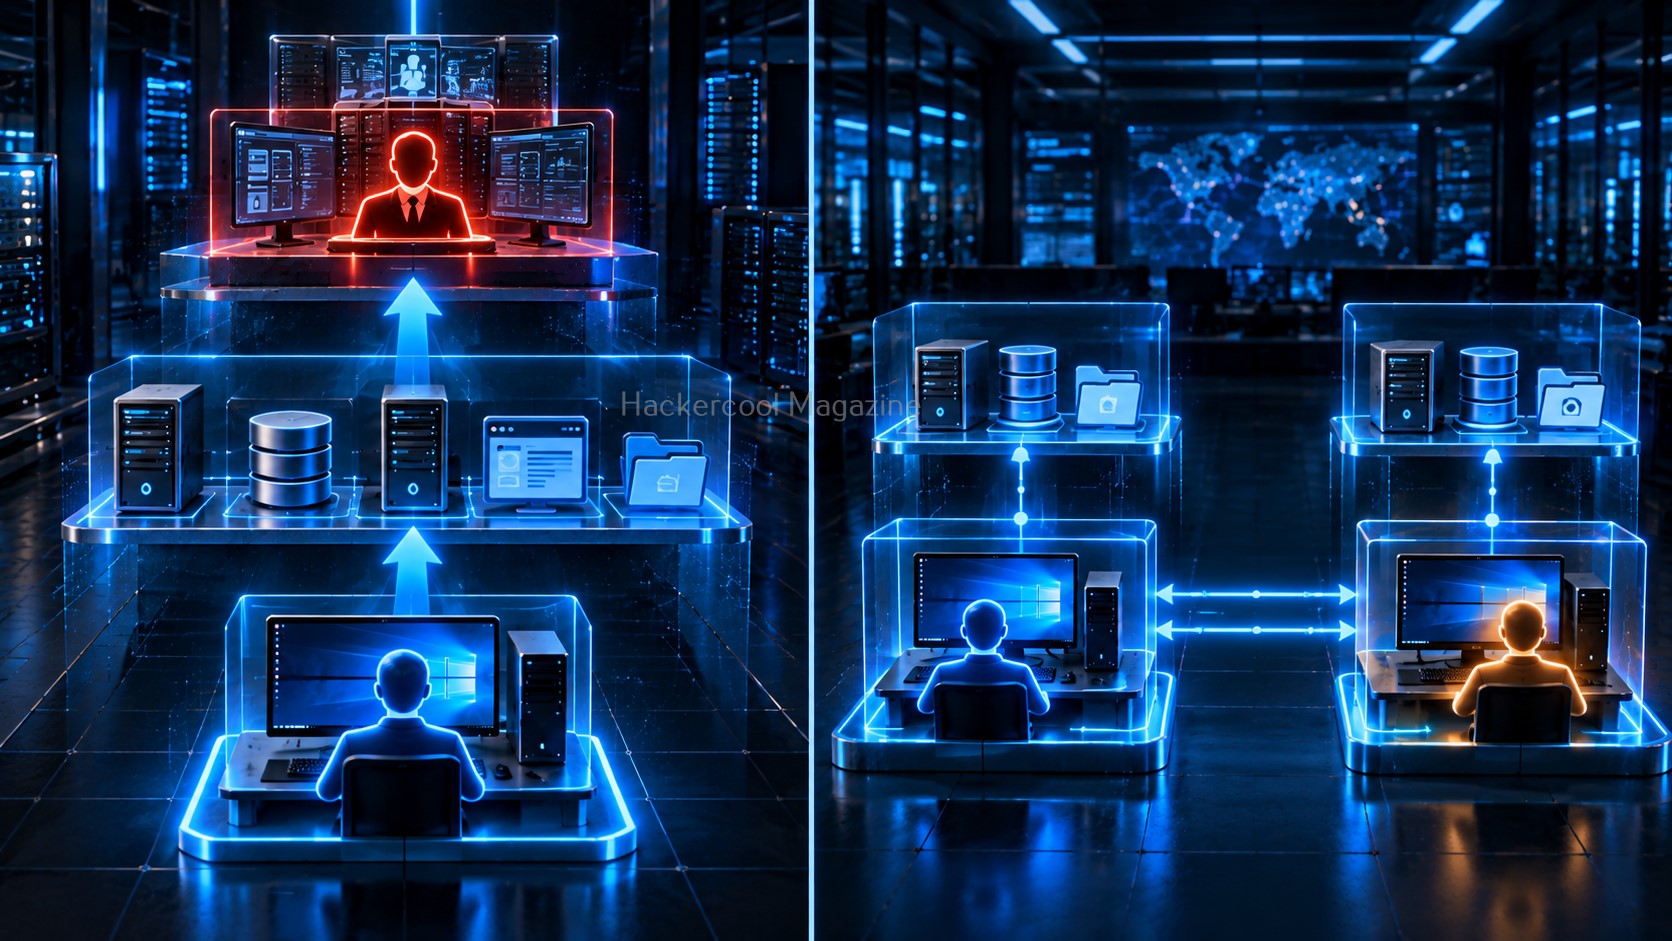
Privilege escalation is generally divided into two categories. They are,

Vertical Privilege Escalation:

Vertical escalation occurs when a lower-privileged user gains higher privileges.

For example:

Standard User → Administrator → System-Level Access

This is the type most beginners associate with privilege escalation.

Horizontal Privilege Escalation:

Horizontal escalation occurs when one user accesses resources belonging to another user with a similar privilege level.

For example, imagine two ordinary accounts:

User A → User B’s Account or Data

The attacker may not become an administrator but accessing another user’s resources can still represent a serious security problem. Understanding this distinction is important because not every privilege problem involves becoming a system administrator.

Why Does Privilege Escalation Matter?

Organizations use permissions to limit what users and applications can do. A normal employee may need access to business applications but should not necessarily be able to modify security settings, install arbitrary software or access another employee’s confidential files.

Privilege separation reduces the impact of compromised accounts. If an attacker compromises a standard account and discovers that the account can immediately obtain administrative privileges because of a configuration mistake, the security boundary becomes much weaker.

This is why penetration testers don’t stop after obtaining an initial foothold. They examine what that access actually allows.

How Privilege Escalation Fits Into a Security Assessment

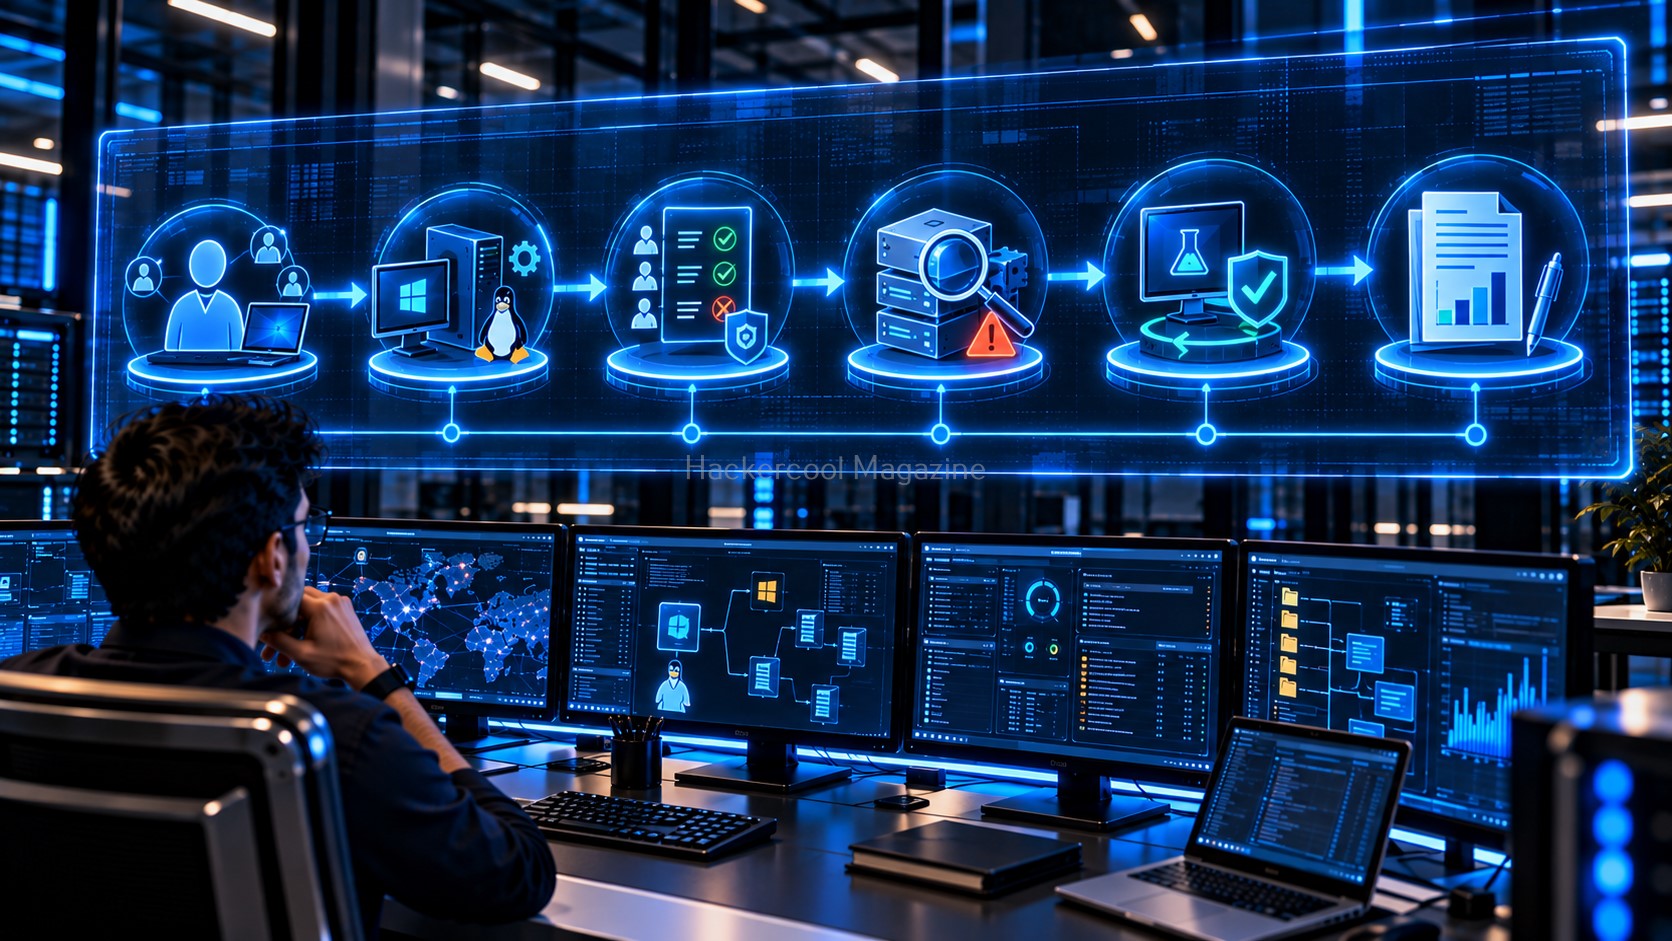
A simplified penetration-testing workflow might look like this:

Reconnaissance → Initial Access → Enumeration → Privilege Assessment → Privilege Escalation → Impact Analysis → Reporting

Privilege escalation generally happens after some level of access has already been obtained.

The tester asks questions such as:

  • What account am I using?
  • What permissions does this account have?
  • What groups is it part of?
  • Which applications are running?
  • Which files are accessible?
  • Which services operate with elevated privileges?
  • Are there incorrectly configured permissions?
  • Are outdated components present?
  • Are credentials or secrets unnecessarily exposed?
  • Are administrative functions restricted correctly?

The important lesson is that enumeration comes before exploitation. Beginners sometimes immediately search for an exploit. A better approach is to first understand the system.

Linux Privilege Escalation

Linux systems use a permission model involving users, groups, files, processes, services and administrative privileges.

A beginner learning Linux privilege escalation should first understand:

Users and Groups

Linux permissions are strongly connected to users and groups. A file might belong to one user and group while allowing different levels of access to the owner, group members and other users. Understanding this model is more important than memorizing individual privilege-escalation tricks.

Sudo and Administrative Permissions

Linux systems can allow selected users to perform certain administrative operations. Misconfigured administrative permissions can create security risks. For example, giving a user permission to perform a powerful administrative operation without sufficient restrictions can potentially allow that user to cross a security boundary.

This is why security assessments examine administrative permissions carefully.

File and Directory Permissions

Incorrect ownership or overly permissive access controls can expose sensitive information or allow unauthorized modification.

A beginner should learn how to reason about:

Owner → Group → Permissions → Sensitive Resource

rather than simply looking for a particular command or exploit.
Services and Scheduled Tasks

Background services and scheduled processes may run with higher privileges. If such a process interacts with files, scripts or other resources that lower-privileged users can modify, the configuration may create a privilege-escalation risk.

This is an important security concept because the weakness can come from the relationship between two individually legitimate components.

Windows Privilege Escalation

Windows privilege escalation has a different ecosystem but follows many of the same underlying principles.

Beginners should understand:

User and Group Membership

Windows uses users and groups to control access to resources. Membership in certain administrative or powerful groups can significantly change what an account can do.

Services

Windows services frequently run in privileged security contexts. A poorly configured service can become a security weakness if a lower-privileged user can improperly influence how that service operates.

File and Registry Permissions

Windows uses access control mechanisms to determine who can read, modify or execute resources. Weak permissions on sensitive files, directories or configuration information can create opportunities for unauthorized access.

Scheduled Tasks

Scheduled tasks can execute automatically under particular accounts or security contexts. Incorrect permissions surrounding a scheduled task can therefore create a privilege boundary problem.

Credentials and Secrets

Passwords, tokens, configuration files and other secrets should never be unnecessarily exposed to low-privileged users.

During an authorized assessment, testers look for situations where sensitive authentication material is stored or exposed incorrectly.

Common Privilege-Escalation Weaknesses

Although every operating system is different, several recurring categories appear in security assessments:

  1. Weak permissions
  2. Misconfigured services
  3. Excessive administrative privileges
  4. Unpatched software
  5. Exposed credentials or secrets
  6. Insecure scheduled tasks
  7. Poorly configured applications
  8. Weak separation between users and resources
  9. Unsafe scripts or automation
  10. Improper access-control design

Notice that many of these are configuration problems rather than sophisticated software vulnerabilities. That is an important lesson for beginners. Security is often broken by ordinary components that have been configured incorrectly.

A Beginner’s Privilege-Escalation Methodology

Instead of memorizing hundreds of techniques, develop a repeatable process.

Step 1: Identify Your Current Context

Determine which account, groups, permissions and security context you currently have.

Step 2: Understand the System

Identify the operating system, installed applications, running services, network configuration and important directories.

Step 3: Review Permissions

Look for resources that your current account can access or modify.

Step 4: Look for Misconfigurations

Focus on excessive privileges, writable sensitive resources, insecure services, exposed credentials and weak access controls.

Step 5: Research the Finding

If you discover an unusual configuration or vulnerable component, research its security implications using trusted documentation and vulnerability databases.

Step 6: Validate Safely

In an authorized laboratory, determine whether the suspected weakness actually crosses a privilege boundary.

Step 7: Document Everything

Record the original privilege level, the weakness discovered, the security impact and the recommended remediation.

This methodology is more valuable than memorizing a collection of commands.

How Beginners Can Practice Safely

The best way to learn privilege escalation is through deliberately vulnerable environments. Create an isolated virtual lab containing systems you control. Beginner-friendly cybersecurity training platforms and vulnerable virtual machines can also provide structured exercises.

Your goal should not simply be:
“How do I become administrator?”

Instead, ask:

“Why was the privilege boundary weak?”

That question develops a much stronger security mindset.

For example, if a lab demonstrates an insecure service configuration, investigate why the service had excessive privileges, what permission allowed the lower-privileged account to influence it and how an administrator could correct the problem.

How to Prevent Privilege Escalation

Learning offensive security should also teach you how to defend systems.

Organizations can reduce privilege-escalation risk by:

  • Applying security updates regularly
  • Following the principle of least privilege
  • Reviewing administrator and group memberships
  • Restricting service permissions
  • Protecting credentials and secrets
  • Monitoring privileged activity
  • Removing unnecessary software and services
  • Reviewing file and registry permissions
  • Separating administrative accounts from normal accounts
  • Auditing configuration changes

Least privilege is particularly important. Users and applications should receive only the permissions they actually need.

What Beginners Should Learn Next

Privilege escalation sits at the intersection of several important cybersecurity fundamentals.

A useful learning sequence is:

Networking → Linux → Windows → Permissions → Authentication → Enumeration → Vulnerability Management → Privilege Escalation → Active Directory → Security Reporting

You don’t need to master everything at once. Start with operating-system fundamentals. Learn how users, groups, processes, services, files, permissions and authentication work.

Then practice identifying security weaknesses in controlled environments. Eventually, privilege escalation becomes less about memorizing tricks and more about recognizing relationships between users, permissions, processes, services, applications and resources.

Conclusion

Privilege escalation is an essential skill for anyone learning ethical hacking. The most important lesson for beginners is that privilege escalation isn’t simply about finding a clever exploit. It is about understanding why a system allows one security boundary to be crossed.
A strong ethical hacker can look at a system and reason about permissions, trust relationships, configuration, and security controls.

Build that foundation first.
Practice only in authorized environments.
Document what you discover.

And most importantly, learn both sides of the problem: how privilege boundaries can fail and how administrators can build stronger ones.

That is what turns privilege escalation from a collection of hacking tricks into a genuine cybersecurity skill.