Ethical hacking continues to attract thousands of beginners every year. The idea sounds exciting: learn hacking, find vulnerabilities, work remotely, earn a good salary and ofcourse become a cybersecurity professional. But there is a side of the ethical hacking career that social media videos and short courses often don’t show.
Becoming a professional ethical hacker takes more than learning Kali Linux, running Nmap scans or collecting penetration-testing tools. The cybersecurity industry is changing quickly and employers increasingly expect practical skills, strong fundamentals, communication ability and an understanding of how modern IT environments actually work.
So, what should beginners realistically expect from an ethical hacking career in 2027?
Let’s take a practical look.
New to Ethical Hacking?
Start your journey with The Beginner Ethical Hacker Starter Kit (2026 Edition).
Inside the free guide, you’ll learn:.
- Ethical hacking fundamentals
- Beginner cybersecurity roadmap
- Essential hacking tools
- Common vulnerabilities explained
What Does an Ethical Hacker Actually Do?
An ethical hacker is a cybersecurity professional who is authorized to identify weaknesses in systems, applications, networks, cloud environments or other technology. The goal isn’t simply to “hack” something.
The goal is to help an organization understand where security weaknesses exist and how those weaknesses can be reduced or fixed.
Depending on the role, an ethical hacker may work on:
- Web application security
- Network penetration testing
- Internal security assessments
- Cloud security testing
- Mobile application security
- API security
- Active Directory security
- Vulnerability assessments
- Red-team exercises
- Security research
- Bug bounty programs
A professional engagement usually involves much more than technical testing. Scope, authorization, documentation, evidence collection, risk analysis, communication and reporting are all important.
That is one of the first realities beginners should understand. Professional ethical hacking is a security job, not simply a collection of hacking tricks.
Reality #1: Learning Tools Is Not the Same as Learning Hacking
One of the biggest beginner mistakes is believing that mastering security tools automatically creates a cybersecurity career. A beginner might learn Nmap, Burp Suite, Wireshark, Metasploit, Gobuster, Nikto or other popular tools.
That is useful but tools are only part of the picture. For example, knowing how to launch a network scan is less valuable if you don’t understand what the discovered ports and services mean.
Similarly, knowing how to use a web proxy is much less useful if you don’t understand HTTP, cookies, sessions, authentication, authorization, APIs and common web application architectures.
In 2027, beginners should think beyond tools. Learn the technology first. Then learn how security professionals analyze it.
Reality #2: Networking Fundamentals Still Matter
Cybersecurity changes constantly but networking remains fundamental.
You don’t need to become a network engineer before entering cybersecurity but you should understand concepts such as:
- IP addresses
- TCP and UDP
- Ports
- DNS
- HTTP and HTTPS
- Routing
- NAT
- Firewalls
- VPNs
- Network segmentation
- Common network services
These concepts help you understand what security tools are actually showing you.
When an Nmap scan identifies an open service, for example, your next question shouldn’t simply be “Which tool do I run next?”
Instead, ask:
What is this service, why is it exposed, what does it normally do and what security risks could be associated with it?
That mindset is much closer to professional security work.
Reality #3: Web Security Is Extremely Valuable
Web applications and APIs remain important areas of cybersecurity. For beginners, web security can provide an excellent learning path because it combines technical concepts with practical experimentation.
You should understand:
- HTTP requests and responses
- Cookies
- Sessions
- Authentication
- Authorization
- Input validation
- APIs
- Access control
- Common web vulnerabilities
- Secure application design
Training platforms and intentionally vulnerable applications can provide safe environments for learning these concepts. The important point is to practice only within systems where you have explicit permission.
Reality #4: Cloud Security Is Becoming Increasingly Important
Modern organizations increasingly depend on cloud infrastructure. That means future security professionals need to understand environments such as AWS, Azure and other cloud platforms. However, cloud security isn’t simply traditional penetration testing performed against a cloud server.
Cloud environments introduce concepts such as:
- Identity and access management
- Cloud storage
- Roles and permissions
- Virtual networks
- Security groups
- Logging
- Monitoring
- Secrets
- Containers
- Serverless services
- Infrastructure as code
A beginner doesn’t need to master every cloud technology immediately but understanding basic cloud architecture can significantly expand your cybersecurity knowledge.
Reality #5: Active Directory Knowledge Can Be Valuable
Many organizations still operate Windows-based enterprise environments. That makes identity and directory technologies important areas for security professionals to understand.
Beginners should learn concepts such as:
- Users
- Groups
- Organizational Units
- Domain Controllers
- Domains
- Forests
- Authentication
- Authorization
- Group Policy
- Kerberos
- LDAP
- Privileged accounts
The goal isn’t to memorize attack commands. Instead, understand how enterprise identity works and where security weaknesses can appear. This foundation is useful for both offensive and defensive cybersecurity roles.
Reality #6: You Will Spend More Time Reading Than You Expect
Cybersecurity has a huge amount of documentation. Professional security researchers regularly read:
- Technical documentation
- Security advisories
- Vulnerability disclosures
- Research papers
- Vendor documentation
- Application documentation
- Configuration guides
- Incident reports
Sometimes the solution to a problem isn’t another tool. It’s reading the documentation carefully. Developing this habit early can give beginners an advantage because cybersecurity knowledge changes continuously.
Reality #7: Certifications Can Help but They Are Not Magic
Certifications can be useful for demonstrating structured learning. They may also help candidates get past certain recruitment filters but certification alone doesn’t prove that someone can perform professional security work.
A candidate who has completed a certification but has never built a lab, investigated a vulnerability, documented findings or explained security risks may still struggle during practical interviews. A stronger approach is to combine structured learning with practical experience.
For example:
Learn → Build → Practice → Document → Explain
Create controlled labs.
Practice security concepts.
Document what you discovered.
Write short technical reports.
Explain the security impact in simple language.
This creates evidence of practical learning.
Want to Learn Ethical Hacking Step-by-Step?
If you’re serious about learning cybersecurity, a structured roadmap makes the journey much easier.
Download The Beginner Ethical Hacker Starter Kit (2026 Edition) and discover:
✔ The ethical hacking learning path
✔ Beginner-friendly security concepts
✔ Essential tools ethical hackers use
✔ The most common vulnerabilities explained
Reality #8: Your First Cybersecurity Job May Not Be “Ethical Hacker”
This is an important reality for beginners.
Many people imagine their first job will have a title such as:
Penetration Tester
But cybersecurity careers are broader than that.
Your first role might involve:
- Security operations
- Vulnerability management
- Security monitoring
- IT support
- Network administration
- System administration
- Application security
- Cloud security
- Governance and compliance
- Security testing
These roles can provide experience that eventually leads toward penetration testing or red teaming. Don’t become too focused on a job title. Focus on building transferable security skills.
Reality #9: Communication Is a Cybersecurity Skill
Technical knowledge is important but professional security work also involves communication. Imagine discovering a serious vulnerability.
You might need to explain:
- What the issue is
- Where it exists
- Why it matters
- What systems are affected
- What evidence supports the finding
- What the potential impact is
- How the organization can reduce the risk
Your audience may not be a security expert. Therefore, being able to explain technical problems clearly is extremely valuable. A great security professional isn’t simply someone who finds vulnerabilities. They can also communicate what those vulnerabilities mean.
Reality #10: AI Will Change Cybersecurity Jobs
Artificial intelligence will increasingly affect cybersecurity work. AI tools can already assist with activities such as summarizing information, analyzing large amounts of data, generating drafts, explaining technical concepts and supporting security workflows.
By 2027, cybersecurity professionals will likely need to become comfortable working alongside AI-assisted tools but that doesn’t mean cybersecurity knowledge becomes unnecessary. In fact, understanding fundamentals becomes even more important.
If an AI system produces an incorrect technical conclusion, a knowledgeable security professional needs to recognize the mistake. Think of AI as an accelerator rather than a replacement for understanding.
Reality #11: Bug Bounty Is Not a Guaranteed Career
Bug bounty programs can be an excellent way to learn web security. They can teach researchers how to analyze applications, understand vulnerabilities, document findings and communicate with security teams.
However, beginners should avoid treating bug bounty hunting as guaranteed income. Finding valid vulnerabilities can take significant time and requires strong technical skills. Bug bounty should initially be viewed as a learning and research activity rather than a guaranteed paycheck. Always follow program scope and rules.
Reality #12: You Need a Portfolio
One of the strongest ways for beginners to demonstrate practical knowledge is through a portfolio.
Your portfolio could contain:
- Lab projects
- Security write-ups
- Vulnerability reports from authorized environments
- Network diagrams
- Web security research
- Detection experiments
- Security scripts
- CTF write-ups
- Cloud security labs
- Documentation projects
Never publish confidential information or unauthorized security findings. The goal is to demonstrate how you think. A simple project showing that you understand a security concept can be more informative than a long list of tools.
Reality #13: Continuous Learning Is Part of the Job
Cybersecurity is not a career where you learn everything once and stop.
New technologies appear. New vulnerabilities are discovered. Cloud platforms change. Attack techniques evolve. Security controls improve. That means continuous learning is part of the profession.
A sustainable learning routine could include:
30% fundamentals
30% hands-on labs
20% security research
10% documentation
10% communication and reporting
The exact percentages aren’t important. The principle is. Balance theory with practical experience.
What Should Beginners Learn Before 2027?
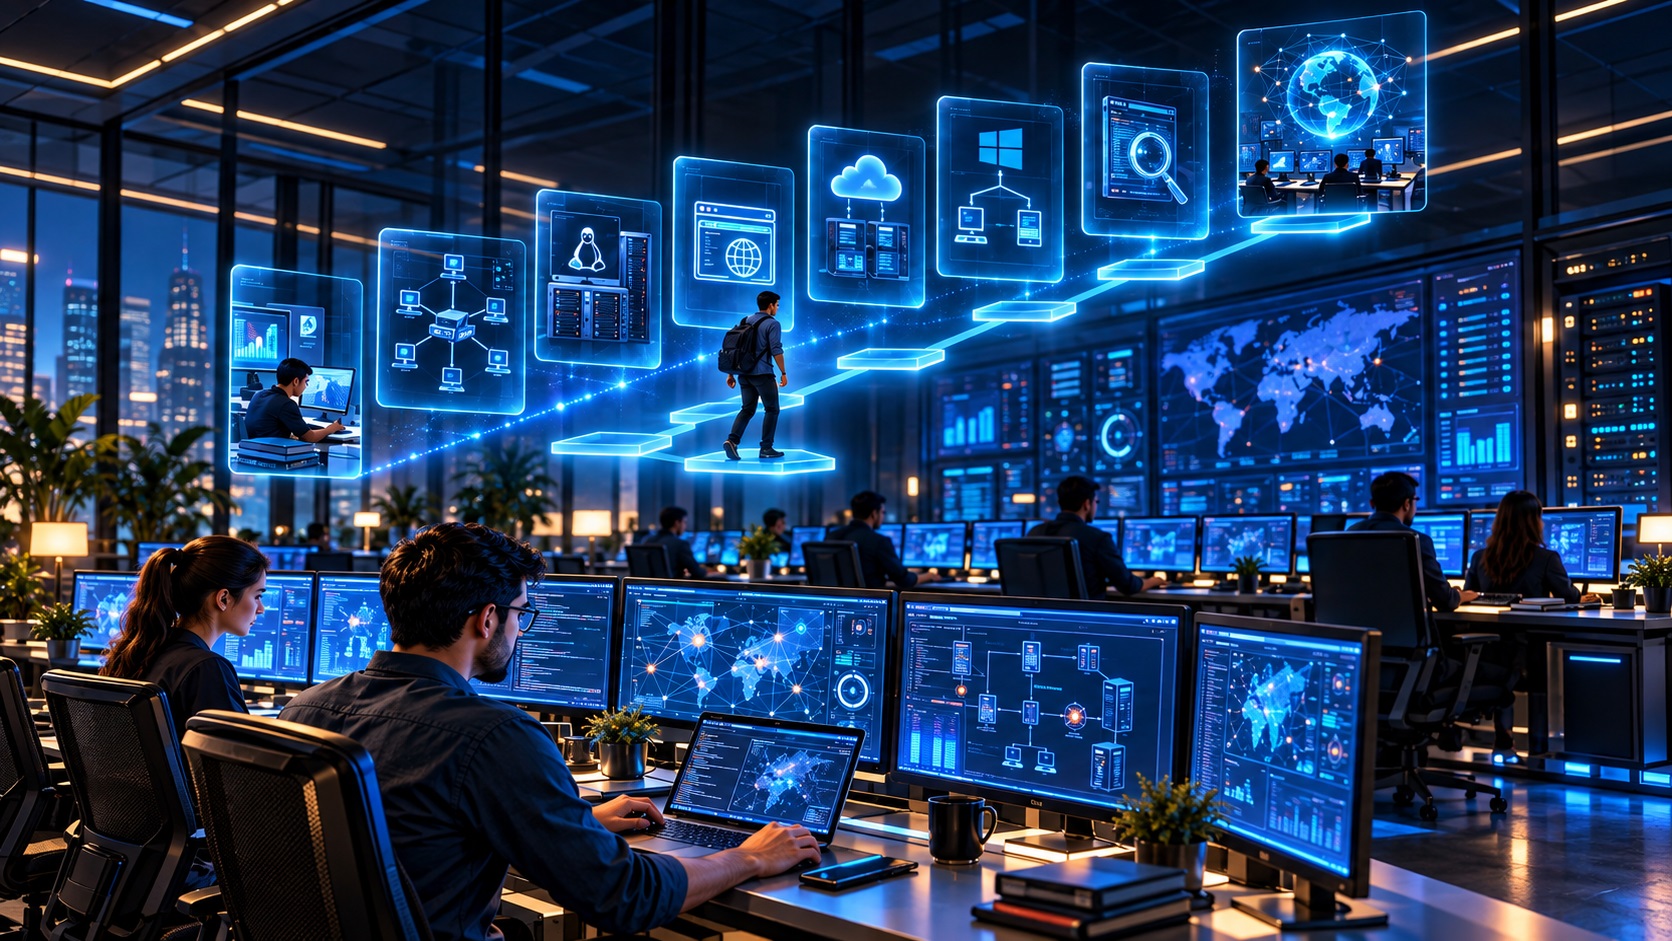
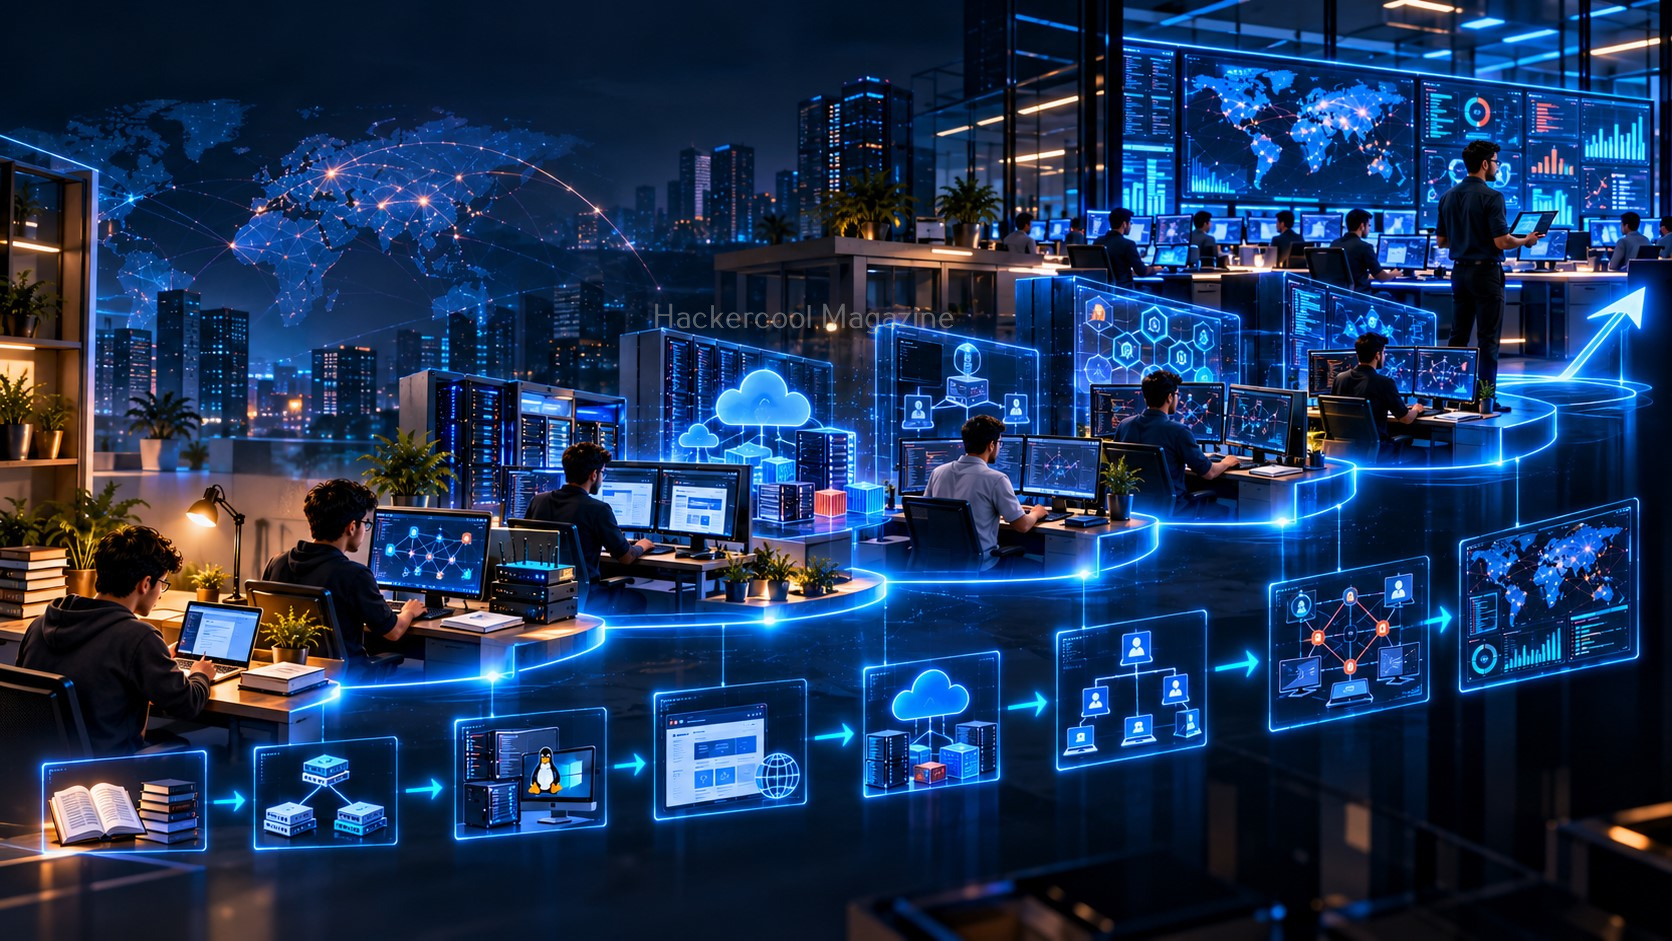
If you’re starting an ethical hacking journey, consider building your knowledge in this order:
Step 1: Computer Fundamentals
Understand operating systems, files, processes, users, permissions and basic troubleshooting.
Step 2: Networking
Learn IP addressing, TCP/IP, DNS, HTTP, ports, routing and common network services.
Step 3: Linux and Windows
Become comfortable working with both operating systems.
Step 4: Web Technologies
Learn how browsers, servers, APIs, authentication and databases interact.
Step 5: Security Fundamentals
Study vulnerabilities, threats, risk, authentication, authorization, encryption, logging and security controls.
Step 6: Hands-On Practice
Build an isolated home lab or use authorized cybersecurity training platforms.
Step 7: Choose a Specialization
You could explore:
- Web security
- Network security
- Cloud security
- Active Directory security
- Red teaming
- Application security
- Vulnerability research
- Security operations
Step 8: Build a Portfolio
Document your projects and demonstrate what you learned.
Step 9: Develop Communication Skills
Practice writing clear technical reports and explaining security concepts.
So, Is Ethical Hacking Still a Good Career to Explore in 2027?
The cybersecurity industry will continue to need people who can understand technology and security risks but beginners should enter the field with realistic expectations.
Ethical hacking isn’t about memorizing hundreds of commands.
It isn’t about collecting every hacking tool.
It isn’t about becoming an expert overnight
and it certainly isn’t about hacking random websites.
A sustainable cybersecurity career is built on fundamentals, hands-on practice, curiosity, communication, ethical behavior and continuous learning. If you enjoy understanding how technology works, investigating problems, learning continuously and thinking from both an attacker and defender perspective, ethical hacking can be a rewarding area to explore.
Start small.
Build a legal lab.
Learn the fundamentals.
Practice consistently.
Document your progress and remember one of the most important rules in cybersecurity:
Only test systems when you have explicit permission to do so.
That’s the reality check beginners need before starting an ethical hacking career in 2027.
Start Your Ethical Hacking Journey Today
Learning cybersecurity can feel overwhelming at first. The best way to start is with a clear roadmap and the right resources.
Download The Beginner Ethical Hacker Starter Kit (2026 Edition) and get instant access to:
Ethical Hacking Fundamentals
A beginner cybersecurity learning roadmap
Essential hacking tools every beginner should know
Common vulnerabilities explained simply