One of the first questions beginners ask when they discover ethical hacking is:
“How long will it take me to learn ethical hacking?”
On Internet, you may see claims that someone can become an ethical hacker in 30 days, 60 days or six months. Other people suggest that it takes years. The reality is more complicated.
There is no single timeline for learning ethical hacking because ethical hacking is not one skill. It combines networking, operating systems, web technologies, programming, security concepts, vulnerability assessment, penetration testing, cloud environments, identity systems and communication skills.
You can learn the fundamentals relatively quickly. Becoming comfortable performing security assessments takes considerably longer. Becoming an experienced security professional is a continuous process. The good news is that you do not need to master everything before you begin practicing. Instead, think of ethical hacking as a progression of skills.
New to Ethical Hacking?
Start your journey with The Beginner Ethical Hacker Starter Kit (2026 Edition).
Inside the free guide, you’ll learn:.
- Ethical hacking fundamentals
- Beginner cybersecurity roadmap
- Essential hacking tools
- Common vulnerabilities explained
What Does “Learn Ethical Hacking” Actually Mean?
Before discussing timelines, it is important to define what “learn ethical hacking” means.
For a beginner, it might mean understanding basic security concepts and completing guided labs. For someone preparing for a cybersecurity job, it might mean being able to analyze a system, identify vulnerabilities, document findings and explain remediation.
For an experienced penetration tester, it may involve assessing complex enterprise environments, cloud infrastructure, web applications, Active Directory, APIs and other systems. These are very different levels of ability.
Therefore, instead of asking:
“How many months does ethical hacking take?”
A better question is:
“What should I be able to do after each stage of learning?”
That gives you a much more realistic roadmap.
A Realistic Ethical Hacking Learning Timeline
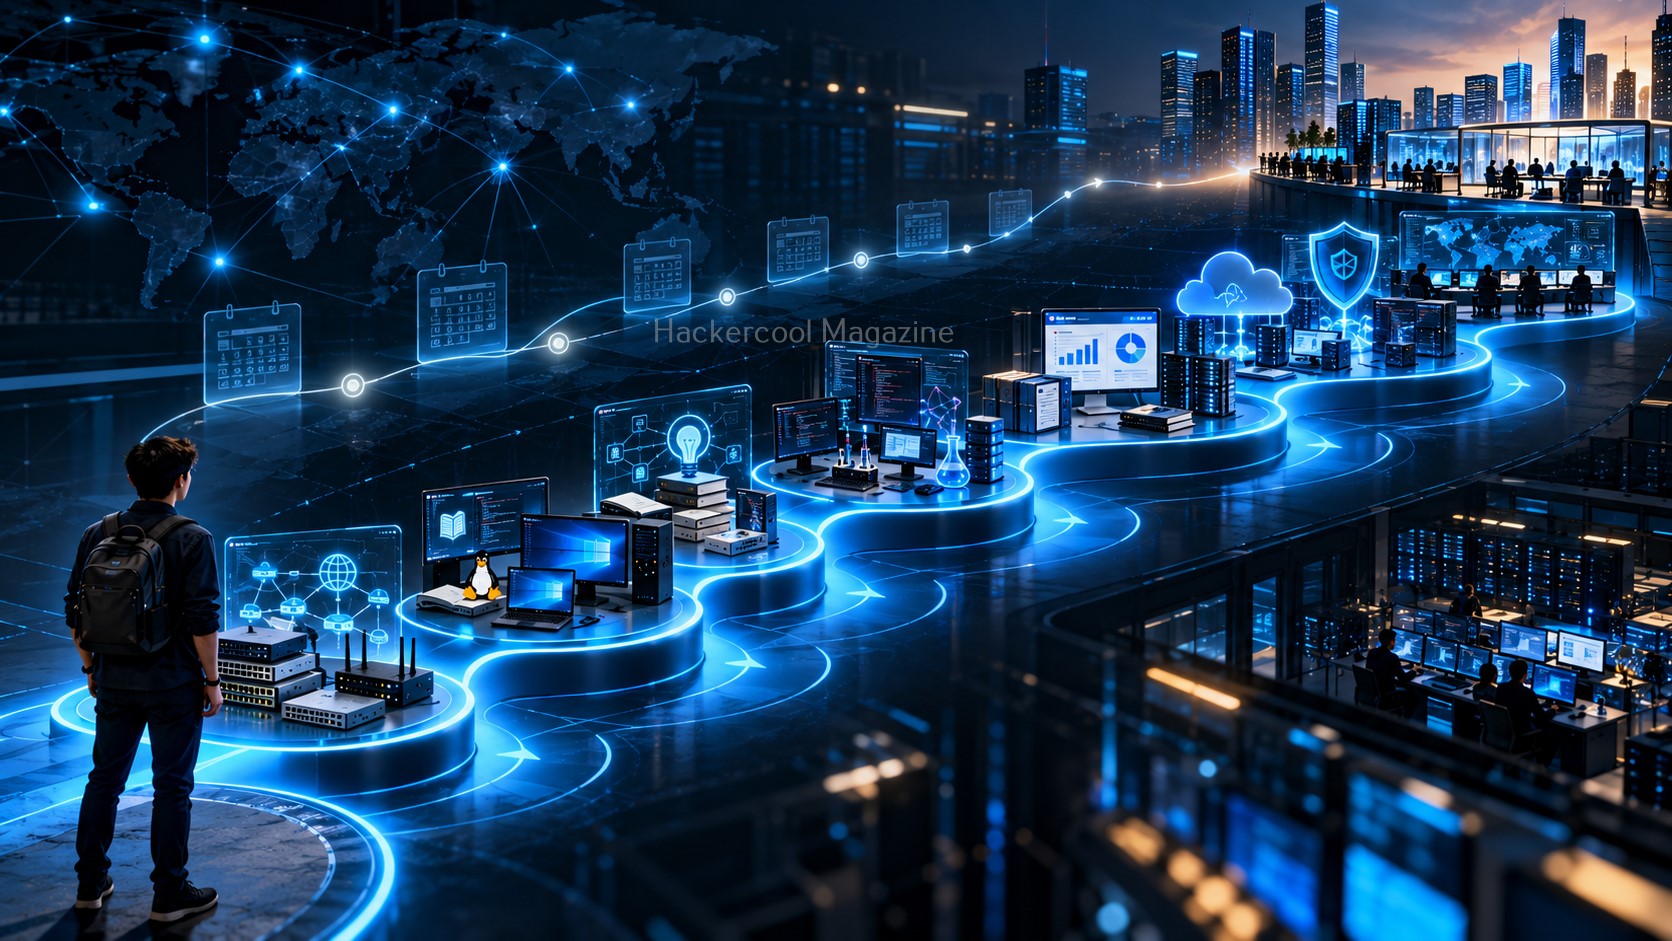
For someone starting from the beginning and studying consistently, a reasonable progression might look like this:
| Learning stage | Approximate timeframe | Main focus |
| Foundations | 1–2 months | Networking, Linux, Windows, Web Basics |
| Security fundamentals | 2–4 months | Authentication, vulnerabilities, security concepts |
| Hands-on practice | 3–6 months | Labs, enumeration, vulnerability assessment |
| Beginner penetration testing | 6–12 months | Structured security assessments |
| Job-ready development | 9–18+ months | Portfolio, reporting, specialization |
| Professional growth | 1–3+ years | Enterprise environments and specialization |
These are learning estimates, not guarantees.
Someone studying several hours every day may progress differently from someone studying for five hours per week. Previous IT experience also makes a major difference. The important thing is to measure progress by capability, not by the calendar.
Stage 1: Build Your Foundations
Approximate timeframe: 1–2 months
Many beginners make the mistake of starting with hacking tools immediately. You might install Kali Linux, open Nmap, learn a few commands and feel like you are already learning ethical hacking but tools make much more sense when you understand the technology they are examining. So, start with fundamentals.
Networking
Learn concepts such as:
- IP addresses
- TCP and UDP
- Ports
- DNS
- HTTP and HTTPS
- Routing
- Subnets
- Firewalls
- NAT
- Common network protocols
You do not need to become a network engineer. You need enough networking knowledge to understand what is happening when systems communicate.
Linux
Learn:
- Files and directories
- Users and groups
- Permissions
- Processes
- Services
- Package management
- Shell basics
- Logs
Windows
Understand:
- Users and groups
- Processes
- Services
- File permissions
- Windows administration
- Event logs
- Basic Active Directory concepts
Web Fundamentals
Learn how browsers communicate with servers.
Understand:
- Requests and responses
- HTTP methods
- Headers
- Cookies
- Sessions
- Authentication
- Databases
- APIs
- Basic JavaScript concepts
These foundations may seem less exciting than hacking tools but they become extremely valuable later.
Stage 2: Learn Security Fundamentals
Approximate timeframe: 2–4 months
Once you understand basic technology, start learning how security problems occur.
Important concepts include:
- Authentication
- Authorization
- Access control
- Encryption
- Hashing
- Vulnerability management
- Security misconfiguration
- Input validation
- Logging and monitoring
- Common web vulnerabilities
- Network security
- Endpoint security
You should begin thinking like both an attacker and a defender. For example, don’t simply learn that weak access control can be dangerous.
Ask:
Why does the application trust this user?
What resource is being protected?
Which permission is missing?
How could an administrator prevent the problem?
This mindset is more valuable than memorizing a list of vulnerabilities.
Stage 3: Start Hands-On Practice
Approximate timeframe: 3–6 months
This is where theoretical knowledge begins turning into practical skill. Use intentionally vulnerable systems and authorized training environments.
Your practice should include activities such as:
- Network discovery
- Service identification
- Web application testing
- Authentication testing
- Vulnerability identification
- Basic privilege analysis
- Security configuration review
- Log analysis
- Writing findings
Beginner-friendly cybersecurity training platforms can help provide structured exercises. You can also build your own isolated virtual lab using systems designed specifically for security testing. The goal is not simply to complete as many labs as possible.
After each exercise, ask:
What vulnerability existed?
Why did it exist?
How could it be detected?
How could it be fixed?
That turns a lab exercise into actual learning.
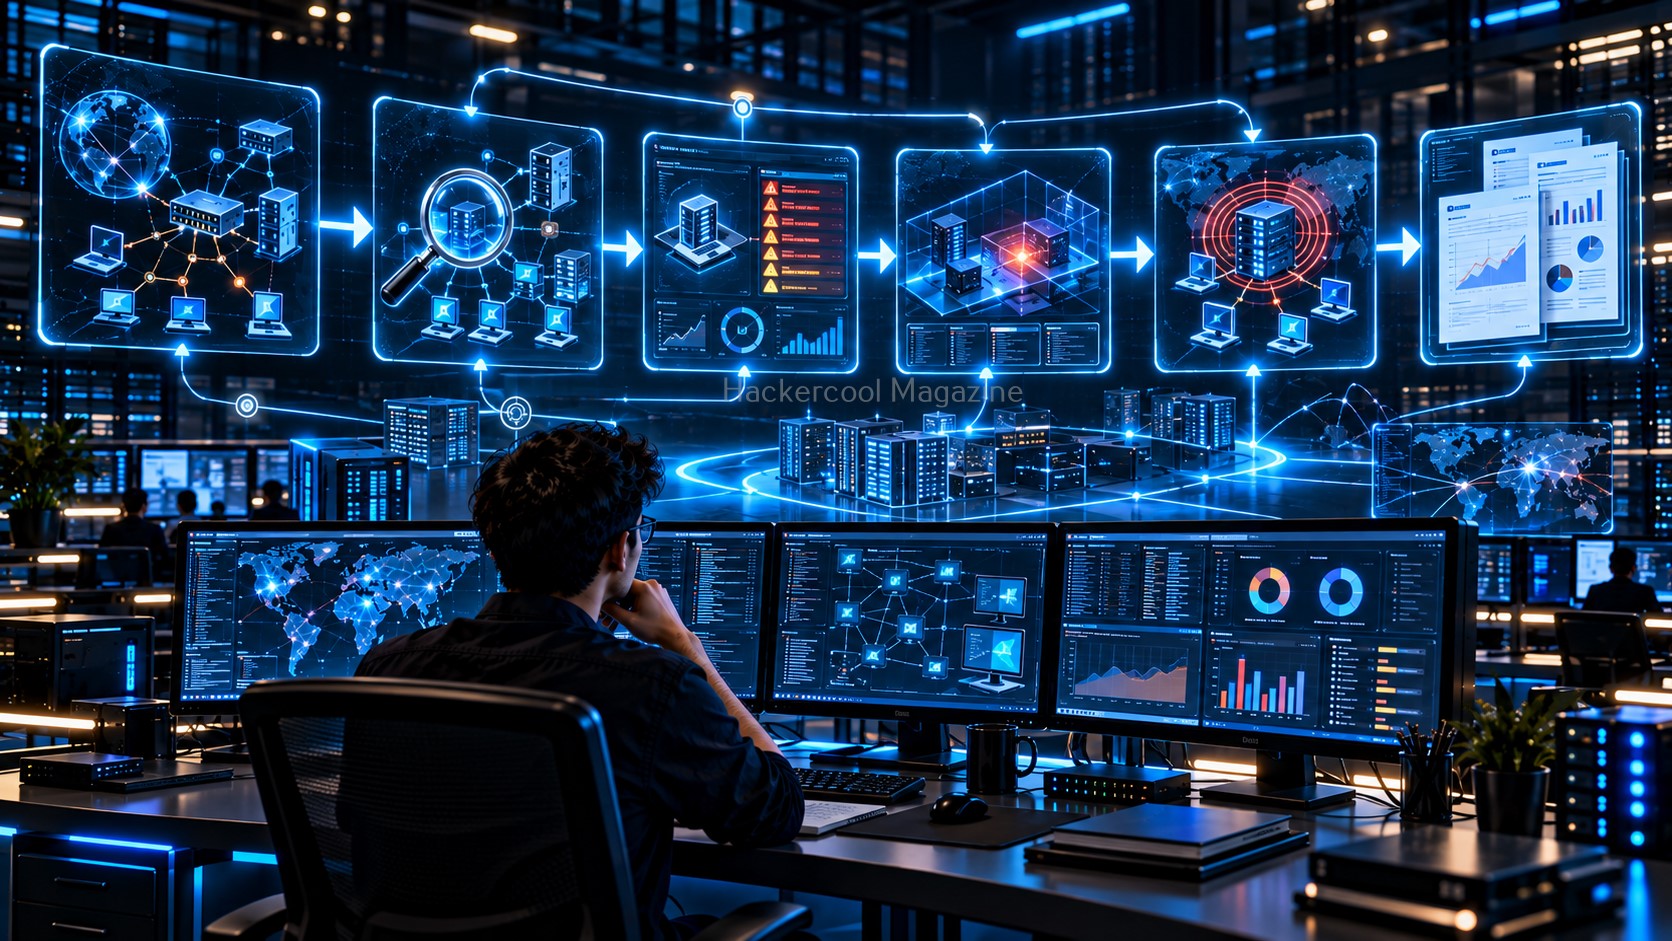
Stage 4: Learn a Basic Penetration-Testing Methodology
Approximate timeframe: 6–12 months
At this stage, you should stop thinking about individual tools and start thinking about complete assessments.
A simplified penetration-testing workflow might look like:
Reconnaissance → Enumeration → Vulnerability Analysis → Validation → Impact Assessment → Reporting
You should understand why each stage exists. For example, enumeration is not simply about running a particular scanner. It is about building an understanding of the target environment.
Similarly, vulnerability assessment isn’t simply about finding a CVE. You need to determine whether a finding is relevant, what its impact could b and how it should be remediated. This is where your skills begin moving from tool usage toward security assessment.
Stage 5: Develop a Portfolio
Approximate timeframe: 6–12+ months
A portfolio can demonstrate what you actually know.
Instead of simply writing:
“I know Nmap, Burp Suite, Linux and Metasploit.”
Show what you have built and learned.
For example,
Project 1: Network Security Lab
Document a controlled lab where you mapped systems and analyzed exposed services.
Project 2: Web Security Assessment
Create a report based on an intentionally vulnerable web application.
Explain:
- Finding
- Risk
- Evidence
- Impact
- Remediation
Project 3: Windows Security Lab
Build a small Windows environment and document users, groups, permissions, services and security configurations.
Project 4: Active Directory Lab
Create an authorized lab demonstrating identity relationships and common security weaknesses. The quality of your documentation matters. A professional who can identify a security issue and explain it clearly is much more valuable than someone who can simply run a tool.
Want to Learn Ethical Hacking Step-by-Step?
If you’re serious about learning cybersecurity, a structured roadmap makes the journey much easier.
Download The Beginner Ethical Hacker Starter Kit (2026 Edition) and discover:
✔ The ethical hacking learning path
✔ Beginner-friendly security concepts
✔ Essential tools ethical hackers use
✔ The most common vulnerabilities explained
Can You Become Job-Ready in Six Months?
Possibly—but the phrase “job-ready” needs context.
Six months of consistent study can give a motivated beginner a solid foundation and meaningful hands-on experience. However, it does not automatically mean that the person is ready for every penetration-testing position. Your starting point matters.
Someone with networking, Linux, system administration or software-development experience may progress faster because many concepts are already familiar. Someone completely new to computers may need considerably more time.
A better six-month goal is:
“Can I demonstrate measurable technical progress?”
For example,
Can you explain networking?
Can you work comfortably in Linux?
Can you understand Windows permissions?
Can you analyze a web request?
Can you perform a structured lab assessment?
Can you write a professional vulnerability report?
Those questions provide much better indicators of progress.
What About Becoming an Ethical Hacker in 30 Days?
Thirty-day ethical-hacking challenges can be useful as motivation but that is not a realistic timeframe for mastering ethical hacking. In 30 days, a beginner can learn the basics of networking, Linux, security concepts and some tools.
They can also complete introductory labs but ethical hacking involves a large technical landscape. Learning how a tool works is different from understanding the technology that tool is examining. Treat short challenges as starting points, not promises of professional mastery.
How Many Hours a Day Should You Study?
Consistency matters more than extreme study schedules.
For example:
5 hours per week
Can produce steady progress if maintained consistently.
10 hours per week
Provides considerably more time for theory and practical labs.
15–20 hours per week
Can accelerate progress significantly, provided the learning is structured and sustainable. You do not need to study for eight hours every day. A focused one-hour session can be valuable if you use it to solve a specific problem, complete a lab, read documentation or analyze something you previously didn’t understand.
Why Some Beginners Progress Faster
Several factors affect learning speed.
Previous Technical Experience;
Someone who already understands Linux, networking, programming or system administration has a significant foundation.
Consistency
Studying two hours every weekend is very different from studying for one hour several days per week.
Hands-On Practice
Reading about security is useful. Actually configuring systems and analyzing them is different.
Quality of Learning
Completing 20 labs without understanding them is less valuable than completing 10 labs and understanding why each vulnerability existed.
Ability to Troubleshoot
You will encounter errors constantly. Learning how to search documentation, read error messages, test assumptions and troubleshoot independently is a major cybersecurity skill.
When Should You Start Using Security Tools?
You don’t have to wait until you have mastered every fundamental. Start using tools while learning the underlying technology.
For example:
Learn networking → use a network-analysis tool.
Learn web protocols → study web requests.
Learn Linux → explore Linux administration and security.
Learn vulnerability management → analyze vulnerabilities in an authorized lab.
This creates a powerful learning loop:
Learn → Practice → Make Mistakes → Investigate → Understand → Practice Again
That cycle is much more effective than simply memorizing commands.
Certifications Can Help—but They Are Not the Whole Journey
Certifications can provide structure and demonstrate knowledge, depending on the certification and role. Beginners may encounter certifications covering areas such as networking, cybersecurity fundamentals, penetration testing or offensive security.
But a certificate should complement practical experience. If you have a certification but cannot explain basic networking, permissions, authentication or vulnerability management, there is still a significant skills gap.
Think of certifications as one component of your development:
Knowledge + Practice + Projects + Communication + Professionalism
Together, these create a stronger foundation.
Ethical Hacking Is a Continuous Learning Career
Even experienced cybersecurity professionals continue learning.
Technology changes.
Cloud platforms evolve.
Operating systems receive new features.
Applications introduce new architectures.
Attack techniques change.
Defensive controls improve.
Artificial intelligence is also changing how security teams analyze systems and how attackers and defenders approach problems.
This means there isn’t really a final point where you can say:
“I have finished learning ethical hacking.”
Instead, your goal should be to continuously expand your capabilities. You might begin with web applications. Later, you may explore Active Directory. Then cloud security. Then APIs, containers, identity systems, mobile applications or red teaming.
You don’t need to learn everything. Choose areas that match your interests and career goals.
A Realistic Beginner Roadmap
If you are starting from zero, a practical progression could look like this:
Months 1–2
Networking + Linux + Windows fundamentals
Months 3–4
Security concepts + web fundamentals + basic security tools
Months 5–6
Hands-on labs + enumeration + vulnerability assessment
Months 7–9
Web security + Windows security + privilege concepts + reporting
Months 10–12
Portfolio projects + specialization + interview preparation
After the first year, continue developing deeper skills in areas such as:
- Active Directory
- Cloud security
- Web application security
- API security
- Red teaming
- Vulnerability management
- Security operations
Again, these are approximate milestones rather than promises. Your own starting point, available study time, learning methods and technical background will influence the timeline.
Conclusion
So, how long does it take to learn ethical hacking?
You can learn the fundamentals in a few months.
You can develop meaningful hands-on skills over six to twelve months of consistent practice.
You can continue developing professional-level capabilities over several years.
But there is no magic number.
The most useful way to measure your progress is not:
“How many months have I been studying?”
Instead ask:
“What can I understand and do today that I couldn’t do three months ago?”
If you can explain how networks work, understand Linux and Windows permissions, analyze web applications, identify vulnerabilities in an authorized lab, document your findings and explain how those vulnerabilities can be fixed, you are making real progress.
Start with the fundamentals.
Practice regularly.
Build projects.
Document your work.
Learn from your mistakes
and always practice ethical hacking only on systems you own or have explicit permission to test.
Ethical hacking is not a race to learn the most tools. It is a long-term process of learning how technology works, how security boundaries fail, and how those boundaries can be strengthened.
Start Your Ethical Hacking Journey Today
Learning cybersecurity can feel overwhelming at first. The best way to start is with a clear roadmap and the right resources.
Download The Beginner Ethical Hacker Starter Kit (2026 Edition) and get instant access to:
Ethical Hacking Fundamentals
A beginner cybersecurity learning roadmap
Essential hacking tools every beginner should know
Common vulnerabilities explained simply